Cisco Secure Access Help

PDF

Cisco Secure Access Help

Add a Private Access Rule

Want to summarize with AI?

Log in

Describes Add a Private Access Rule in Cisco Secure Access. Cisco Secure Access connects users, devices, both public and branch networks, and network tunnels to private resources in your enterprise.


Cisco Secure Access connects users, devices, both public and branch networks, and network tunnels to private resources in your enterprise. Private resources are applications and services that you deploy on your enterprise's infrastructure or private cloud. When you add a private resource to your organization, Secure Access enables Branch network connections to the resource.

Once you add your sources and private resources to Secure Access, you can create private access rules with these source and destination components. For more information, see Components for Private Access Rules.

In a private access rule, add the source or destination components that you configured for your organization. You can also enter sources and destinations directly into your rules. These single-use source and destination components are only available on an access rule, not shared by your policy.

The access rule defines the Action, Source, Security Controls, and Destinations for the rule. In your private access rule's Security Controls, Secure Access provides a default Intrusion Prevention System (IPS) profile. You can configure and apply other IPS profiles for your Branch networks to Private Resources rules. For more information, see Get Started With Private Access Rules.
Geolocation Sources and Private Access Rules

Geolocation sources enable organizations to monitor and control the traffic from end users in specific geographic regions. The Geolocation source component is available on the internet and private access rules in the Access policy.

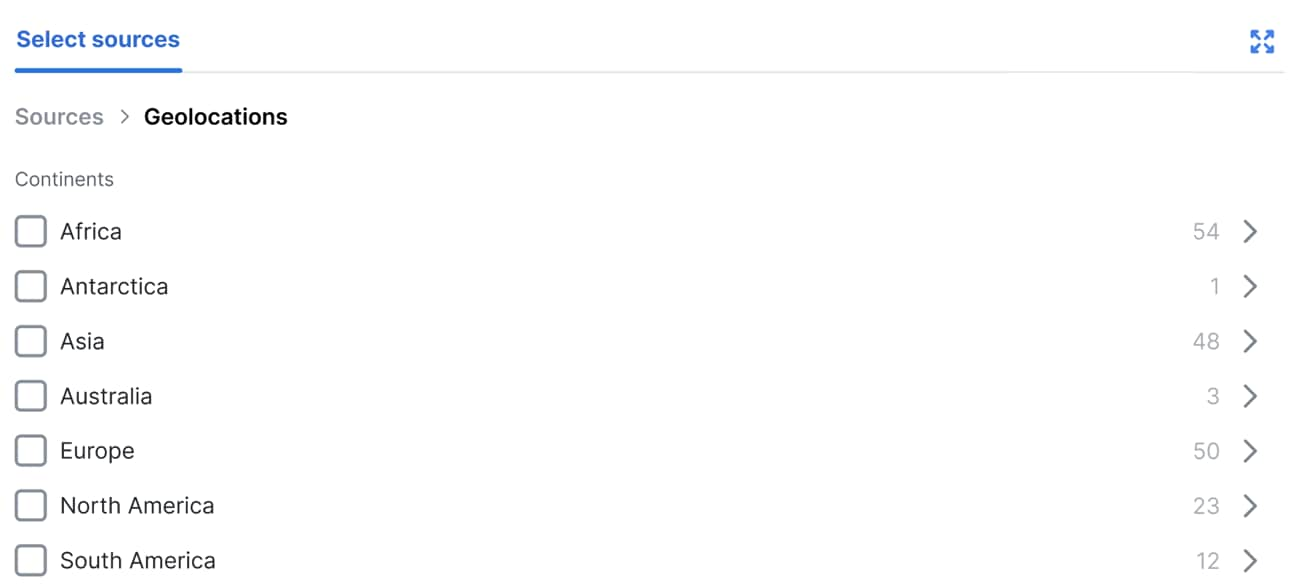
The Geolocation source component is a list of continents and the countries in these continents where Secure Access can manage the network traffic sent from these geographic locations.

You can select the Geolocation sources with the AD Users or AD Groups or only add the Geolocations on the access rules. Administrators of the organization are responsible for provisioning the AD Users and AD Groups. For more information, see Provision Users, Groups, and Endpoint Devices from Active Directory.

When you select the Geolocations on an access rule, Secure Access shows the AND option and the AD Users or AD Groups. When you select the AD Users and AD Groups for the source on an access rule, Secure Access shows the AND option and the list of continents and countries. Secure Access combines the selected AD Users or AD Groups and the geolocations with the boolean AND operator. You can only combine the Geolocation source component with the AD Users or AD Groups.

Monitoring Private Traffic from Geolocations

Set up the attributes and conditions on the access rules in the Access policy to monitor and protect the network traffic from the end users located in specific geographic regions. To enforce the security controls on a rule, the network traffic must match the selected sources.

For private access rules, choose to allow or block all traffic from the geolocations or all traffic from the selected AD Users or AD Groups located in the countries and continents.

  • The Secure Web Gateway (SWG) detects and enforces the web traffic (TCP/80, TCP/443) sent from the end users located in the selected continents and countries.

  • The Secure Access cloud-delivered firewall detects and enforces the network traffic on non-standard web ports sent from the end users located in the selected continents and countries.

  • For Zero Trust Access (ZTA) connections, the Secure Access cloud-delivered firewall detects and enforces the network traffic and the SWG proxies the traffic to the private destinations.

You can view the events and logs recorded by Secure Access for the traffic sent from the end users in the organization in certain geolocations. Secure Access reports on the traffic on standard web ports and non-web ports. For more information, see:


About Geolocation Sources

Sources on private access rules are either pre-configured or composite components. Pre-configured source components such as Registered Networks and Network Tunnel Groups acquire and manage the web traffic in your organization. You can select Geolocations sources on the access rules combined with any AD Users or AD Groups.

Note
DNS resolution does not is not supported in source based geolocation policies. The geolocation source of a DNS lookup is not an indicator of where content is being delivered and as such source based geolocation checks and matches are enforced at other enforcement layers as part of unified policy based on your policy configuration.

Composite sources may include IP addresses, CIDR blocks, and wildcard masks, and ports and port ranges.

If you see an option to Select All, this selects all existing items in the group at the time you select it, but the rule will not include items added to the group in the future.


Add Geolocation Sources on Private Access Rules

You can select Geolocation sources only on access rules or combine the Geolocation sources with AD Users or AD Groups using the boolean AND operator.

  • Add the Geolocation sources on the access rule, select the AND button, and then choose the AD Users and Groups.

  • Add pre-configured AD Users and Groups on the access rule, select the AND button, and then choose the Geolocation sources.

For information about Geolocation sources, see Geolocation Sources and Private Access Rules. For information about AD Users and AD Groups, see Manage Users, Groups, and Endpoint Devices.
Before you begin

Procedure

  1. Navigate to Secure > Access Policy.

  2. Navigate to the rules table and choose an existing access rule to edit, or add a new access rule in the Access policy.

  3. Navigate to Specify Access and then navigate to From.

  4. Navigate to Select sources > Geolocations, choose a continent, which selects all countries in the continent, or choose the countries in each continent.


    The Alert Rules Geolocations Source interface.
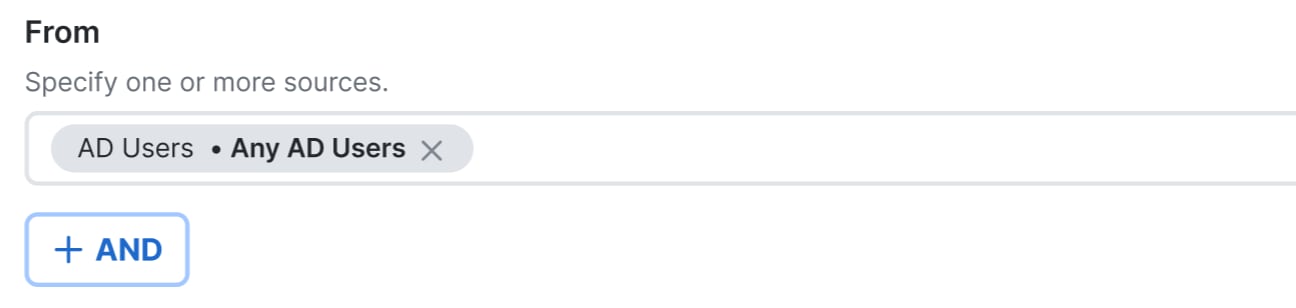
  5. (Optional) Click + AND and then add the AD Users or AD Groups.

    1. Navigate to Select sources, and then expand Users or Groups.
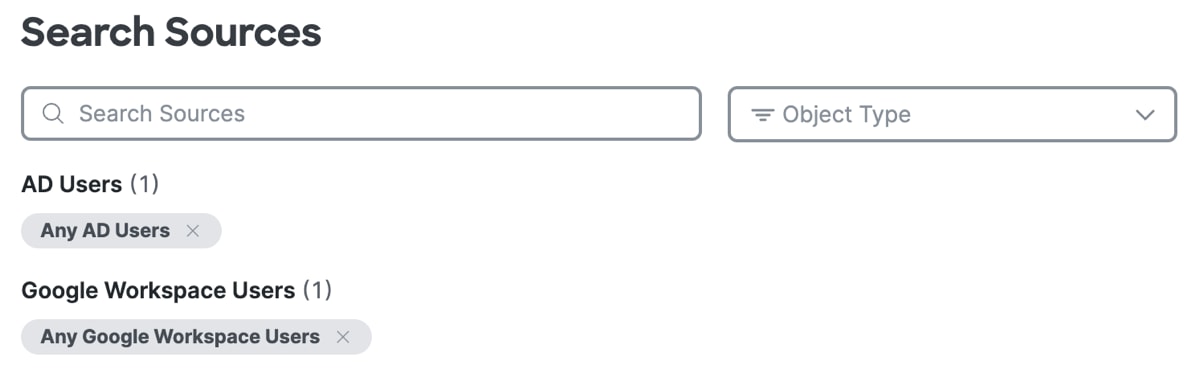
    2. Expand Users, and then select AD Users or select Any AD Users.

      The Alert Rules from AD User interface.
    3. Expand Groups, and then select AD Groups or select Any AD Groups.

Set Up the Private Access Rule


Enable the Rule and Edit Your Logging Settings

Enable your private access rule and edit the logging settings for the rule.

Procedure

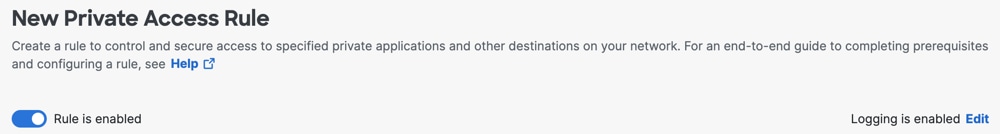
  1. Toggle on Rule is enabled to enable the access rule.

    After you configure and save the rule to your policy, the rule is enabled. You can toggle off the rule at any time to disable it.


    The Private Access Main Controls interface.
  2. Click Edit to manage your logging settings on the access rule.

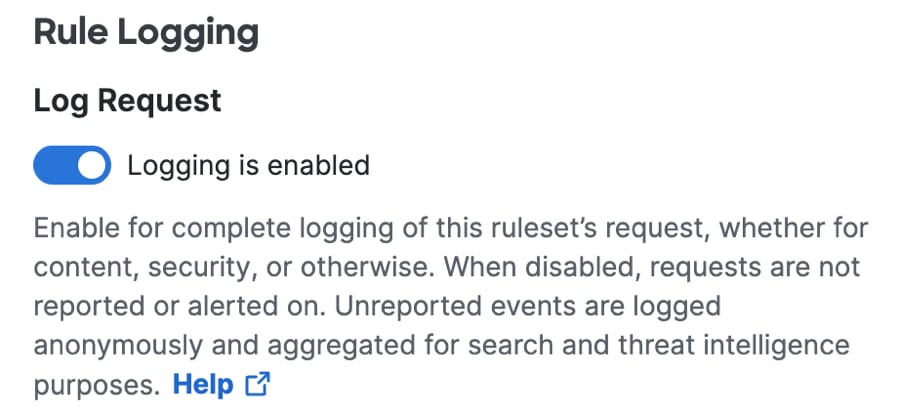
    1. For Log Request, toggle Logging is enabled off or on to choose whether Secure Access logs the events for the traffic managed by the access rule.

      The Log Request Setting interface.
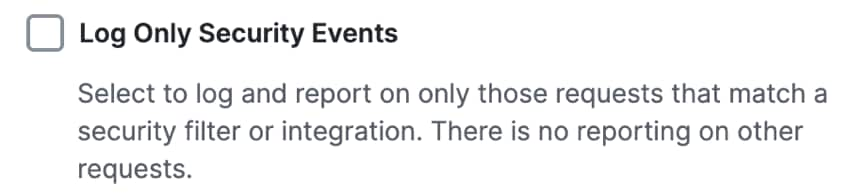
    2. For Log Only Security Events, select whether Secure Access logs the events that match the security filters.
      For more information, see Manage Logging.
      The Log Only Security Events interface.

Add a Rule Name

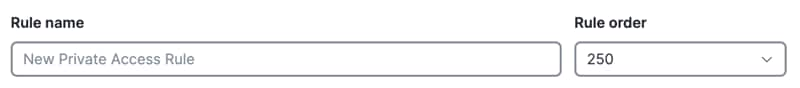
For Rule name, add a meaningful name for your access rule. The Rule name is required. You must give your rule a name before you can continue to configure the Security Controls on the access rule.

Note
The Next button on the access rule is not available until you enter a name for the rule.

The Private Rule Name Description interface.

Guidelines for Creating a Rule Name

Secure Access enforces the number and type of characters supported in a rule name. You can add a rule name with these constraints:

  • A rule name is a sequence of 2–50 alphanumeric, hyphen, underscore, and space characters.

  • A rule name must be unique across all access rules in the organization's Access policy.


Summary

After you add a rule to your policy, you can edit the rule and then view the rule summary.

  1. Navigate to Secure > Access Policy.

  2. Navigate to a rule, and then click on the horizontal ellipsis (...) to expand the rule menu.


    The Access Rule Small List interface.
  3. Click Edit to open the rule and view the rule summary.


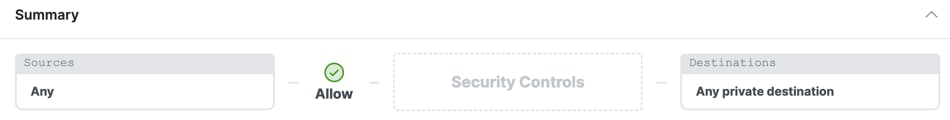
    The Private Access Rule Summary interface.

The summary contains the components that you configured on the access rule:

  • Sources

  • Action

  • Security Controls

  • Destinations

If you see an Upgrade button, this means that your organization has an opportunity to upgrade to a subscription that offers additional functionality. For more information, see Welcome to Cisco Secure Access.


Choose a Rule Order

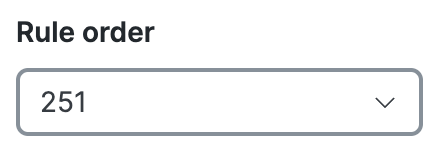
  1. For Rule order, choose a new priority for the rule, or keep the rule order assigned to the rule by Secure Access.

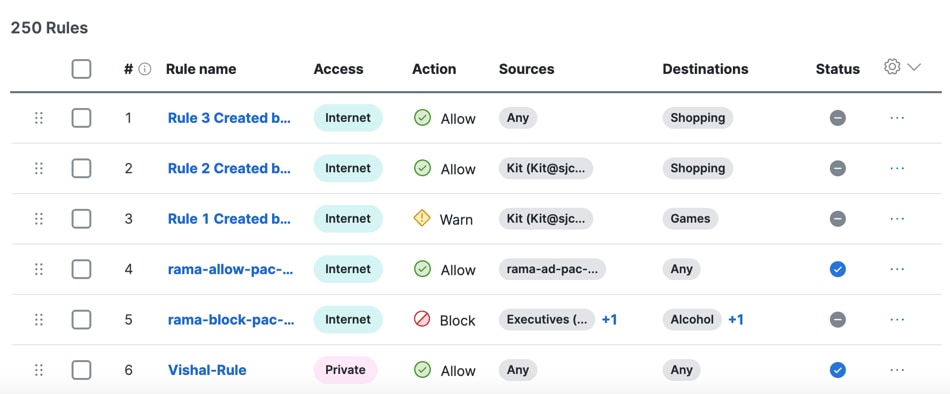
    When you add a new rule, Secure Access assigns the next lowest priority to the rule. Secure Access applies the first rule in the list on the Access Policy page that matches the traffic. Order your rules so that more specific rules that might apply to the traffic are above more general rules. For more information, see Edit the Order of Rules on the Access Policy Page.


    The Access Policy Rule Order Small interface.

Rule Action

  1. Choose Allow or Block to assign how Secure Access applies the configured components in the access rule.

    Note
    Secure Access blocks the traffic in your organization to private destinations unless an access rule allows the connections.
Note
When the action is Allow and the traffic does not pass the security controls defined in the rule, Secure Access blocks the traffic.

If you assign Block to a rule that is destine for a private application and there is an HTTPS “Get” request for a downloadable file, the rule blocks matching traffic and actions appropriately but the event appears in Activity Search twice: one entry as the action is “blocked” and one entry as the action is “allow”. Activity Search does not currently condense events that generate multiple entries and thusly increases the hit counter as “2”.


Enable a Schedule on a Private Access Rule

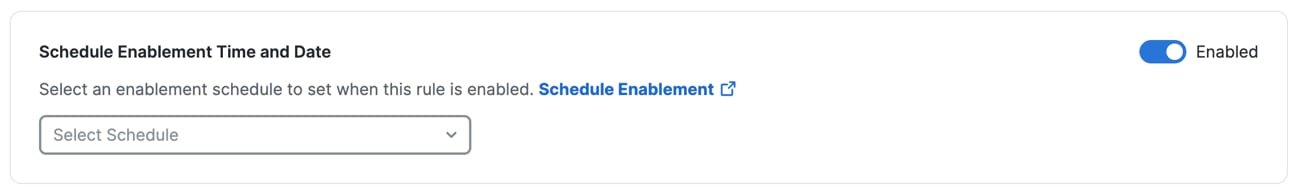
Configure the Schedule Enablement Time and Date setting and add a Schedule for the private access rule. For information about configuring Schedules in Secure Access, see Manage Schedules.

Before you begin

Procedure

  1. On a private access rule in the Access policy, navigate to Specify Access, and then navigate to Schedule Enablement Time and Date.


    The Schedule Enablement Selector interface.
  2. Click Enabled to activate a Schedule on the private access rule.

    1. (Optional) To disable a Schedule on the private access rule, toggle off the Schedule Enablement Time and Date setting.
  3. Click the Select Schedule drop-down menu and then choose a schedule to enable on the private access rule.

  4. Click Save.


Pre-Configured Sources

We recommend that you use your organization's reusable source components in your access rules. If you select Users or User Groups, you can choose destinations enabled for virtual private networks (VPNs) and Zero Trust Access connections, not Branch connections.

Note
The connection methods for a destination depend on the type of sources that you choose.
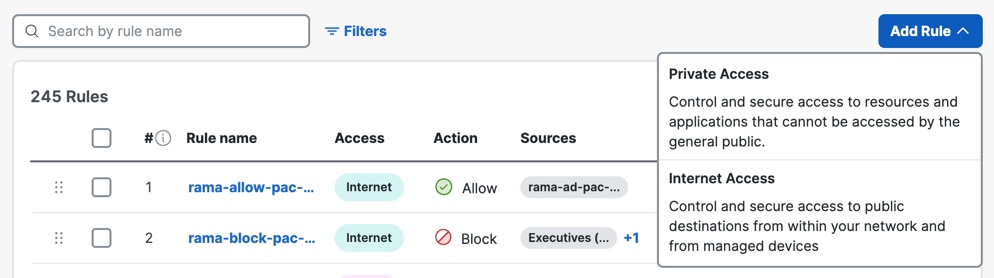
  1. Navigate to Secure > Access Policy > Add Rule > Private Access.

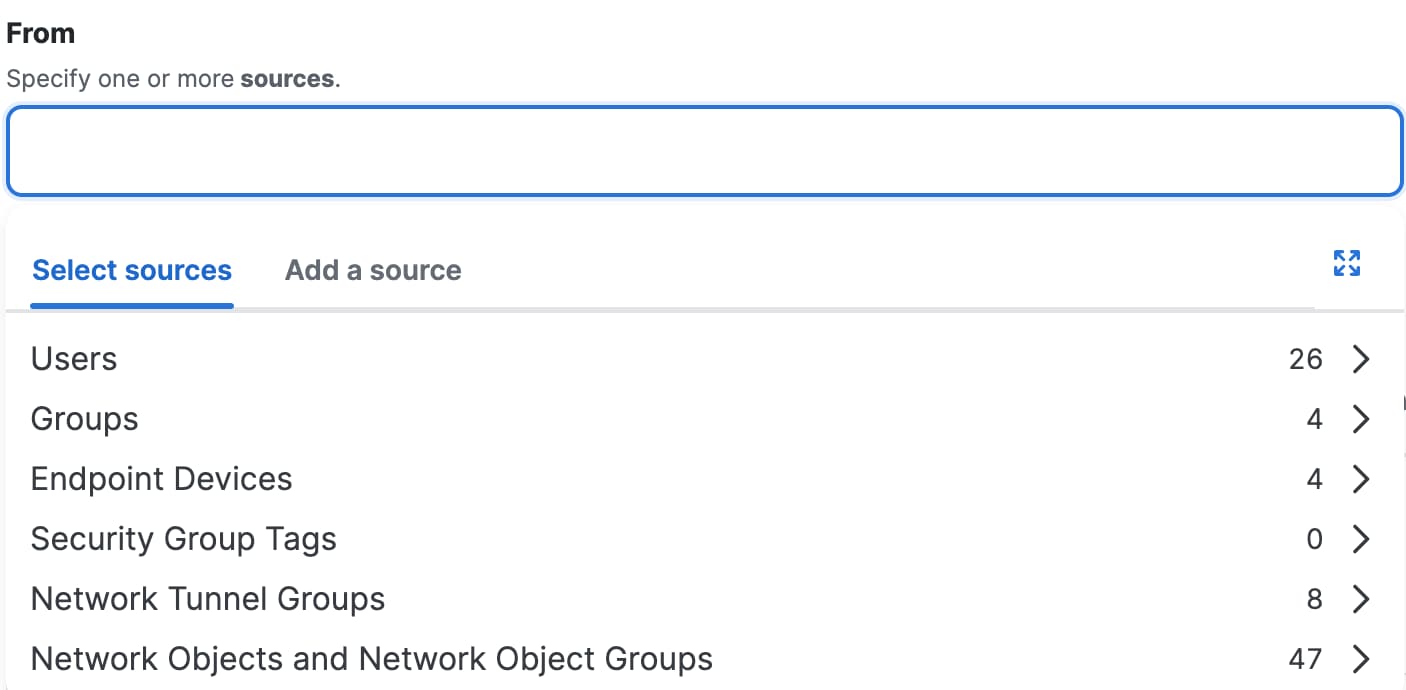
  2. Navigate to Specify Access and then click on the search bar under From.

  3. For Select sources, click in the white space beside the default value ("Any") and choose the configured source components in your organization. When you finish choosing your sources, click Done. For descriptions of the different types of sources, see Components for Private Access Rules: Sources.


    The Private Access Rule Source Components interface.
  4. After you add a source component, click +More to view the list of sources that you added to the rule.


    The Search Source Components 02 interface.

Add Composite Sources

Add a network address as a source on a private access rule.

The connection methods for a destination depend on the type of sources that you choose.

Procedure

  1. Navigate to Secure > Access Policy > Add Rule > Private Access.

  2. Navigate to Specify Access and then click on the search bar under From.

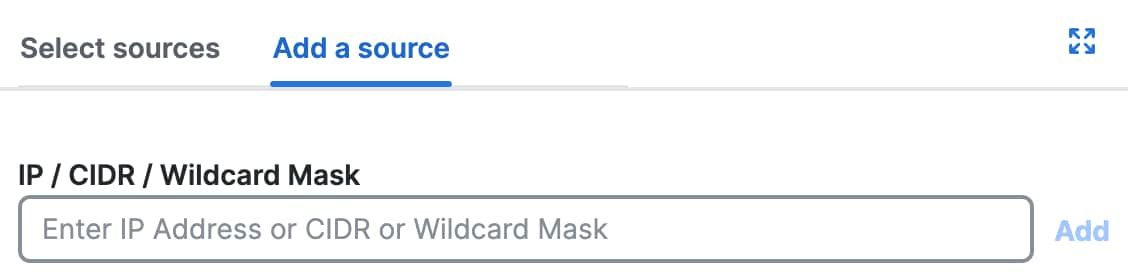
  3. For Add a source, enter an IPv4 address, CIDR block, or IPv4 address with a wildcard mask

    This option is useful if you need to quickly address a specific issue that arises, for example to immediately block a particular user's access to an internet destination. For more information, see About Configuring Sources in Private Access Rules.
    For Example:

    • IPv4 address—1.2.3.4

    • CIDR block—1.2.3.4/24

    • Wildcard mask—1.2.3.4/255.255.255.255

      For Wildcard Mask, use the format: <IP address>/<Wildcard Mask>.

    The Secure Access Wildcard Add Source Button interface.
  4. Click Add.

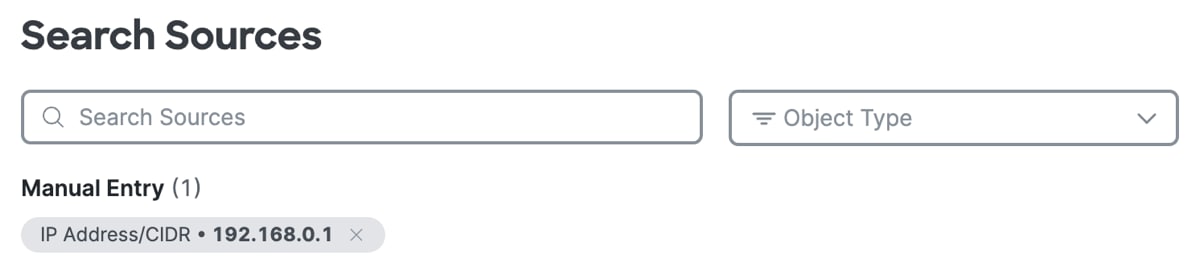
  5. After you add a composite source, click +More to view the list of sources that you added to the rule.

    The Search Composite Sources interface.

Pre-Configured Destinations

We recommend that you use your organization's configured destination components in your private access rules. For more information, see Reusable Destinations in Private Access Rules.
  1. Navigate to Secure > Access Policy > Add Rule > Private Access.

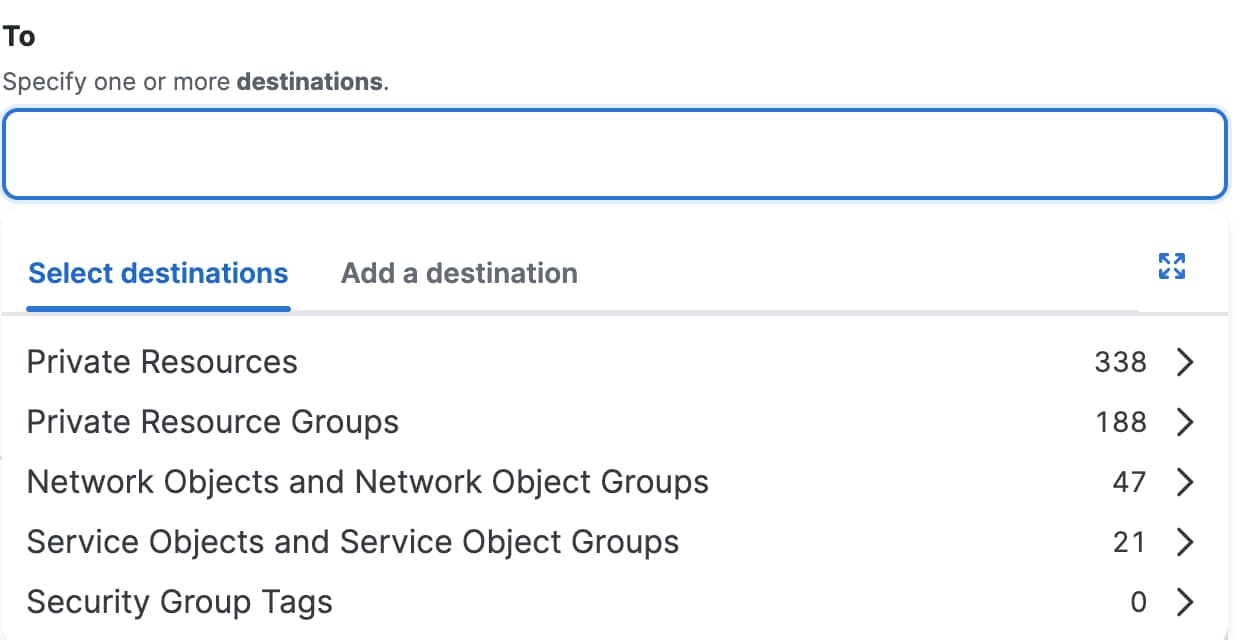
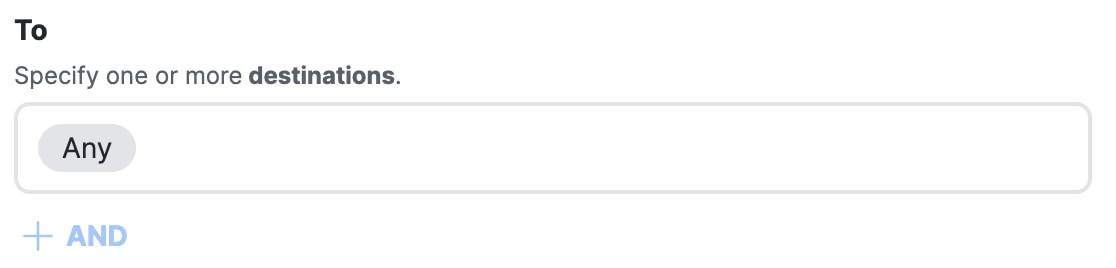
  2. Navigate to Specify Access and then click on the search bar under To.

  3. For Select destinations, click in the white space beside the default value ("Any") and choose the configured Private Resource Groups and Private Resources in your organization. When you finish choosing your private resources, click Done.

    Note
    The arrows out icon opens a window to configure the destinations in your rule.
    1. For each Private Resource, hover over the network connections icons.

      Secure Access describes the type of network connections supported by the private destination.

      The Private Access Rule Destination Components interface.
  4. After you add a destination component, click +More to view the list of destinations that you added to the rule.

    1. Click on the X to remove a previously added destination, then click Done.

      The Search Destination Components Private interface.

For more information, see About Configuring Destinations in Private Access Rules.

Add Composite Destinations

You can add destinations directly on a private access rule. For more information, see About Configuring Destinations in Private Access Rules.
  1. Navigate to Secure > Access Policy > Add Rule > Private Access.

  2. Navigate to Specify Access and then click on the search bar under To.

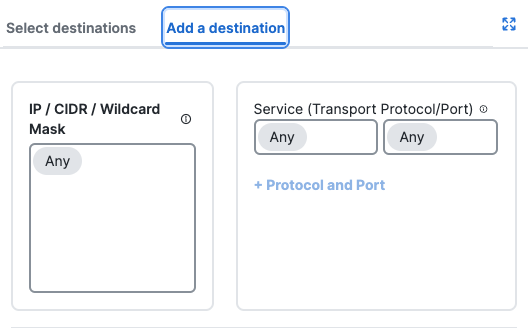
  3. For Add a destination, enter or select the network components, then click Add.

    The Screenshot 2024 11 15 at 2 47 41 PM interface.
    1. For IP, CIDR, or Wildcard Mask, enter an IPv4 or IPv6 address, CIDR block, or IPv4 address with a wildcard mask.

      For example:

      • IPv4 address—1.2.3.4

      • IPv6 address—2001:DB8::/32

      • CIDR block—1.2.3.4/24

      • Wildcard mask—1.2.3.4/255.255.255.255

      For Wildcard Mask, use the format: <IP address>/<Wildcard Mask>.

    2. For Protocol, choose from one of the supported protocols: ANY, TCP, UDP, or ICMP.

    3. For Port/Port Range, enter a port or range of ports.

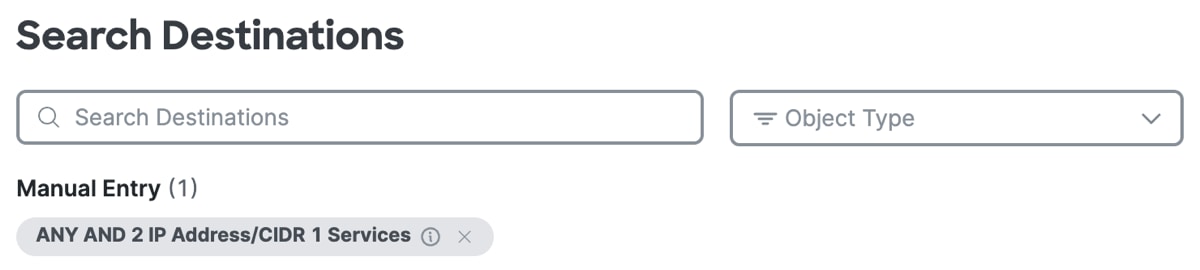
  4. After you add a composite destination, click +More to view the list of destinations that you added to the rule.

    1. Click on the X to remove a previously added destination, then click Done.

      The Search Destination Composite interface.

      To allow VPN access to a private resource, specify its IP, CIDR, or Wildcard mask, port, or protocol with the Add a destination option.

      Note
      You might use this option to allow users from one branch to access private applications in another branch. Destinations that you enter manually are not reusable in another access rule.

      For more information, see About Configuring Destinations in Private Access Rules.

Select Network and Service Objects on Private Access Rules

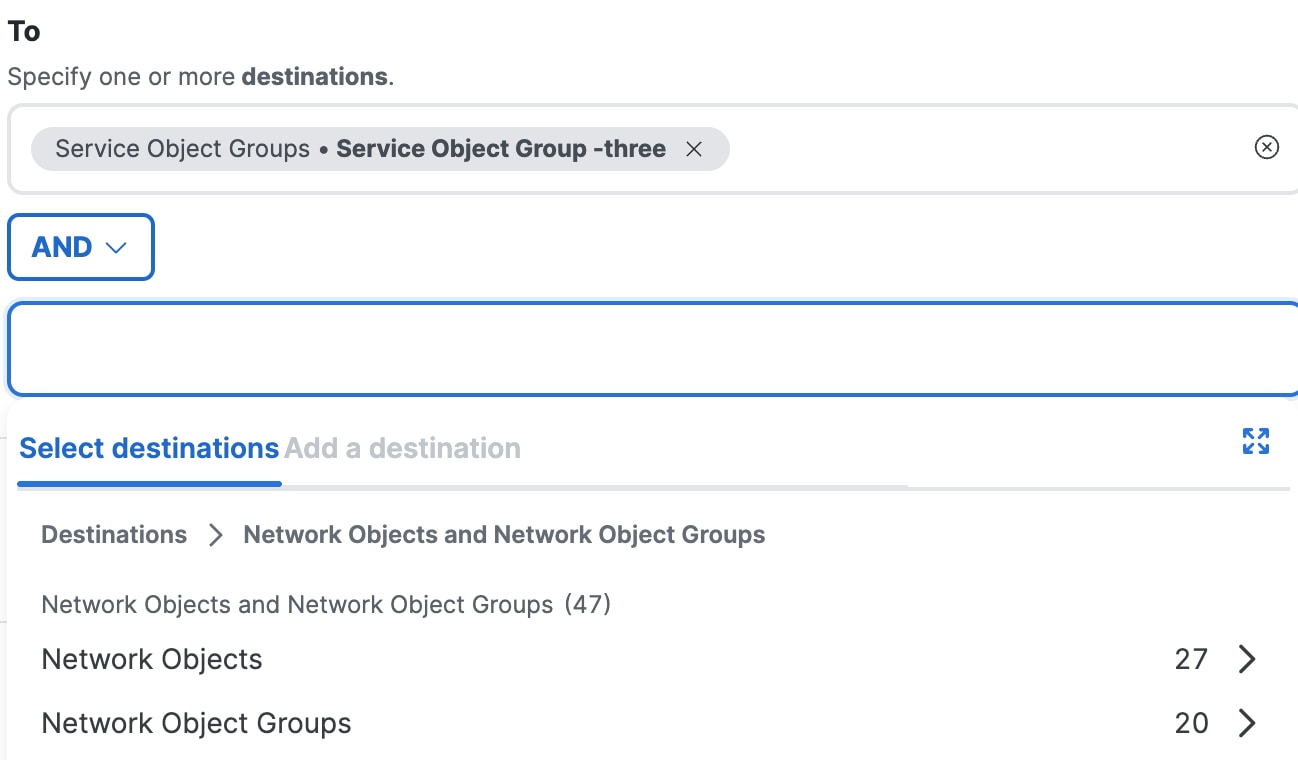
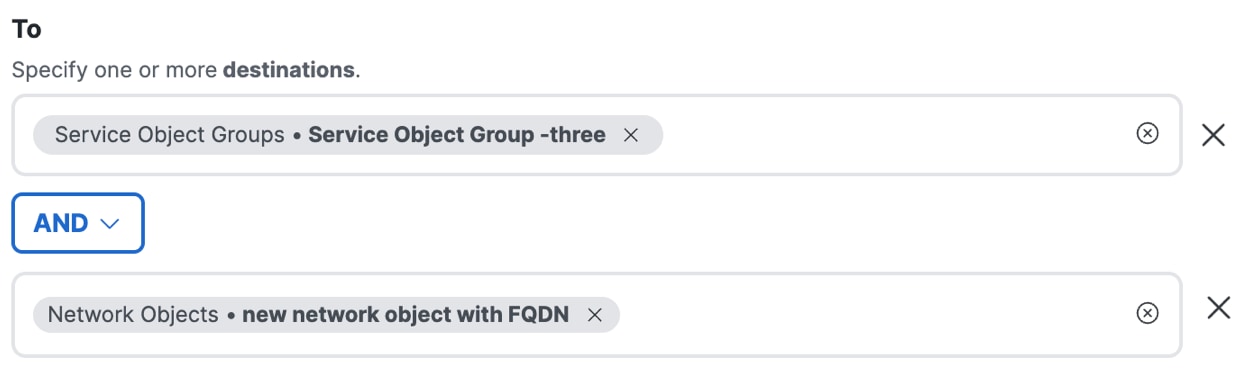
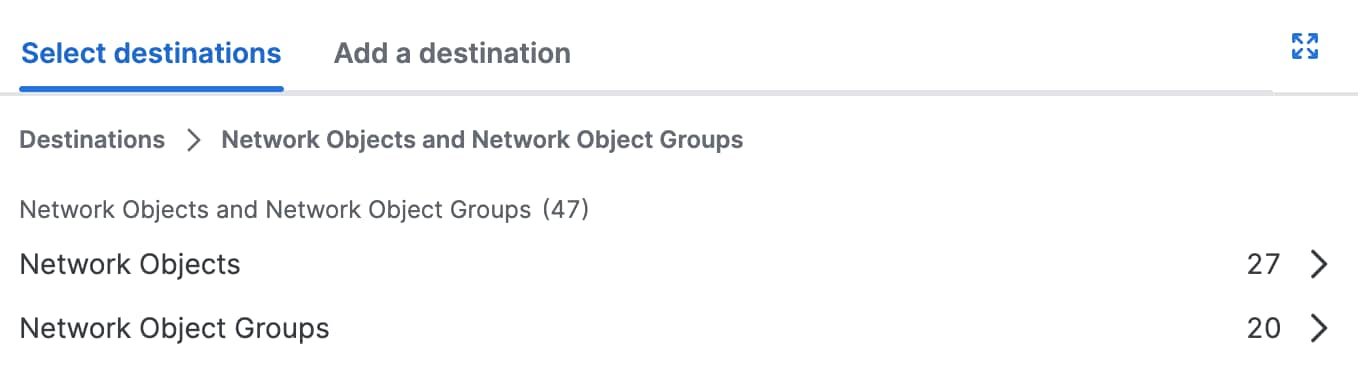
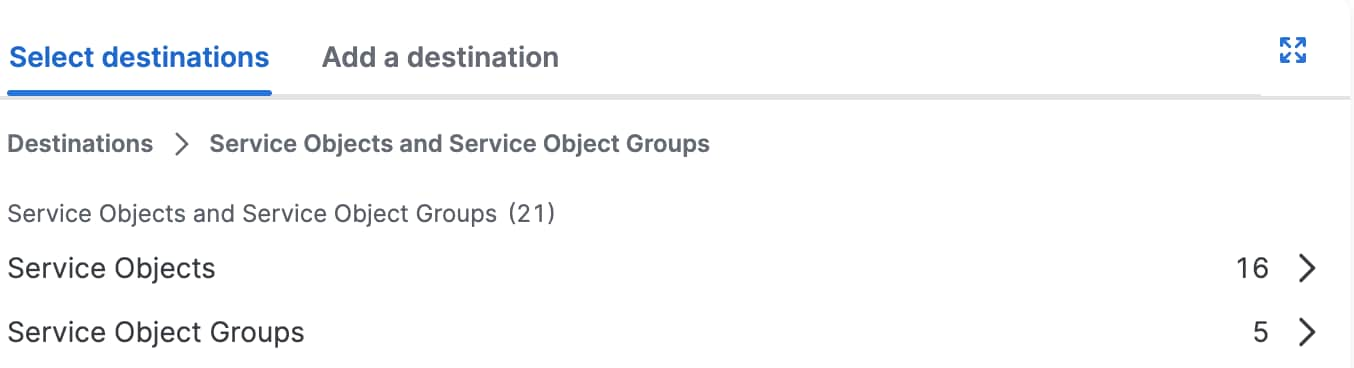
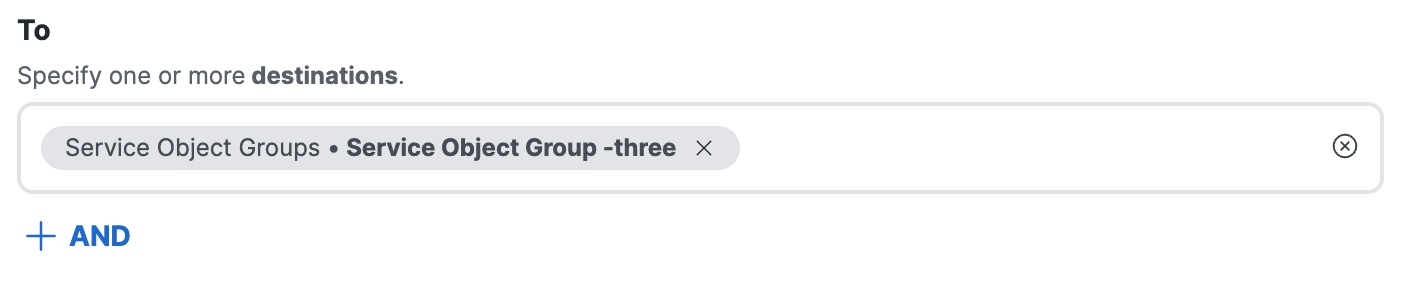
You can select pre-configured Network Objects and Groups and Service Objects and Groups as destinations on private access rules. When you choose the objects and groups, you have the option to combine the objects and groups with the logical AND operator. For more information, see Combine Destinations with Boolean Logic.

Note
If you do not add the logical AND operator with the selected destinations, Secure Access combines the destinations with the logical OR operator. For more information, see Combining Multiple Destinations in a Rule (Boolean Logic).

Before you begin

Procedure

  1. Navigate to Secure > Access Policy > Add Rule > Private Access.

  2. Navigate to Specify Access and then click on the search bar under To.

    The Internet Rule to with and interface.
  3. Select the Network Objects and Groups or Service Objects and Groups.

    1. Click Select destinations, and then choose the Network Objects and Groups to add to the internet rule.
      The Internet Access Rule Destination Nog interface.
    2. Click Select destinations, and then choose the Service Objects and Groups to add to the internet rule.
      The Internet Access Rule Destination Sog interface.
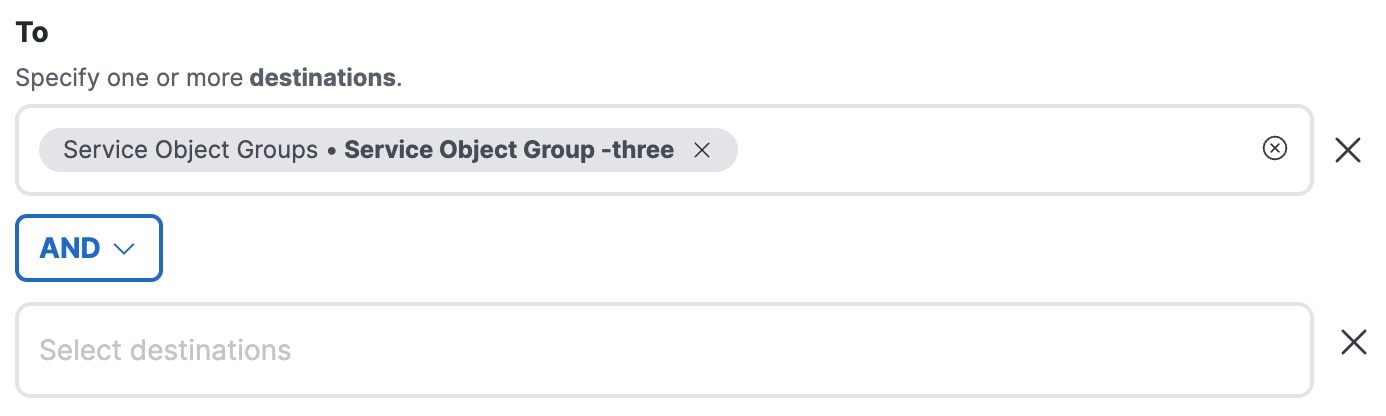
  4. (Optional) Click +AND.

    The Internet Access Rule Destination Select and interface.
    1. Click on the Select destinations text area.
      The Internet Access Rule Destination with and interface.
    2. Choose a destination to combine with the other selected destinations using the logical AND operator.
      For more information, see Combine Destinations With Boolean Logic. The Internet Access Rule Destination and Full interface.

      After you select the objects and groups to use with the AND operator, you can remove the destinations and then add new destinations.

      Note
      You have to select all destinations at the same time for each side of the AND option. Once selected, you can not go back and add more destinations.
      The Internet Access Rule Destination and Both Sides interface.
  5. Click Next.


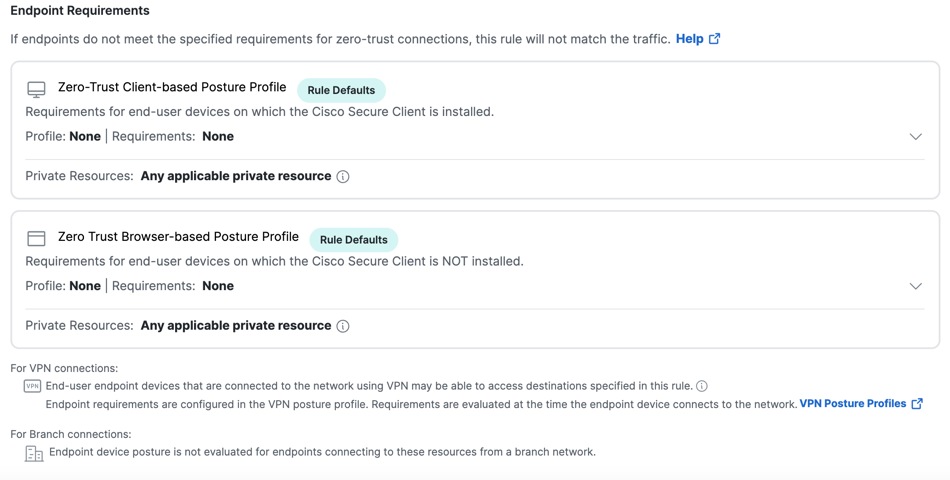
Endpoint Requirements


User Authentication Requirements

For Zero Trust Access: User Authentication Interval, toggle on or off whether Secure Access prompts users to authenticate before connecting to private destinations. When Zero Trust Access: User Authentication Interval is enabled, you can set the interval when Secure Access requests that you authenticate.

This setting determines how often users must sign in to the network in order to make a Zero Trust connection to a private resource specified as a destination in this rule. Users are prompted to sign in only once per interval if they try to connect to a resource during that time, regardless of the private resources they access.

This option appears only if destinations include at least one private resource.

In access rules that apply to iOS devices, User Authentication Interval must be disabled or iOS device users will be unable to access resources that are enabled for zero trust access.

You can use the default interval as configured on the Rule Defaults page or specify a different interval.

For more information, see Network Authentication for Zero Trust Access.


Configure Security Control Options

Security control options for traffic to private destinations include the following:

Intrusion Prevention (IPS)

  1. Use the default IPS profile as specified on the Rule Defaults page, or choose a different IPS profile that includes the threat detection settings that you want applied to traffic that matches this rule.

  2. Click Save.

We recommend that you do not disable your IPS Profiles. For more information, see Manage IPS Profiles.

Security Profile

The security profile for private access specifies file inspection and file type controls for uploaded and downloaded files in private traffic.

Use the default security profile for private access as specified on the Rule Defaults page, or choose a different security profile to apply to traffic that matches this rule.

For details, see Security Profiles for Private Access.