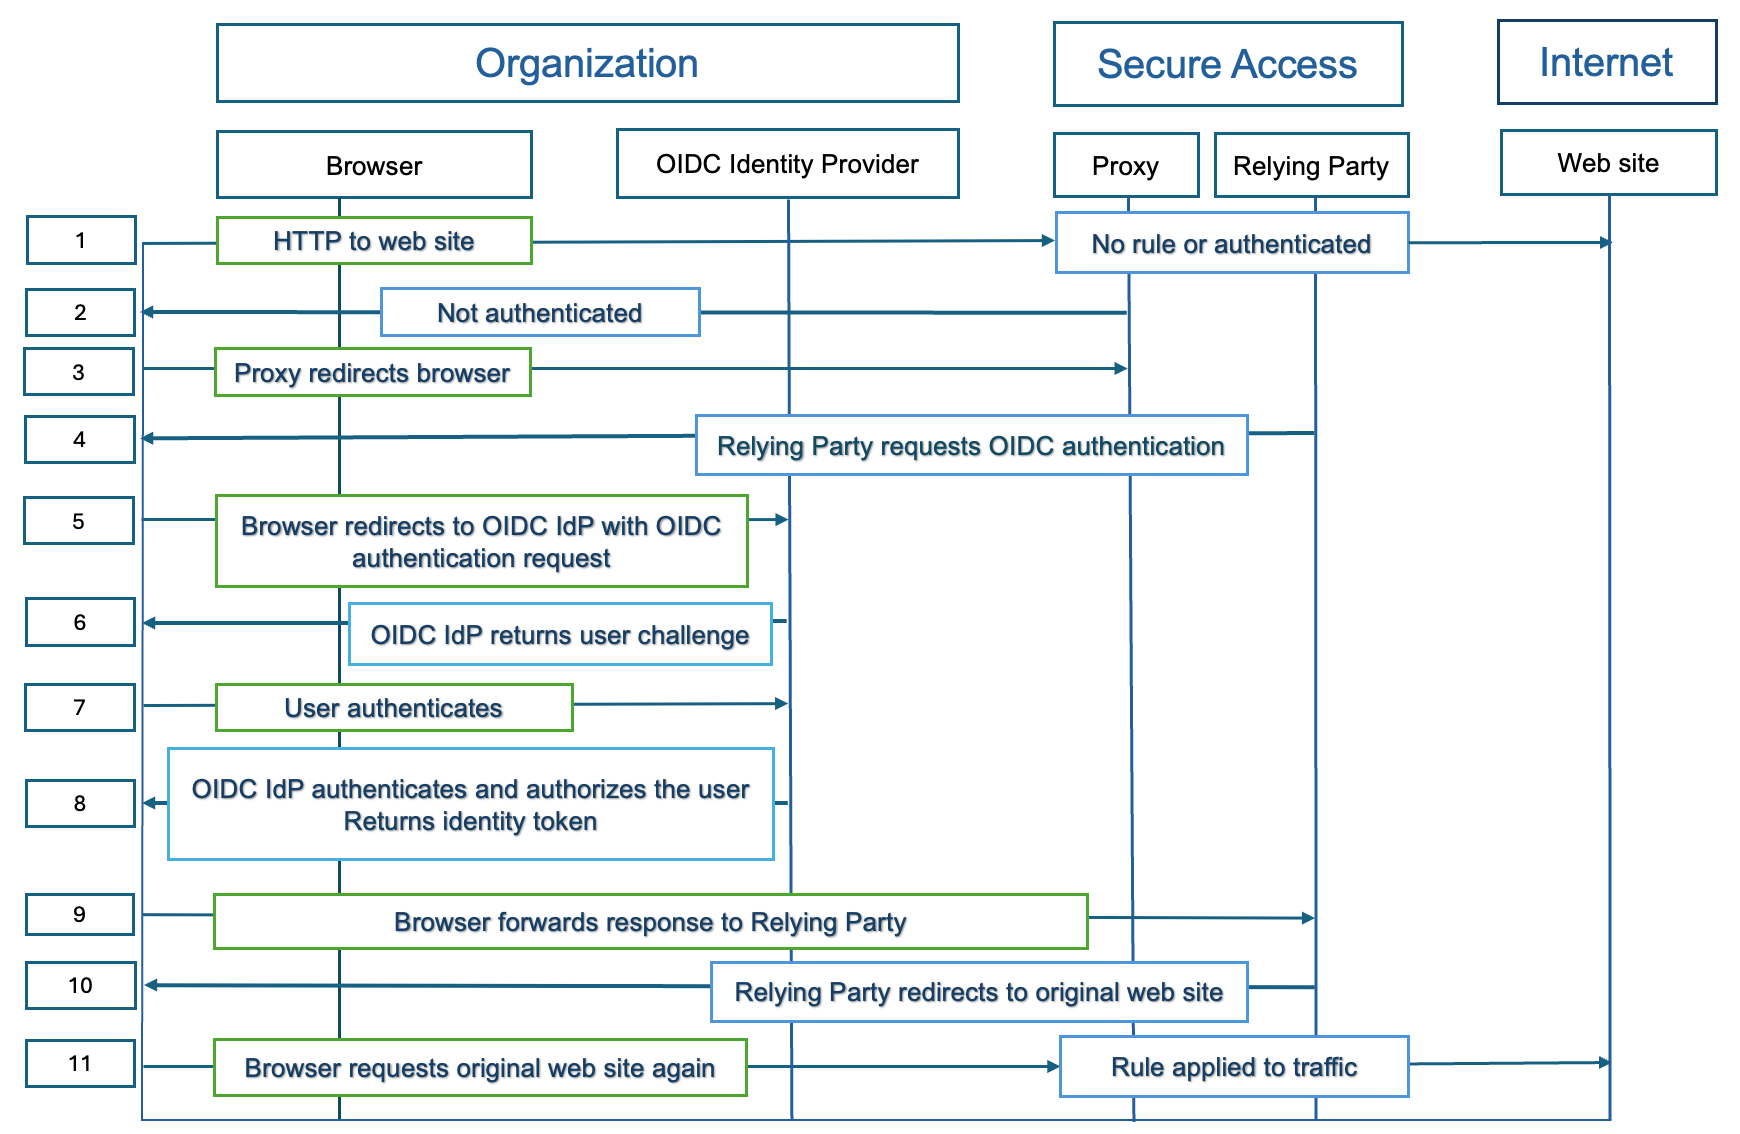
Describes Configure Integrations with OIDC Identity Providers in Cisco Secure Access. Cisco Secure Access enables you to connect securely to the internet, web destinations in private and public clouds, your organization's on-premises private resources, and Software as a Service (SaaS) applications.
Cisco Secure Access enables you to connect securely to the internet, web destinations in private and public clouds, your organization's on-premises private resources, and Software as a Service (SaaS) applications. To create more granular access rules and to authenticate users connecting on networks or network tunnels or with Zero Trust Access (ZTA), you can integrate an OpenID Connect (OIDC) identity provider (IdP) with Secure Access.
Secure Access supports OIDC for single sign-on (SSO) authentication of users through the integration with Okta and Microsoft Entra ID.
Once users in your organization are configured to use SSO through an IdP, the IdP manages all authentication requests. A user authenticates to the SSO authentication IdP, automatically signs in to Secure Access, and is authorized to connect to the requested destination.
Configure Identity Providers for OIDC Authentication
Follow the procedure in the configuration guides to integrate an SSO authentication IdP for Open ID Connect with Secure Access.
Secure Access Redirect URI
The Secure Access Redirect URI is used when you set up the integration of Secure Access for OIDC in the SSO authentication IdP app.
https://fg.id.sse.cisco.com/gw/auth/oidc/callback