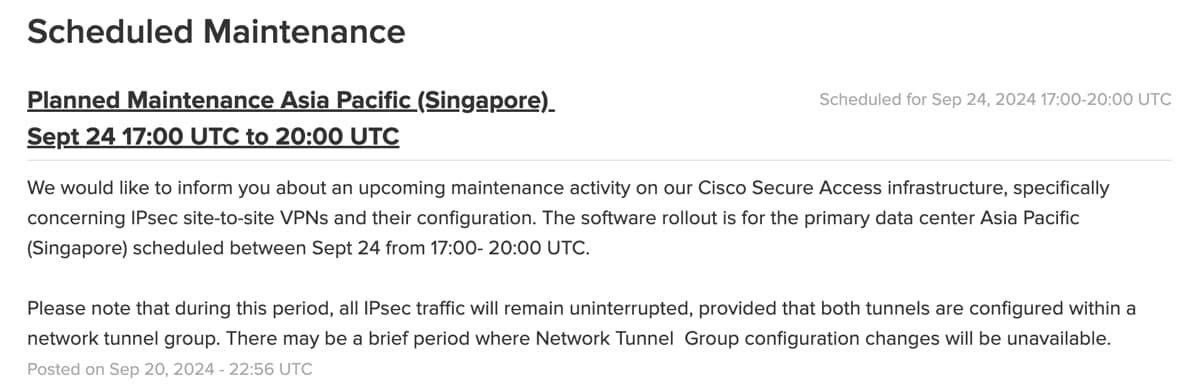
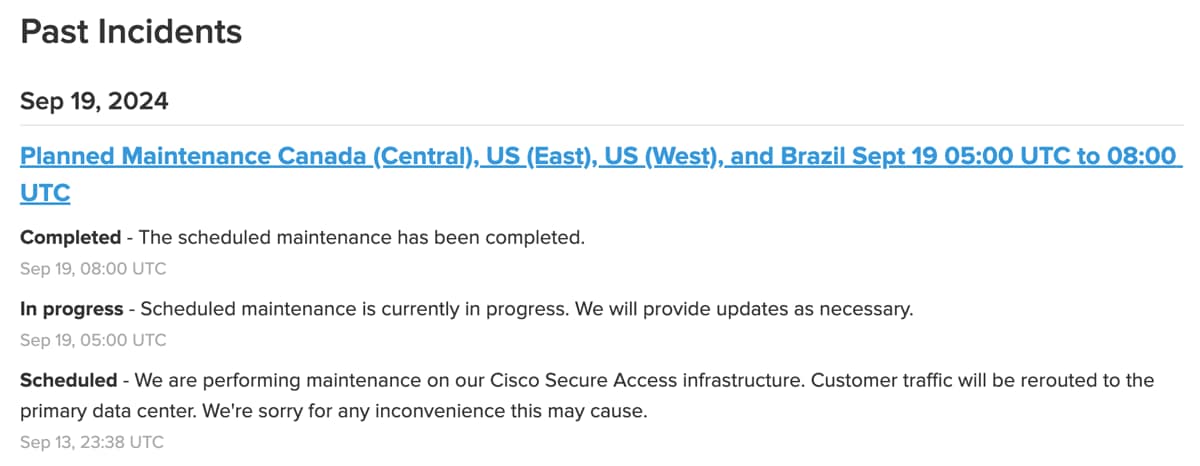
The Cloud Security Platform section on the Cisco Secure Access Service Status page provides visibility into the operational status of Secure Access services from both a global and a region-specific perspective. Administrators use this information to understand the scope of service-impacting events and to determine whether observed behavior affects all users or only users in specific locations.
Global Status
The Global view displays the status of Secure Access services aggregated across all regions. Expand Global to view the list of Secure Access services and their current operational state based on active incidents or maintenance events.
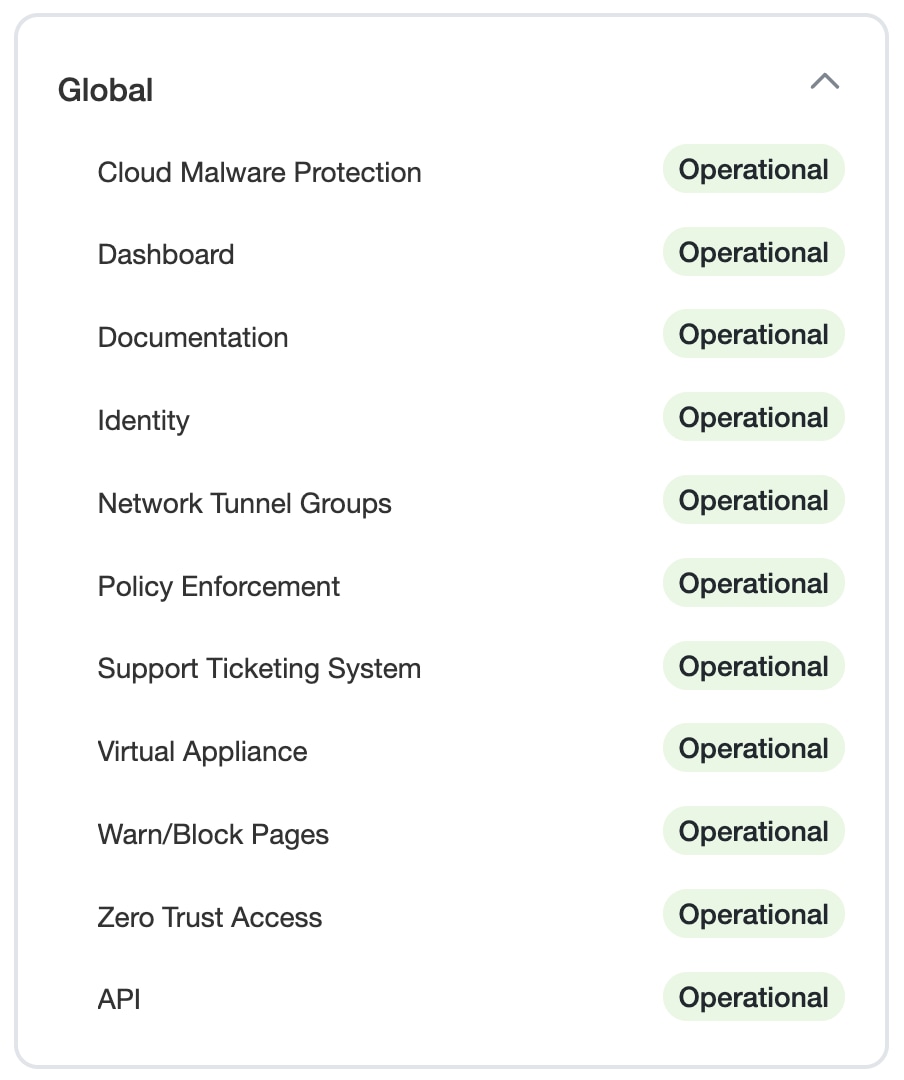
Administrators should use the Global view to determine whether a service condition is widespread and potentially affecting users across multiple regions.
Region-Specific Status
The region-specific view displays the status of Secure Access services for a specific geographic region. Expand a region to view the list of services and their current operational state for that region.
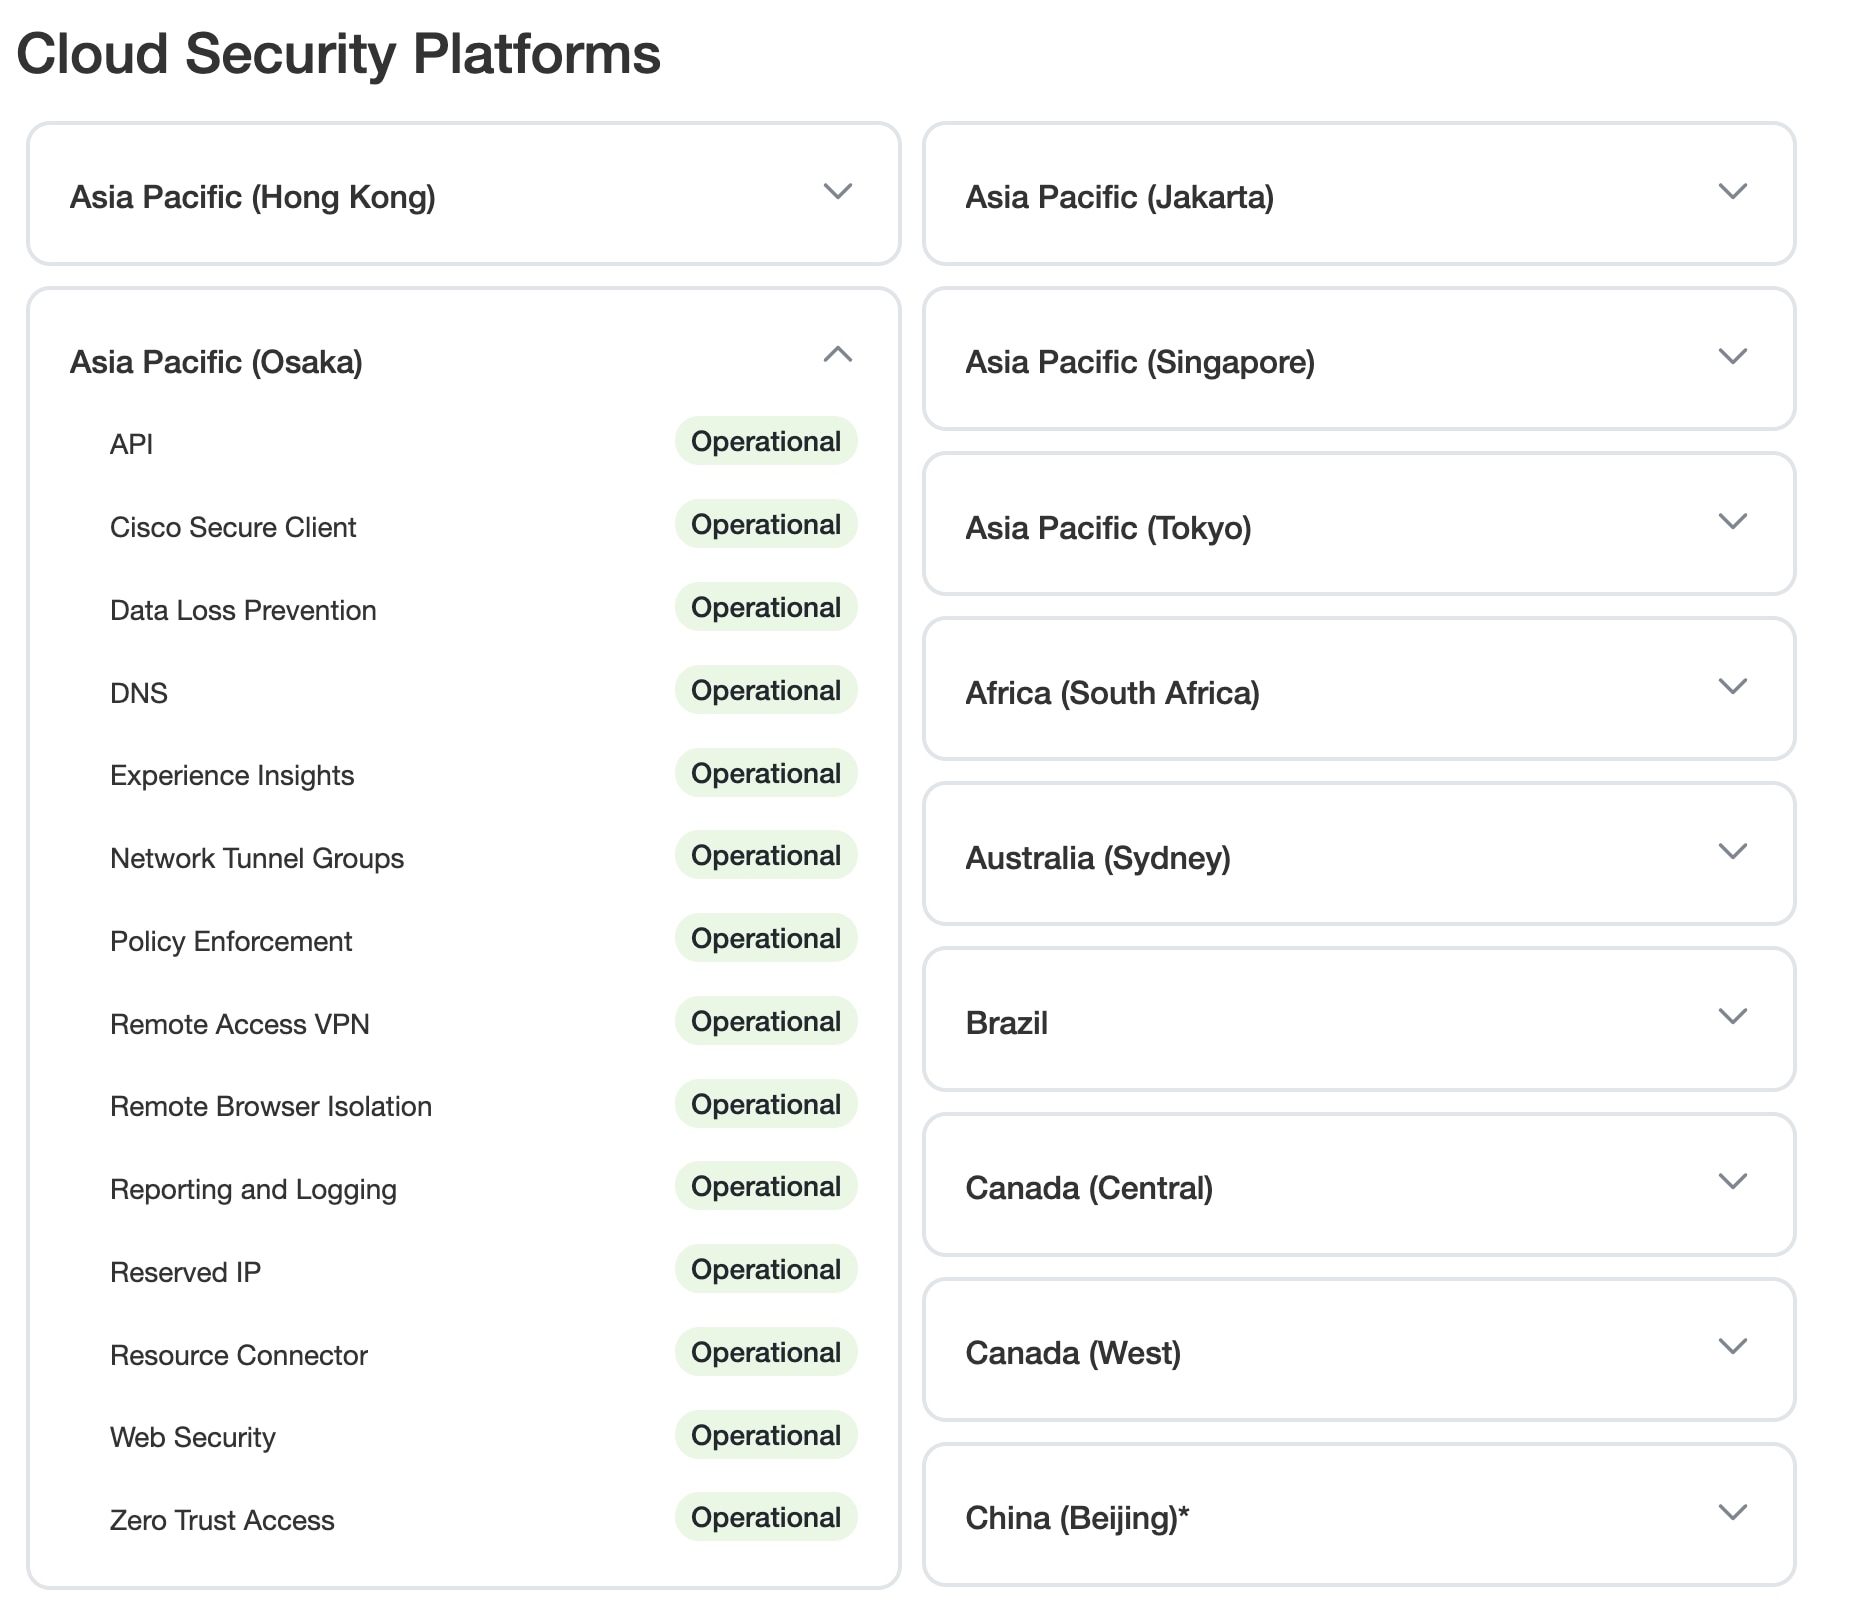
Administrators should use the region-specific view to identify localized service impact, especially when user issues are limited to a specific region or access location.
Service Status Definitions
The Cloud Security Service Status describes the state of a service component using one of the following statuses. These definitions apply to both Global and region-specific service status views.
- Operational—The service is available and functioning as expected.
- Under Maintenance—Scheduled or ongoing maintenance is being performed. During maintenance, traffic is automatically redirected to the closest available data center to ensure continued service availability. No user action is required.
- Degradation—The service remains online, but users may experience reduced performance or partial impact.
- Outage—A data center is unreachable. To maintain service continuity, traffic to Cloud Security services is automatically routed using Anycast.
Secure Access Service Descriptions
The Cloud Security Platform section lists Secure Access services whose operational status is displayed at both the Global and Region-specific levels. The following descriptions help administrators understand the functional scope of each service when interpreting service status information.
- API—Platform API services that support programmatic access, automation, integrations, and administrative operations within Cisco Secure Access.
- Cisco Secure Client—Services that support Secure Access client connectivity, including client-based access to internet, SaaS, and private applications.
- Cloud Malware Protection— Detects and removes malware from cloud-based file storage applications. It enriches security protection by scanning files automatically and flagging malicious content for remediation, supporting services such as Box, Dropbox, Webex, Microsoft 365, Google Drive, AWS S3, and Azure.
- Dashboard—Provides visibility in reports and applied policies down to the user level by leveraging Cisco Secure Client, Virtual Appliances, and third-party integrations.
- Data Loss Prevention—Services that inspect traffic to detect and prevent the exposure of sensitive data based on configured data protection policies.
- DNS—Secure DNS resolution and enforcement services used to apply security policies, control domain access, and route user traffic.
- Documentation—Provides access to user guides and API programming guides for Secure Access services.
- Experience Insights—Services that collect and analyze user experience and performance data to provide visibility into connectivity quality and service behavior.
- Identity—Integrates identity trust levels into Secure Access, enabling adaptive access policies based on live identity data and user trust profiles.
- Network Tunnel Groups—Services that manage network tunnel groups used for establishing and maintaining secure tunnels between customer networks and Cisco Secure Access.
- Policy Enforcement—Core enforcement services responsible for applying security and access policies across Secure Access traffic flows.
- Remote Access VPN—Services that provide secure remote connectivity for users accessing internet, SaaS, and private resources through Cisco Secure Access.
- Remote Browser Isolation—Services that isolate web browsing sessions in a remote environment to protect users from web-based threats.
- Reporting and Logging—Services that generate, store, and provide access to logs and reports related to Secure Access traffic, security events, and system activity.
- Reserved IP—Services that manage reserved public IP addresses used for consistent source IP presentation for Secure Access traffic.
- Resource Connector—Services that manage Resource Connector Groups and individual Resource Connectors used to provide access to private resources.
- Support Ticket System —Provides technical support access, case management, and assistance for Secure Access software and services.
- Virtual Appliance—Services related to the deployment, management, and operation of virtual appliances that support Secure Access functionalities.
- Warn/Block Pages—Services that display warning or block pages to users when access to certain resources is restricted or blocked based on security policies.
- Web Security—Secure web gateway services that inspect and enforce security policies on web traffic accessed through Cisco Secure Access.
- Zero Trust Access—Zero Trust Access services that control user access to private applications based on identity, device posture, and policy.