Cisco Secure Access Help

PDF

Cisco Secure Access Help

Cloud Malware Report

Want to summarize with AI?

Log in

Describes Cloud Malware Report in Cisco Secure Access. The Cloud Malware report provides an overview of malicious files within your environment and details the potential risk and exposure these files present.


The Cloud Malware report provides an overview of malicious files within your environment and details the potential risk and exposure these files present. For instructions to initiate malware scanning, see Enable Cloud Malware Protection.

To use the Cloud Malware report, you need a minimum user role of Read-only. For more information, see Accounts Overview.

To find the Cloud Malware report, navigate to Monitor > Reports > Cloud Malware.


View the Cloud Malware Report

Procedure

  1. Navigate to Monitor > Reports > Cloud Malware.


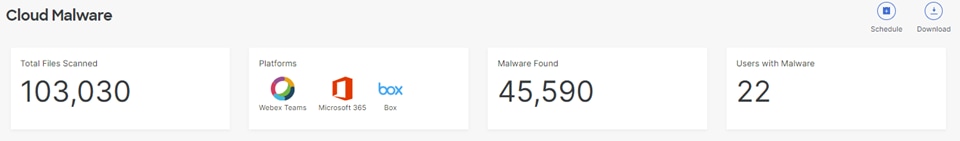
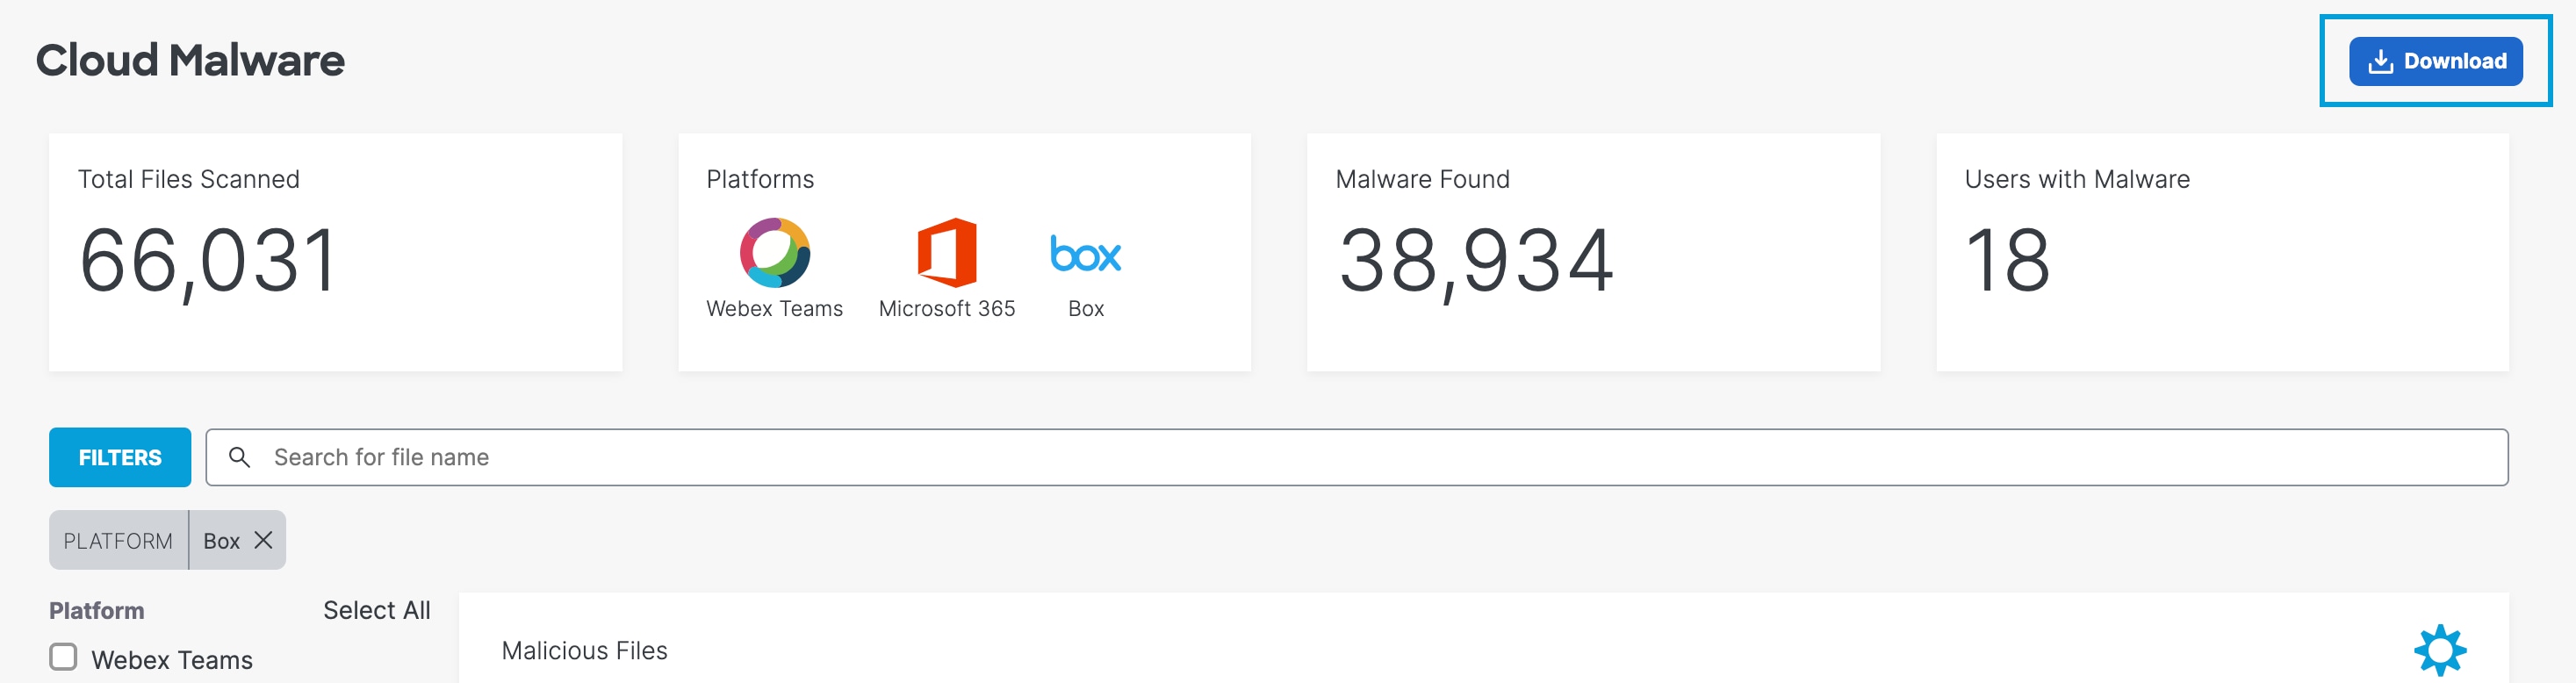
    The Cloud Malware Report interface.
  2. View the report's overview of information about the malicious files in your organization.

    • Total files scanned —The total number of files in the organization scanned for potential malware. This will also show a status as to whether the scan is complete or in progress.

    • Platforms—The platforms where malicious files were found.

    • Malware found—The total number of files found deemed malicious.

    • Users with malware—The number of users in your environment whose files contain malware.

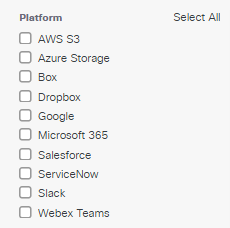
  3. Filter by platform.

    The platforms available for Cloud Malware are AWS S3, Azure Storage, Box, Dropbox, Google, Microsoft 365, Salesforce, ServiceNow, Slack, and Webex Teams. You can filter your malicious files' results by selecting any or all of the platforms listed.

    Note
    Secure Access supports Cloud Malware protection for Salesforce files and files attached to chatter posts, not for sObjects or for chatter posts.
    The Cloud Malware Report Platform Filter interface.
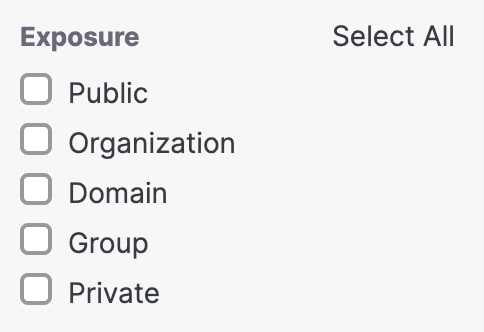
  4. Filter by exposure. You can filter your malicious files by the type of exposure they pose to the environment. By default, none are selected, so all exposure types are presented.


    Filter by exposure. You can filter your malicious files by the type of exposure they pose to the environment. By default, none are selected, so all exposure types are presented.
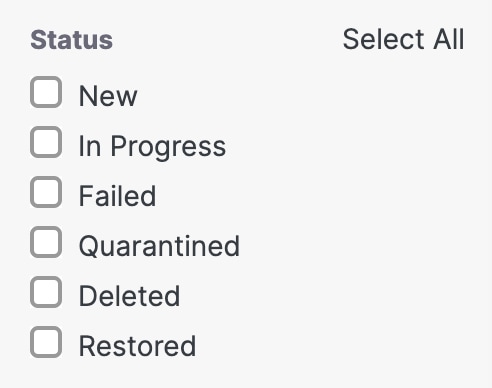
  5. Filter by status. Each file displays a status depending on whether it is newly discovered, a quarantine is in progress or failed, or that the file was successfully quarantined or deleted.


    Status. Each file displays a status depending on whether it is newly discovered, a quarantine is in progress or failed, or that the file was successfully quarantined or deleted.
  6. Optionally, you can choose to view suspect Potential Unwanted Applications.


    The View Options interface.
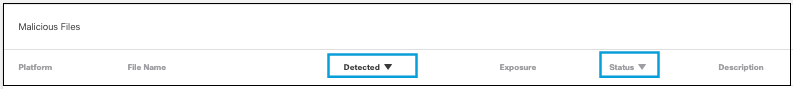
  7. Sort columns by detection or status.


    The Column Sort interface.

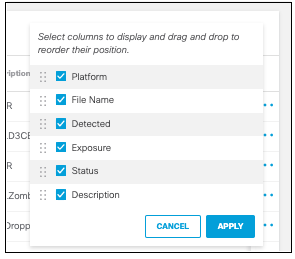
    Click the settings menu icon to select which columns to display and organize them as you choose.


    The Column Display interface.

Use the Cloud Malware Report


View Detailed Information About a File

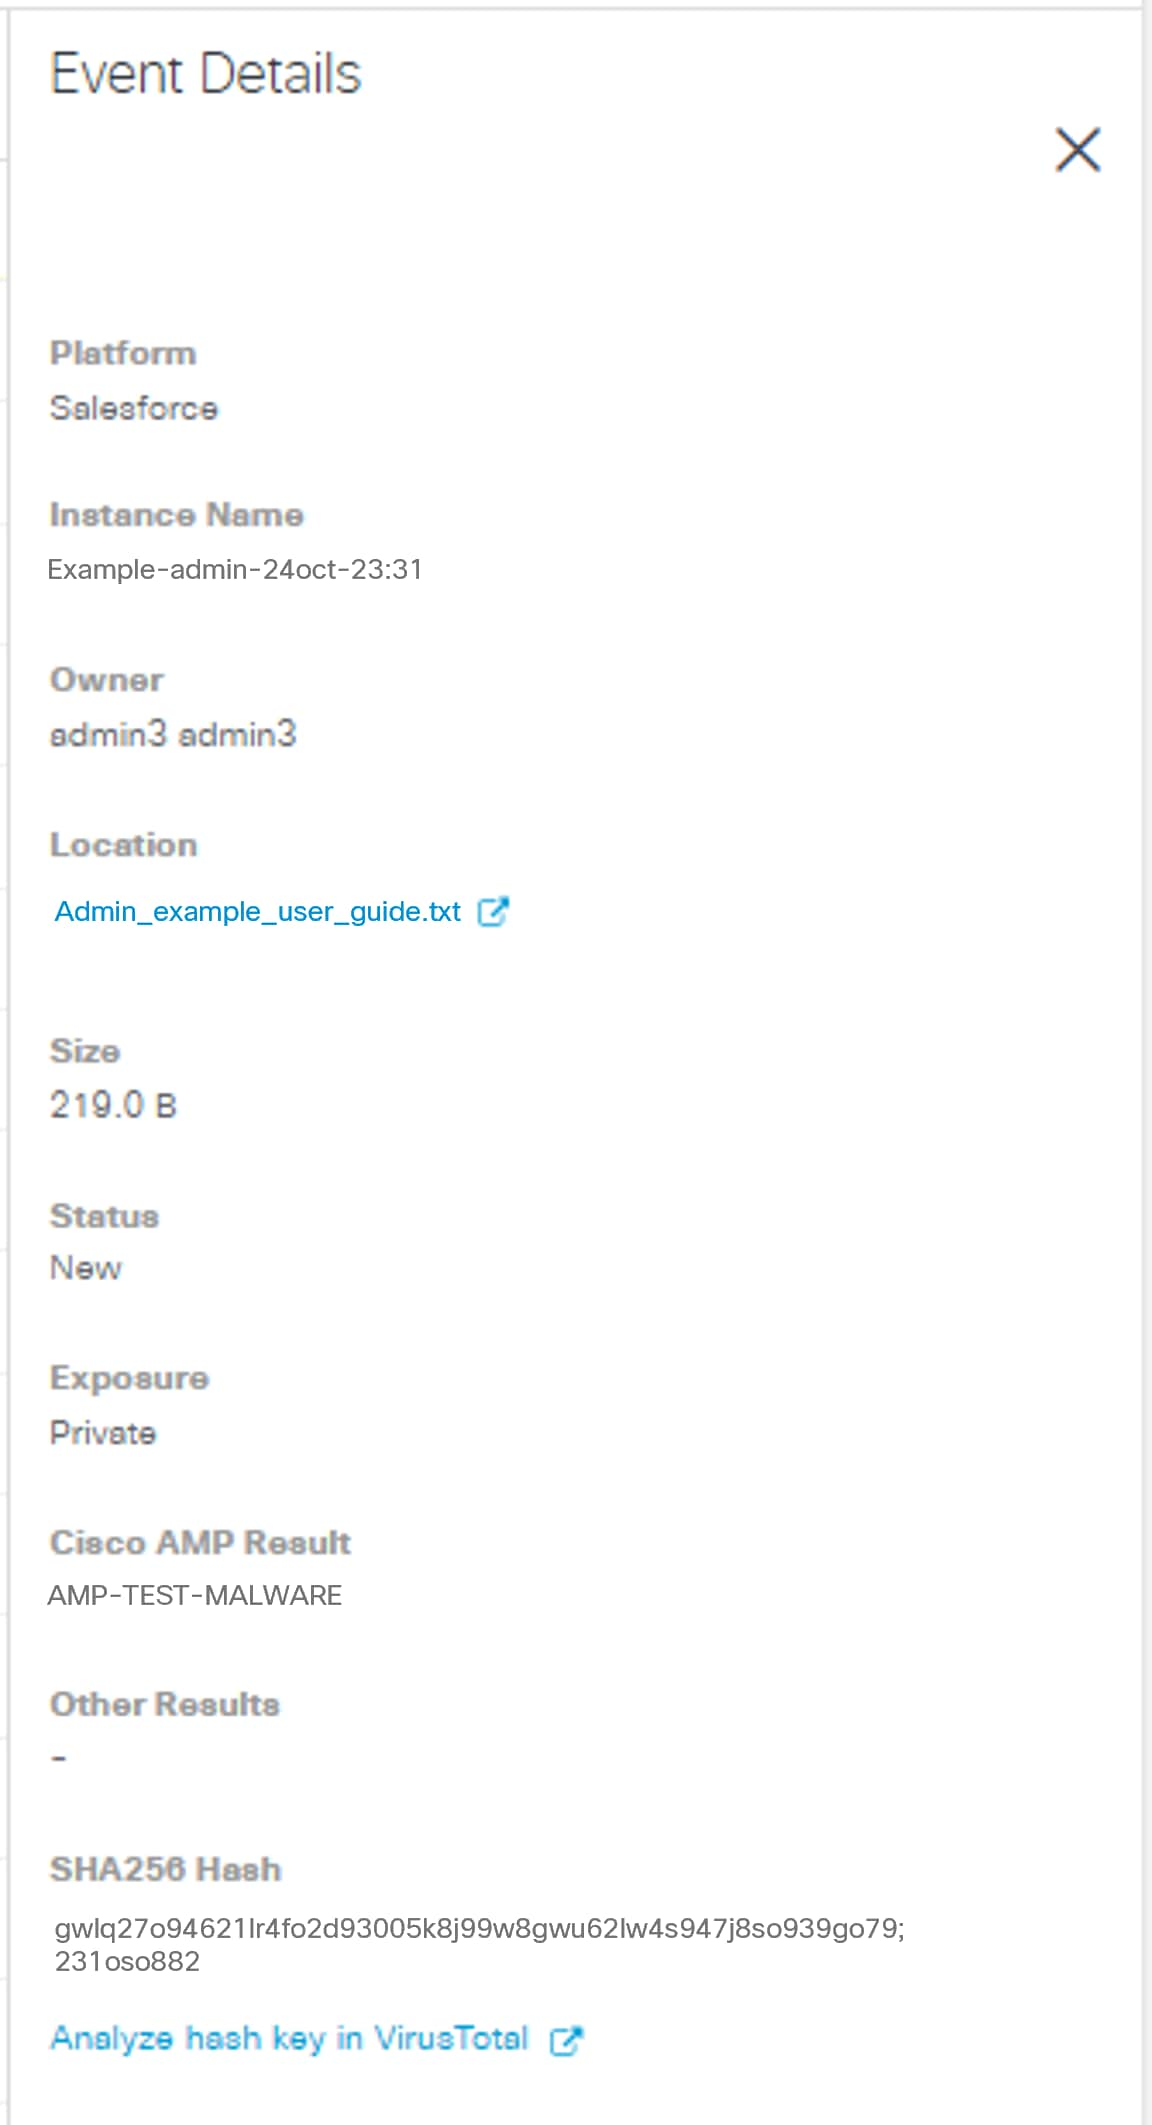
You can use the Cloud Malware Report to view details (such as owner, location, and size) about malicious files within your environment.

Before you begin

Procedure

  1. Navigate to Monitor > Reports > Cloud Malware.

  2. Review the list of files and identify a file of interest.

  3. Click the action menu (3 dots) to the right of the file of interest, then select See Full Details.

  4. Review the information that appears.

    The Malware Report File Details interface.

Quarantine a Malicious File

On the Microsoft OneDrive, Microsoft Teams, SharePoint Online, Box, Dropbox, Salesforce, ServiceNow, or Google Drive, when a malicious file presents a potential risk and needs remediation, you can manually quarantine the file. Only the integration user for the platform will have access to the quarantined files.

Before you begin

A minimum user role of Read-only. For more information, see Manage Accounts.

Procedure

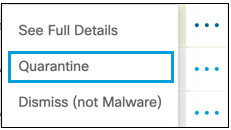
  1. Click the Action Menu to the right of the file that needs to be quarantined, then select Quarantine.


    The F9a107c Malware Quarantine interface.
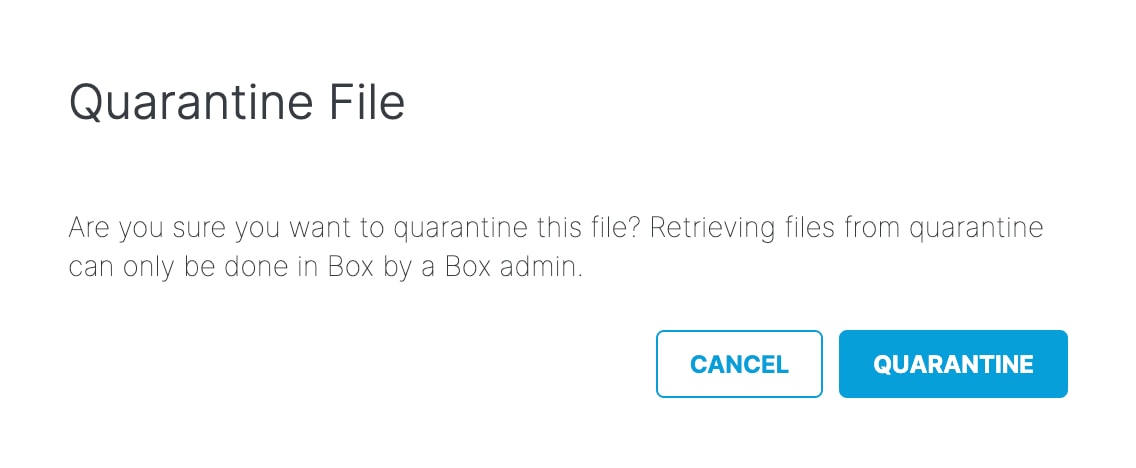
  2. A modal appears to verify if this is the file to be quarantined. Click Quarantine. The status will update in the report to Quarantine in Progress while the quarantine is processing. This process can take up to five minutes; when complete, the status will update to Quarantined.

    Quarantine attempts may fail if the files have been locked or blocked by settings within their native platforms. Settings local to the platform where a file resides take precedence over Secure Access' ability to detect or remediate DLP violations or malware.


    The Quarantine File interface.
    Note
    • For Microsoft OneDrive, SharePoint Online, Box, Dropbox, or Google Drive:

      • The file identified as exposing sensitive data is moved to the Cisco_Quarantine/DLP folder Secure Access created in the root path of the Global Admin who authorized the tenant.

      • The user who authorizes access to Secure Access will have access to the quarantine folder. All other accesses and collaborators are removed. Thus, we recommend that the admin add the relevant DLP Admins as additional collaborators to the folder.

    • For ServiceNow:

      • The file identified as exposing sensitive data is moved to a table named Cisco_Quarantine_Malware which can be access only by the admin user who authorized the ServiceNow tenant.

      • A footprint is attached to the notes\activities area of the table the file was originally attached to. This footprint will notify users that the file has been identified as malware, and for more information they should contact their administrator.

    • For Salesforce:

      Secure Access applies the Quarantine response action to files only (including those attached to chatter posts). Choose Quarantine to:

      • Remove all collaborators, and change the file owner to the Salesforce admin who has performed the authorization, and who has been assigned the permission set for the quarantine app. In Salesforce, the admin can see a list of quarantined files by using the App Launcher to search for "Cisco Secure Access SF Quarantine," then selecting the All Quarantines option.

        The Sfapp Launcher All Quarantines interface.

        Click on the listing for an individual file to see the information about it:

        The Sfquarantined File interface.
      • Replace the file in its original location with a text file named filename_Cisco_Quarantined.txt explaining to the original file owner that the file is identified as malware and for more information to contact their organization administrator.


Restore a Quarantined File

On the Microsoft OneDrive, Microsoft Teams (files only), SharePoint Online, Box, Dropbox, ServiceNow, Salesforce, or Google Drive platforms, you can restore a file that has previously been quarantined.

Note
Once a file has been quarantined and then restored, it cannot be quarantined again.

Before you begin

A minimum user role of Read-only. For more information, see Manage Accounts.

Procedure

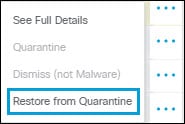
  1. Click the Action Menu to the right of the file that needs to be quarantined, then select Restore from Quarantine.


    The Restore Step One interface.
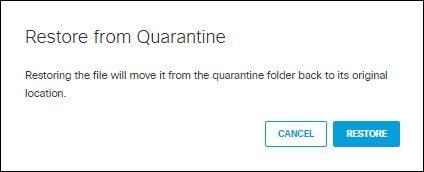
  2. A dialog box appears to verify the file is to be restored. Click RESTORE. The status will update to Restoration in Progress while the file is being processed. This can take up to five minutes; when complete, the status will update to Restored.


    The Restore Step Two interface.

    If you select Restore from Quarantine for Microsoft Teams Cloud Malware report:

    • Cloud Malware scans files only, so Quarantine and Restore apply to files. A file shared in a Teams message is scanned as a file and can be quarantined and restored in the same way.

    • Restore applies only to files. Secure Access cannot restore a quarantined message.

      To restore a quarantined file, open its event in the Cloud Malware report and select Restore from quarantine.

      After you restore a file, Secure Access moves it to its original folder with its original name and removes the tombstone file left there during quarantine. You can then find and open the file in the same location as before.

      For example, a91c3e-Q4-budget.xlsx returns to its original folder as Q4-budget.xlsx, and Q4-budget.xlsx*100245*Cisco_Quarantined.txt is removed.

    • Restore may fail in either of these cases:

      • A file with the same name already exists in the original folder. Rename or move the existing file, then try restoring again.

      • The quarantined file is no longer in the quarantine folder.

    • Secure Access does not modify Teams messages or update links already posted in chats. Link behavior after a restore depends on the file type:

      • Microsoft Office files: Microsoft assigns the restored file a new link. A link copied before the restore, including one posted in a Teams message, may return a “not found” (404) error. To get the new link, open the restored file in its original folder and copy the link again. This applies to:

        • Word: .doc, .docm, .docx, .dot, .dotm, .dotx

        • Excel: .xls, .xlsb, .xlsm, .xlsx, .xlt, .xltm, .xltx

        • PowerPoint: .ppt, .pptm, .pptx, .pps, .ppsm, .ppsx

      • Other file types: The restored file keeps its original link, so existing links work again.

    Note

    If your Cloud Malware deployment processes files from Microsoft OneDrive, SharePoint Online, Box, Dropbox, ServiceNow, Salesforce, or Google Drive and you restore a quarantined file that still violates rule criteria, the system will quarantine that file again. To prevent the system from quarantining the file again, remove the file's violation, or update the rule's criteria.

    Note

    If your Cloud Malware deployment processes files from Microsoft OneDrive, SharePoint Online, Box, Dropbox, ServiceNow, Salesforce, or Google Drive and you restore a quarantined file that still violates rule criteria, the system will quarantine that file again. To prevent the system from quarantining the file again, remove the file's violation, or update the rule's criteria.


Delete a Malicious File

For the Webex Teams platform, when a malicious file presents a potential risk and needs remediation, you can delete the file.

Before you begin

A minimum user role of Read-only. For more information, see Manage Accounts.

Procedure

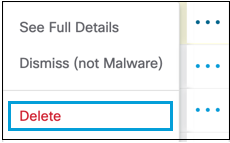
  1. Click the Action Menu for the file that needs to be quarantined and choose Delete.


    The 37c7ddd Malware Del Menu interface.
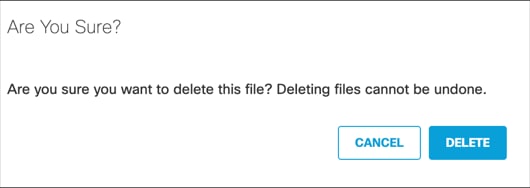
  2. A modal appears to verify if this is the file to be deleted. Click Delete. The report status is updated to Deleted.


    The C5d34a4 Malware Delete Dia interface.

Dismiss an Item from the Report

When a reported file is found to not present a risk, you can dismiss the file from the report.

Before you begin

A minimum user role of Read-only. For more information, see Manage Accounts.

Procedure

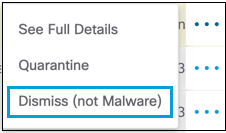
  1. Click the Action Menu for the file that needs to be removed from the report and choose Dismiss.


    The 3e2657b Malware Dismiss interface.
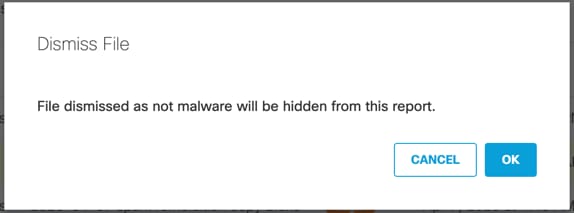
  2. A modal appears to verify if this is the file to be dismissed. Click OK. The file is removed from the report.


    The D25e68d Malware Dismiss Dia interface.

Export a Cloud Malware Report

You can export your Cloud Malware report to a CSV file for your records.

Before you begin

A minimum user role of Read-only. For more information, see Manage Accounts.

Procedure

  1. Click Download.


    The Download File interface.
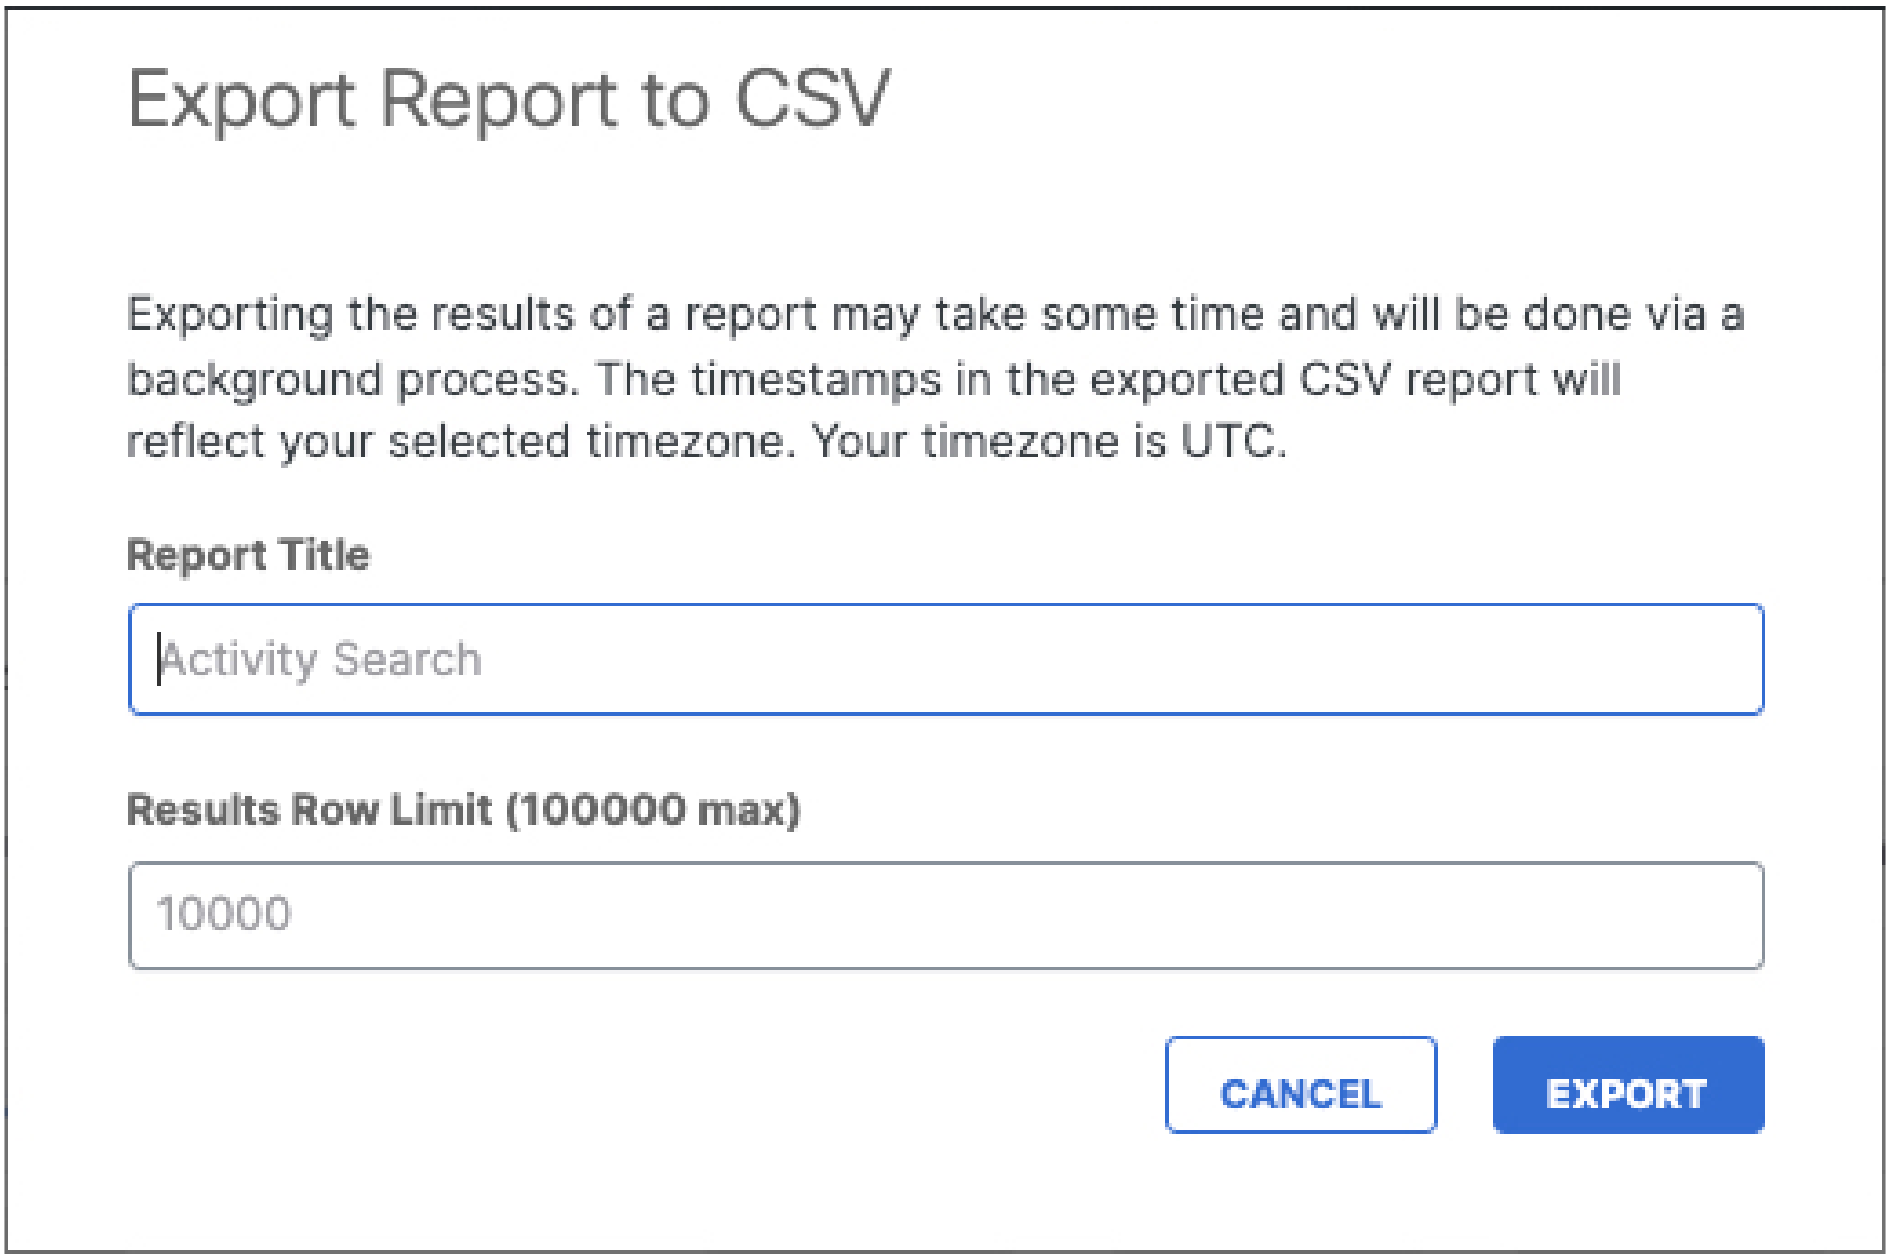
  2. Give your report a title and click Export.

    Note
    Data is limited to 100,000 rows when exporting to CSV.
    Export Report to CSV screen showing fields for Report Title and number of rows, with an Export button.
  3. When you click Export, you are taken to the Exported Reports page. Click the download icon in the download column to download the CSV file.