User Guide for AsyncOS 16.5 for Cisco Secure Email Gateway - GD (General Deployment)
Bias-Free Language
The documentation set for this product strives to use bias-free language. For the purposes of this documentation set, bias-free is defined as language that does not imply discrimination based on age, disability, gender, racial identity, ethnic identity, sexual orientation, socioeconomic status, and intersectionality. Exceptions may be present in the documentation due to language that is hardcoded in the user interfaces of the product software, language used based on RFP documentation, or language that is used by a referenced third-party product. Learn more about how Cisco is using Inclusive Language.
Sender IP reputation filtering is the first layer of spam protection, allowing you to control the messages that come through the email
gateway based on senders’ trustworthiness as determined by the
Sender IP Reputation Service.
The
email gateway can accept messages from known or highly reputable senders — such as customers and partners — and deliver them directly to
the end user without any content scanning. Messages from unknown or less reputable senders can be subjected to content scanning,
such as anti-spam and anti-virus scanning, and you can also throttle the number of messages you are willing to accept from
each sender. Email senders with the worst reputation can have their connections rejected or their messages bounced based on
your preferences.
The IP Reputation Service, using global data from the
Talos Affiliate network, assigns a IP Reputation Score (IPRS) to email senders based on complaint rates, message volume statistics, and data from public blocked lists and open proxy lists.
The IP Reputation Score helps to differentiate legitimate senders from spam sources. You can determine the threshold for blocking
messages from senders with low reputation scores.
The
Talos Security Network website ( https://talosintelligence.com) provides a global overview of the latest email and web-based threats, displays current email traffic volume by country,
and allows you to look up reputation scores based on IP address, URI or Domain.
Note
The IP Reputation Service is only available with a current anti-spam feature key.
The IP Reputation Score is a numeric value assigned to an IP address based on information from the IP Reputation Service. The IP Reputation Service aggregates data from over 25 public blocked lists and open proxy lists, and combines this data with global
data from
Talos to assign a score from -10.0 to +10.0, as follows:
Score
Meaning
-10.0
Most likely
to be a source of spam
0
Neutral, or
not enough information to make a recommendation
+10.0
Most likely
to be a trustworthy sender
The lower (more
negative) the score, the more likely that a message is spam. A score of -10.0
means that this message is “guaranteed” to be spam, while a score of 10.0 means
that the message is “guaranteed” to be legitimate.
Your Sending IP Address Has a Low or No IP Reputation Score
The IP Reputation Score, referred to as the SenderBase Reputation Scores (SBRS), are assigned to sending IP addresses based
on multiple reputation factors, including email volume, spam complaints, information from DNS-based blocklists, and sender
behavior.
The SBRS value ranges from -10.0 to +10.0. The score reflects the likelihood that mail from the IP address is spam. Highly
negative scores indicate that the IP address is more likely to be sending spam, while highly positive scores indicate a better
sender reputation.
When an organization first begins sending mail through a Cisco Secure Email Gateway, the public sending IP address of the
gateway or upstream Mail Transfer Agents (MTA) may have a score of none or a low positive score. A score of none or a low
positive score is not necessarily a problem.
A low or None score for your sending IP address can occur for several reasons, such as:
Lack of sending history for the IP address
Low mail volume from the IP address
Occasional or repeated spam complaints
Listing on DNS-based blocklists
Cisco does not recommend throttling or blocking mail solely because an IP address has a positive score. A typical MTA score
in the range of 0 to 3.5 is generally not a cause for concern.
Negative scores require investigation. A negative score can indicate that the IP address has generated complaints, appears
on DNS-based block lists, or is otherwise suspected of sending spam. To improve a negative score, investigate and correct
the source of the reputation problem. For example:
Check whether the sending IP address appears on DNS-based block lists.
Identify and remediate infected or unauthorized hosts that may be sending spam through your network.
Review outbound mail volume and complaint patterns.
Verify that only authorized systems can relay mail through the gateway.
Use Talos Intelligence reputation lookup to review reputation information for the IP address.
If the IP address is not listed on any block list and the reason for the negative score is unclear, contact Cisco Support.
Using the
IP Reputation Score, you configure the
email gateway to apply mail flow policies to senders based on their trustworthiness. (You can also create message filters to specify “thresholds”
for
IP Reputation Scores to further act upon messages processed by the system. For more information, refer to “IP Reputation Rule” and “Bypass Anti-Spam System Action.”)
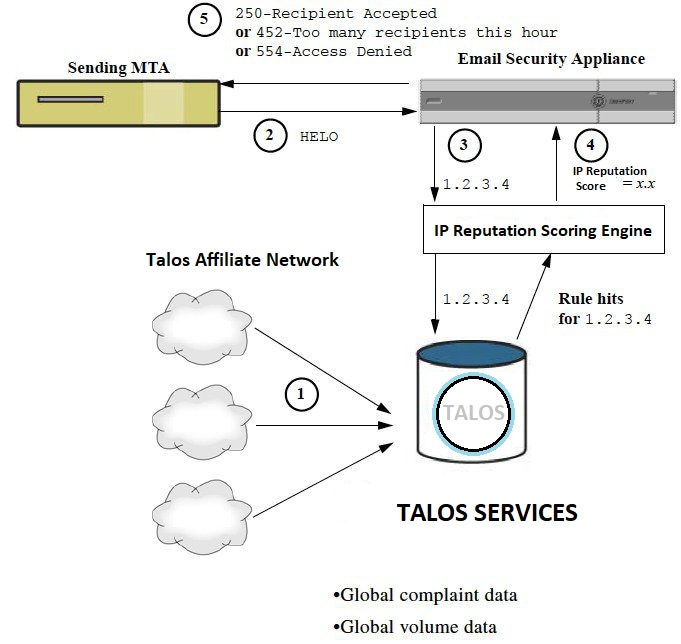
Figure 1. The IP Reputation Service
Talos affiliates send real-time, global data
Sending MTA opens connection with the
email gateway
Email gateway checks global data for the connecting IP address
IP Reputation Service calculates the probability that this message is spam and assigns
an IP Reputations Score
Cisco returns the response based on the
IP Reputation Score
How Sender IP Reputation Filters Work
Sender IP Reputation filter technology aims to shunt as much mail as possible from the remaining security services processing that
is available on the
email gateway. (See Understanding the Email Pipeline.)
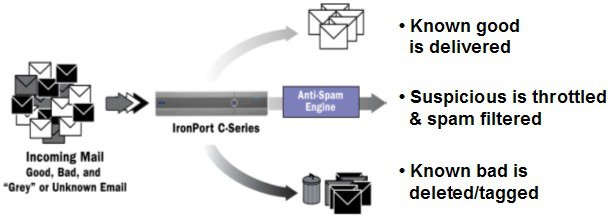
When sender reputation filtering is enabled, mail from known bad senders is simply refused. Known good mail from global 2000
companies is automatically routed around the spam filters, reducing the chance of false positives. Unknown, or “grey” email
is routed to the anti-spam scanning engine. Using this approach, Sender IP Reputation filters can reduce the load on the content filters by as much as 50%.
Figure 2. Sender IP Reputation Filtering Example
Recommended Settings for Different Sender IP Reputation Filtering Approaches
Depending on the
objectives of your enterprise, you can implement a conservative, moderate, or
aggressive approach.
Approach
Characteristics
Allowed _List
Blocked_ List
Suspectlist
Unknownlist
Sender IP Reputation Score range:
Conservative
Near zero false positives, better performance
7 to 10
-10 to -4
-4 to -2
-2 to 7
Moderate
(Installation default)
Very few false positives, high performance
Sender IPReputation Scores are not used.
-10 to -3
-3 to -1
-1 to +10
Aggressive
Some false positives, maximum performance.
This option shunts the most mail away from Anti-Spam
processing.
4 to 10
-10 to -2
-2 to -1
-1 to 4
All approaches
Mail Flow Policy:
Trusted
Blocked
Throttled
Accepted
Editing
IP Reputation Filtering Score Thresholds for a Listener
Use this procedure if you want to change the default
IP Reputation Service score thresholds or add a sender group for reputation filtering.
Testing
IP Reputation Filtering Using the
IP Reputation Scores
Unless you regularly receive a large portion of spam, or you have set up “dummy” accounts to specifically receive spam for
your organization, it may be difficult to immediately test the IP Reputation policies you have implemented. However, if you add entries for reputation filtering with IP Reputation Scores into a listener’s HAT as indicated in the following table, you will notice that a smaller percentage of inbound mail
will be “unclassified.”
Test the policies using the trace command with an arbitrary IP Reputation scores. See Debugging Mail Flow Using Test Messages: Trace. The trace command is available in the CLI as well as the GUI.
Table 1. Suggested Mail Flow Policies for Implementing the IP Reputation Scores
Policy Name
Primary
Behavior (Access Rule)
Parameters
Value
$BLOCKED
REJECT
None
$THROTTLED
ACCEPT
Maximum
messages / session:
Maximum
recipients / message:
Maximum
message size:
Maximum
concurrent connections:
Use Spam
Detection:
Use TLS:
Maximum
recipients / hour:
Use
SenderBase:
10
20
1 MB
10
ON
OFF
20
(recommended)
ON
$ACCEPTED
(Public
Listener)
ACCEPT
Maximum
messages / session:
Maximum
recipients / message:
Maximum
message size:
Maximum
concurrent connections:
Use Spam
Detection:
Use TLS:
Use
SenderBase:
1,000
1,000
100 MB
1,000
ON
OFF
ON
$TRUSTED
ACCEPT
Maximum
messages / session:
Maximum
recipients / message:
Maximum
message size:
Maximum
concurrent connections:
Use Spam
Detection:
Use TLS:
Maximum
recipients / hour:
Use
SenderBase:
1,000
1,000
100 MB
1,000
OFF
OFF
-1
(disabled)
OFF
Note
In the
$THROTTLED policy, the maximum recipients per hour from the remote host is set
to 20 recipients per hour, by default. Note that this setting controls the
maximum throttling available. You can increase the number of recipients to
receive per hour if this parameter is too aggressive. For more information on
Default Host Access policies, see
Understanding Predefined Sender Groups and Mail Flow Policies.
Entering Low
IP Reputation Scores in the Message Subject
Although Cisco recommends throttling, an alternate way to use the IP Reputation Service is to modify the subject line of suspected spam messages. To do this, use the message filter shown in
the following table. This filter uses the reputation filter rule and the strip-header and insert-header filter actions to
replace the subject line of messages having a IP Reputation Score lower than -2.0 with a subject line that includes the actual IP Reputation Score represented as: {Spam IP Reputation Score}. Replace listener_name in this example with the name of your public listener. (The period on its own line is included so that you can cut and paste
this text directly into the command line interface of the filters command.)
Table: Message Filter to Modify Subject Header with IP Reputation: Example 1
iprs_filter:
if ((recv-inj == "listener_name
" AND subject != "\\{Spam -?[0-9.]+\\}"))

 Feedback
