Cisco Security Cloud Control: Secure Firewall Management

PDF

Cisco Security Cloud Control: Secure Firewall Management

Network objects

Want to summarize with AI?

Log in

Learn how to manage network objects and network groups for hosts, networks, IP ranges, FQDNs, access rules, policies, and NAT rules.


A network object can contain a host name, a network IP address, a range of IP addresses, a fully qualified domain name (FQDN), or a subnetwork expressed in CIDR notation. Network groups are collections of network objects and other individual addresses or subnetworks that you add to the group. Network objects and network groups are used in access rules, network policies, and NAT rules.

Not all platforms support network objects, such as Cisco Meraki and Multicloud Defense; when you share dynamic objects, Security Cloud Control Firewall Management automatically translates the appropriate information from the originating platform or device into a set of usable information that Security Cloud Control Firewall Management can use.

Table 1. Permitted Contents of a Network Group

Device type

IP Value

Network Object

Network Groups

ASA

Yes

Yes

Yes

FTD

No

Yes

Yes

Meraki

Yes

Yes

Yes

Multicloud Defense

Yes

Yes

Yes

Reuse network objects across products

If you have a Security Cloud Control tenant with a Cloud-Delivered Firewall Management Center and one or more On-Premises Firewall Management Centers onboarded to your tenant:

  • When you create a Secure Firewall Threat Defense, FDM-managed Firewall Threat Defense, ASA, or Meraki network object or group, a copy of the object is also added to the objects list on the Objects page used when configuring Cloud-Delivered Firewall Management Center, and vice versa.

  • When you create a Secure Firewall Threat Defense, FDM-managed Firewall Threat Defense, or ASA network object or group, an entry is created in the Devices with Pending Changes page for each On-Premises Firewall Management Center for which Discover & Manage Network Objects is enabled. From this list, you can choose and deploy the object to the On-Premises Firewall Management Center on which you want to use the object and discard the ones that you do not want. Navigate , Administration > Firewall Management Center select the On-Premises Firewall Management Center, and click Objects to see your objects in the On-Premises Firewall Management Center user interface and assign them to policies.

Changes you make to network objects or groups on either page apply to the object or group instance on both pages. Deleting an object from one page also deletes the corresponding copy of the object from the other page.

The following exceptions apply:

  • If a network object of the same name already exists for Cloud-Delivered Firewall Management Center, the new Secure Firewall Threat Defense, FDM-managed Firewall Threat Defense, ASA, or Meraki network object will not be replicated on the Objects page of Security Cloud Control.

  • Network objects and groups in onboarded Firewall Threat Defense devices that are managed by on-premises Secure Firewall Management Center are not replicated and cannot be used in Cloud-Delivered Firewall Management Center.

    Note that for on-premises Secure Firewall Management Center instances that have been migrated to Cloud-Delivered Firewall Management Center, network objects and groups are replicated to the Security Cloud Control objects page if they are used in policies that were deployed to FTD devices.

  • Sharing Network Objects between Security Cloud Control and Cloud-Delivered Firewall Management Center is automatically enabled on new tenants but must be requested for existing tenants. If your network objects are not being shared with Cloud-Delivered Firewall Management Center, contact TAC to have the features enabled on your tenant.

  • Sharing network objects between Security Cloud Control and On-Premises Firewall Management Center is not automatically enabled on Security Cloud Control for new On-Premises Firewall Management Centers onboarded to Security Cloud Control. If your network objects are not being shared with On-Premises Firewall Management Center, ensure the Discover & Manage Network Objects toggle button is enabled for the On-Premises Firewall Management Center in Settings or contact TAC to have the features enabled on your tenant.

Viewing network objects

Network objects that you create in Security Cloud Control Firewall Management, and network objects that Security Cloud Control Firewall Management recognizes in onboarded device configurations, appear on the Objects page. They are labeled with their object type. This allows you to filter by object type to quickly find the object you are looking for.

When you select a network object, the Details pane shows the object values. The Relationships pane shows whether the object is used in a policy and which device stores the object.

When you select a network group, Security Cloud Control Firewall Management shows the contents of the group as the combined values from the network objects in that group.


Create or Edit ASA Network Objects and Network Groups

An ASA network object can contain a hostname, an IP address, or a subnet address expressed in CIDR notation. Network groups are conglomerates of network objects, network groups, and IP addresses that are used in access rules, network policies, and NAT rules. You can create, read, update, and delete network objects and network groups using Security Cloud Control.

Table 2. Permitted Values of ASA Network Objects and Groups

Device type

IPv4 / IPv6

Single Address

Range of addresses

Partially Qualified Domain Name (PQDN)

Subnet using CIDR Notation

ASA

IPv4 / IPv6

Yes

Yes

Yes

Yes

Note

If Cloud-Delivered Firewall Management Center is deployed on your tenant:

When you create an FTD, FDM, or ASA network object or group on the Objects page, a copy of the object is automatically added to the Cloud-Delivered Firewall Management Center and vice-versa. In addition, an entry is created in the Devices with Pending Changes page for each On-Premises Firewall Management Center with Discover & Manage Network Objects enabled, from which you can choose and deploy the objects to the On-Premises Firewall Management Center on which you want these objects.

Note

If Cloud-Delivered Firewall Management Center is deployed on your tenant:

Changes you make to the ASA, FDM, and FTD network objects and groups are reflected in the corresponding Cloud-Delivered Firewall Management Center network object or group. In addition, an entry is created in the Devices with Pending Changes page for each On-Premises Firewall Management Center with Discover & Manage Network Objects enabled, from which you can choose and deploy the changes to the On-Premises Firewall Management Center on which you have these objects.

Deleting a network object or group from either page deletes the object or group from both pages.


Create an ASA Network Object

A network object can contain a host name, a network IP address, a range of IP addresses, a fully qualified domain name (FQDN), or a subnetwork expressed in CIDR notation. Network objects are used in access rules, network policies, and NAT rules. You can create, update, and delete network objects and network groups using Security Cloud Control.

Note

If Cloud-Delivered Firewall Management Center is deployed on your tenant:

When you create an FTD, FDM, or ASA network object or group on the Objects page, a copy of the object is automatically added to the Cloud-Delivered Firewall Management Center and vice-versa. In addition, an entry is created in the Devices with Pending Changes page for each On-Premises Firewall Management Center with Discover & Manage Network Objects enabled, from which you can choose and deploy the objects to the On-Premises Firewall Management Center on which you want these objects.

Procedure

  1. From the Security Cloud Control Home page, click Firewall.

  2. In the left pane, click Objects.

  3. Click the blue plus button to create an object.

  4. Click ASA > Network.

  5. Enter an object name.

  6. Select Create a network object.

  7. (optional) Enter an object description.

  8. In the Value section, add the IP address information in one of these ways:

    • Select eq and then enter a single IP address, a subnet address using CIDR notation, or a Partially Qualified Domain Name (PQDN).

    • Select range and then enter a range of IP addresses. Enter the range with the beginning and ending address in the range separated by a space. For example, 10.1.1.1 10.1.1.255 or 2001:DB8:1::1 2001:DB8:1::3

  9. Click Add.

    The newly created network objects aren't associated with any ASA device as they aren't part of any rule or policy. To see these objects, select the Unassociated objects category in object filters.

    For more information, see Object Filters. Once you use the unassociated objects in a device's rule or policy, such objects are associated with that device.


Create an ASA Network Group

A network group can contain IP address values, network objects, and network groups. When you are creating a new network group, you can search for existing objects by their name, IP addresses, IP address range, or FQDN and add them to the network group. If the object isn't present, you can instantly create that object in the same interface and add it to the network group. Network groups can contain both IPv4 and IPv6 addresses.

Note

If Cloud-Delivered Firewall Management Center is deployed on your tenant:

When you create an FTD, FDM, or ASA network object or group on the Objects page, a copy of the object is automatically added to the Cloud-Delivered Firewall Management Center and vice-versa. In addition, an entry is created in the Devices with Pending Changes page for each On-Premises Firewall Management Center with Discover & Manage Network Objects enabled, from which you can choose and deploy the objects to the On-Premises Firewall Management Center on which you want these objects.

Procedure

  1. From the Security Cloud Control Home page, click Firewall.

  2. In the left pane, click Objects.

  3. Click the blue plus button to create an object.

  4. Click ASA > Network.

  5. Enter an Object Name.

  6. Select Create a network group.

  7. (optional) Enter an object description.

  8. In the Values field, enter a value or object name. When you start typing, Security Cloud Control provides object names or values that match your entry.

  9. You can choose one of the existing objects shown or create a new one based on the name or value that you have entered.

  10. If Security Cloud Control finds a match, to choose an existing object, click Add to add the network object or network group to the new network group.

  11. If you have entered a value or object that is not present, you can perform one of the following:

    • Click Add as New Object With This Name to create a new object with that name. Enter a value and click the check mark to save it.

    • Click Add as New Object to create a new object. The object name and value are the same. Enter a name and click the check mark to save it.

    • Click Add Value to create an inline value without using an object. Enter a value and click the check mark to save it.

    It is possible to create a new object even though the value is already present. You can make changes to those objects and save them.

    Note

    You can click the edit icon to modify the details. Clicking the delete button doesn't delete the object itself; instead, it removes it from the network group.

  12. After adding the required objects, click Add to create a new network group.

  13. Preview and deploy configuration changes for all devices.


Edit an ASA Network Object

Note

If Cloud-Delivered Firewall Management Center is deployed on your tenant:

Changes you make to the ASA, FDM, and FTD network objects and groups are reflected in the corresponding Cloud-Delivered Firewall Management Center network object or group. In addition, an entry is created in the Devices with Pending Changes page for each On-Premises Firewall Management Center with Discover & Manage Network Objects enabled, from which you can choose and deploy the changes to the On-Premises Firewall Management Center on which you have these objects.

Deleting a network object or group from either page deletes the object or group from both pages.

Procedure

  1. From the Security Cloud Control Home page, click Firewall.

  2. In the left pane, click Objects.

  3. Locate the object you want to edit by using object filters and search field.

  4. Select the network object and click the edit icon in the Actions pane.

  5. Edit the values in the dialog box in the same fashion that you created in the procedures above.

    Note

    Click the delete icon next to remove the object from the network group.

  6. Click Save. Security Cloud Control displays the devices that will be affected by the change.

  7. Click Confirm to finalize the change to the object and any devices affected by it.


Edit an ASA Network Group

Note

If Cloud-Delivered Firewall Management Center is deployed on your tenant:

Changes you make to the ASA, FDM, and FTD network objects and groups are reflected in the corresponding Cloud-Delivered Firewall Management Center network object or group. In addition, an entry is created in the Devices with Pending Changes page for each On-Premises Firewall Management Center with Discover & Manage Network Objects enabled, from which you can choose and deploy the changes to the On-Premises Firewall Management Center on which you have these objects.

Deleting a network object or group from either page deletes the object or group from both pages.

Procedure

  1. From the Security Cloud Control Home page, click Firewall.

  2. In the left pane, click Objects.

  3. Locate the network group you want to edit by using object filters and search field.

  4. Select the network group and click the edit icon in the Actions pane.

  5. If you want to change the objects or network groups that are already added to the network group, perform the following steps:

    1. Click the edit icon appearing beside the object name or network group to modify them.
    2. Click the checkmark to save your changes.

    Note

    You can click the remove icon to delete the value from a network group.

  6. If you want to add new network objects or network groups to this network group, you have to perform the following steps:

    1. In the Values field, enter a new value or the name of an existing network object. When you start typing, Security Cloud Control provides object names or values that match your entry. You can choose one of the existing objects shown or create a new one based on the name or value that you have entered.

    2. If Security Cloud Control finds a match, to choose an existing object, click Add to add the network object, or network group to the new network group.

    3. If you have entered a value or object that is not present, you can perform one of the following:

      • Click Add as New Object With This Name to create a new object with that name. Enter a value and click the checkmark to save it.

      • Click Add as New Object to create a new object. The object name and value are the same. Enter a name and click the checkmark to save it.

      • Click Add Value to create an inline value without using an object. Enter a value and click the checkmark to save it.

    It is possible to create a new object even though the value is already present. You can make changes to those objects and save them.

  7. Click Save. Security Cloud Control displays the policies that will be affected by the change.

  8. Click Confirm to finalize the change to the object and any devices affected by it.

  9. Preview and deploy configuration changes for all devices.


Add Additional Values to a Shared Network Group in Security Cloud Control

The values in a shared network group that are present on all devices associated with it are called "default values." Security Cloud Control allows you to add "additional values" to the shared network group and assign those values to some devices associated with that shared network group. When Security Cloud Control deploys the changes to the devices, it determines the contents and pushes the "default values" to all devices associated with the shared network group and the "additional values" only to the specified devices.

For example, consider a scenario where you have four AD main servers in your head office that should be accessible from all your sites. Therefore, you have created an object group named "Active-Directory" to use it in all your sites. Now you want to add two more AD servers to one of your branch offices. You can do this by adding their details as additional values specific to that branch office on the object group "Active-Directory." These two servers do not participate in determining whether the object "Active-Directory" is consistent or shared. Therefore, the four AD main servers are accessible from all your sites, but the branch office (with two additional servers) can access two AD servers and four AD main servers.

Note

If there are inconsistent shared network groups, you can combine them into a single shared network group with additional values. See Resolve Inconsistent Object Issues for more information.

Note

If Cloud-Delivered Firewall Management Center is deployed on your tenant:

Changes you make to the ASA, FDM, and FTD network objects and groups are reflected in the corresponding Cloud-Delivered Firewall Management Center network object or group. In addition, an entry is created in the Devices with Pending Changes page for each On-Premises Firewall Management Center with Discover & Manage Network Objects enabled, from which you can choose and deploy the changes to the On-Premises Firewall Management Center on which you have these objects.

Deleting a network object or group from either page deletes the object or group from both pages.

Procedure

  1. From the Security Cloud Control Home page, click Firewall.

  2. In the left pane, click Objects.

  3. Locate the shared network group that you want to edit by using object filters and search field.

  4. Click the edit icon in the Actions pane.

    • The Devices field shows the devices that the shared network group is present.

    • The Usage field shows the rulesets associated with the shared network group.

    • The Default Values field specifies the default network objects and their values associated with the shared network group that was provided during their creation. Next to this field, you can see the number of devices that contain this default value, and you can click to see their names and device types. You can also see the rulesets associated with this value.

  5. In the Additional Values field, enter a value or name. When you start typing, Security Cloud Control provides object names or values that match your entry.

  6. You can choose one of the existing objects shown or create a new one based on the name or value that you have entered.

  7. If Security Cloud Control finds a match, to choose an existing object, click Add to add the network object or network group to the new network group.

  8. If you have entered a value or object that is not present, you can perform one of the following:

    • Click Add as New Object With This Name to create a new object with that name. Enter a value and click the checkmark to save it.

    • Click Add as New Object to create a new object. The object name and value are the same. Enter a name and click the checkmark to save it.

    • Click Add Value to create an inline value without using an object. Enter a value and click the checkmark to save it.

    It is possible to create a new object even though the value is already present. You can make changes to those objects and save them.

  9. In the Devices column, click the cell associated with the newly added object and click Add Devices.

  10. Select the devices that you want and click OK.

  11. Click Save. Security Cloud Control displays the devices that will be affected by the change.

  12. Click Confirm to finalize the change to the object and any devices affected by it.

  13. Preview and deploy configuration changes for all devices.


Edit Additional Values in a Shared Network Group in Security Cloud Control

Note

If Cloud-Delivered Firewall Management Center is deployed on your tenant:

Changes you make to the ASA, FDM, and FTD network objects and groups are reflected in the corresponding Cloud-Delivered Firewall Management Center network object or group. In addition, an entry is created in the Devices with Pending Changes page for each On-Premises Firewall Management Center with Discover & Manage Network Objects enabled, from which you can choose and deploy the changes to the On-Premises Firewall Management Center on which you have these objects.

Deleting a network object or group from either page deletes the object or group from both pages.

Procedure

  1. From the Security Cloud Control Home page, click Firewall.

  2. In the left pane, click Objects.

  3. Locate the object having the override you want to edit by using object filters and search field.

  4. Click the edit icon in the Actions pane.

  5. Modify the override value:

    • Click the edit icon to modify the value.

    • Click the cell in the Devices column to assign new devices. You can select an already assigned device and click Remove Overrides to remove overrides on that device.

    • Click arrow in Default Values to push and make it an additional value of the shared network group. All devices associated with the shared network group are automatically assigned to it.

    • Click arrow in Override Values to push and make it as default objects of the shared network group.

    • Click the delete icon next to remove the object from the network group.

  6. Click Save. Security Cloud Control displays the devices that will be affected by the change.

  7. Click Confirm to finalize the change to the object and any devices affected by it.

  8. Preview and deploy configuration changes for all devices.


Deleting Network Objects and Groups in Security Cloud Control

If Cloud-Delivered Firewall Management Center is deployed on your tenant:

Deleting a network object or group from the Objects page deletes the replicated network object or group from the Objects page on the Cloud-Delivered Firewall Management Center and vice-versa.


Create or Edit a Firepower Network Object or Network Groups

A Firepower network object can contain a hostname, an IP address, or a subnet address expressed in CIDR notation. Network groups are conglomerates of network objects and network groups that are used in access rules, network policies, and NAT rules. You can create, read, update, and delete network objects and network groups using Security Cloud Control.

Firepower network objects and groups can be used by ASA, Firewall Threat Defense, FDM-managed, and Meraki devices. See Reuse network objects across products.

Note

If Cloud-Delivered Firewall Management Center is deployed on your tenant:

When you create an FTD, FDM, or ASA network object or group on the Objects page, a copy of the object is automatically added to the Cloud-Delivered Firewall Management Center and vice-versa. In addition, an entry is created in the Devices with Pending Changes page for each On-Premises Firewall Management Center with Discover & Manage Network Objects enabled, from which you can choose and deploy the objects to the On-Premises Firewall Management Center on which you want these objects.

Note

If Cloud-Delivered Firewall Management Center is deployed on your tenant:

Changes you make to the ASA, FDM, and FTD network objects and groups are reflected in the corresponding Cloud-Delivered Firewall Management Center network object or group. In addition, an entry is created in the Devices with Pending Changes page for each On-Premises Firewall Management Center with Discover & Manage Network Objects enabled, from which you can choose and deploy the changes to the On-Premises Firewall Management Center on which you have these objects.

Deleting a network object or group from either page deletes the object or group from both pages.

Table 3. IP addresses that can be added to network objects

Device type

IPv4 / IPv6

Single Address

Range of addresses

Partially Qualified Domain Name (PQDN)

Subnet using CIDR Notation

Firepower IPv4 / IPv6 Yes Yes Yes Yes

Create a Firepower Network Object

Note

If Cloud-Delivered Firewall Management Center is deployed on your tenant:

When you create an FTD, FDM, or ASA network object or group on the Objects page, a copy of the object is automatically added to the Cloud-Delivered Firewall Management Center and vice-versa. In addition, an entry is created in the Devices with Pending Changes page for each On-Premises Firewall Management Center with Discover & Manage Network Objects enabled, from which you can choose and deploy the objects to the On-Premises Firewall Management Center on which you want these objects.

Procedure

  1. From the Security Cloud Control Home page, click Firewall.

  2. In the left pane, click Objects.

  3. Click the blue plus button to create an object.

  4. Click FTD > Network.

  5. Enter an Object Name.

  6. Select Create a network object.

  7. In the Value section:

    • Select eq and enter a single IP address, a subnet address expressed in CIDR notation, or a Partially Qualified Domain Name (PQDN).

    • Select range and enter an IP address range.

    Note

    Do not set a host bit value. If you enter a host bit value other than 0, Security Cloud Control unsets it while creating the object, because the Cloud-Delivered Firewall Management Center only accepts IPv6 objects with host bits not set.

  8. Click Add.

    Attention: The newly created network objects aren't associated with any FDM-managed device as they aren't part of any rule or policy. To see these objects, select the Unassociated objects category in object filters. For more information, see Object Filters. Once you use the unassociated objects in a device's rule or policy, such objects are associated with that device.


Create a Firepower Network Group

A network group can contain network objects and network groups. When you create a new network group, you can search for existing objects by their name, IP addresses, IP address range, or FQDN and add them to the network group. If the object isn't present, you can instantly create that object in the same interface and add it to the network group.

Note

If Cloud-Delivered Firewall Management Center is deployed on your tenant:

When you create an FTD, FDM, or ASA network object or group on the Objects page, a copy of the object is automatically added to the Cloud-Delivered Firewall Management Center and vice-versa. In addition, an entry is created in the Devices with Pending Changes page for each On-Premises Firewall Management Center with Discover & Manage Network Objects enabled, from which you can choose and deploy the objects to the On-Premises Firewall Management Center on which you want these objects.

Procedure

  1. From the Security Cloud Control Home page, click Firewall.

  2. In the left pane, click Objects.

  3. Click the blue plus button to create an object.

  4. Click FTD > Network.

  5. Enter an Object Name.

  6. Select Create a network group.

  7. In the Values field, enter a value or name. When you start typing, Security Cloud Control provides object names or values that match your entry.

  8. You can choose one of the existing objects shown or create a new one based on the name or value that you have entered.

  9. If Security Cloud Control finds a match, to choose an existing object, click Add to add the network object or network group to the new network group.

  10. If you have entered a value or object that is not present, you can perform one of the following:

    • Click Add as New Object With This Name to create a new object with that name. Enter a value and click the checkmark to save it.

    • Click Add as New Object to create a new object. The object name and value are the same. Enter a name and click the checkmark to save it.

    It is possible to create a new object even though the value is already present. You can make changes to those objects and save them.

    Note: You can click the edit icon to modify the details. Clicking the delete button doesn't delete the object itself; instead, it removes it from the network group.

  11. After adding the required objects, click Save to create a new network group.

  12. Preview and Deploy Configuration Changes for All Devices.


Edit a Firepower Network Object

Note

If Cloud-Delivered Firewall Management Center is deployed on your tenant:

Changes you make to the ASA, FDM, and FTD network objects and groups are reflected in the corresponding Cloud-Delivered Firewall Management Center network object or group. In addition, an entry is created in the Devices with Pending Changes page for each On-Premises Firewall Management Center with Discover & Manage Network Objects enabled, from which you can choose and deploy the changes to the On-Premises Firewall Management Center on which you have these objects.

Deleting a network object or group from either page deletes the object or group from both pages.

Procedure

  1. From the Security Cloud Control Home page, click Firewall.

  2. In the left pane, click Objects.

  3. Locate the object you want to edit by using object filters and search field.

  4. Select the network object and click the edit icon in the Actions pane.

  5. Edit the values in the dialog box in the same fashion that you created them in "Create a Firepower Network Group".

    Note
    Click the delete icon next to remove the object from the network group.
  6. Click Save. Security Cloud Control displays the devices that will be affected by the change.

  7. Click Confirm to finalize the change to the object and any devices affected by it.


Edit a Firepower Network Group

Note

If Cloud-Delivered Firewall Management Center is deployed on your tenant:

Changes you make to the ASA, FDM, and FTD network objects and groups are reflected in the corresponding Cloud-Delivered Firewall Management Center network object or group. In addition, an entry is created in the Devices with Pending Changes page for each On-Premises Firewall Management Center with Discover & Manage Network Objects enabled, from which you can choose and deploy the changes to the On-Premises Firewall Management Center on which you have these objects.

Deleting a network object or group from either page deletes the object or group from both pages.

Procedure

  1. From the Security Cloud Control Home page, click Firewall.

  2. In the left pane, click Objects.

  3. Locate the network group you want to edit by using object filters and search field.

  4. Select the network group and click the edit icon in the Actions pane.

  5. Change the object name and description if needed.

  6. If you want to change the objects or network groups that are already added to the network group, perform the following steps:

    1. Click the edit icon appearing beside the object name or network group to modify them.

    2. Click the checkmark to save your changes. Note: You can click the remove icon to delete the value from a network group.

  7. If you want to add new network objects or network groups to this network group, you have to perform the following steps:

    1. In the Values field, enter a new value or the name of an existing network object. When you start typing, Security Cloud Control provides object names or values that match your entry. You can choose one of the existing objects shown or create a new one based on the name or value that you have entered.

    2. If Security Cloud Control finds a match, to choose an existing object, click Add to add the network object or network group to the new network group.

    3. If you have entered a value or object that is not present, you can perform one of the following:

      • Click Add as New Object With This Name to create a new object with that name. Enter a value and click the checkmark to save it.

      • Click Add as New Object to create a new object. The object name and value are the same. Enter a name and click the checkmark to save it.

    It's is possible to create a new object even though the value is already present. You can make changes to those objects and save them.

  8. Click Save. Security Cloud Control displays the policies that will be affected by the change.

  9. Click Confirm to finalize the change to the object and any devices affected by it.

  10. Preview and Deploy Configuration Changes for All Devices.


Add an Object Override

Note

If Cloud-Delivered Firewall Management Center is deployed on your tenant:

Changes you make to the ASA, FDM, and FTD network objects and groups are reflected in the corresponding Cloud-Delivered Firewall Management Center network object or group. In addition, an entry is created in the Devices with Pending Changes page for each On-Premises Firewall Management Center with Discover & Manage Network Objects enabled, from which you can choose and deploy the changes to the On-Premises Firewall Management Center on which you have these objects.

Deleting a network object or group from either page deletes the object or group from both pages.

Procedure

  1. From the Security Cloud Control Home page, click Firewall.

  2. In the left pane, click Objects.

  3. Locate the object to which you want to add an override, using object filters and search field.

  4. Select the network object and click the edit icon in the Actions pane.

  5. Enter the value in the Override Values dialog box and click + Add Value.

    The override you are adding must have the same type of value that the object contains. For example, to a network object, you can configure an override only with a network value and not a host value.
  6. Once you see that the value is added, click the cell in the Devices column in Override Values.

  7. Click Add Devices, and choose the device to which you want the override to be added. The device you select must contain the object to which you are adding the override.

  8. Click Save. Security Cloud Control displays the devices that will be affected by the change.

  9. Click Confirm to finalize the addition of the override to the object and any devices affected by it.

    Note
    You can add more than one override to an object. However, you must select a different device, which contains the object, each time you are adding an override.
  10. See Object Overrides to know more about object overrides and Edit Object Overrides to edit an existing override.


Edit Object Overrides

You can modify the value of an existing override as long as the object is present on the device.

Procedure

  1. From the Security Cloud Control Home page, click Firewall.

  2. Navigate to Objects.

  3. Locate the object having override you want to edit by using object filters and search field.

  4. Select the object having override and click the edit icon in the Actions pane.

  5. Modify the override value:

    • Click the edit icon to modify the value.

    • Click on the cell in the Devices column in Override Values to assign new devices. You can select an already assigned device and click Remove Overrides to remove overrides on that device.

    • Click arrow in Override Values to push and make it as the default value of the shared object.

    • Click the delete icon next to the override you want to remove.

  6. Click Save. Security Cloud Control displays the devices that will be affected by the change.

  7. Click Confirm to finalize the change to the object and any devices affected by it.

  8. Preview and Deploy Configuration Changes for All Devices.


Add Additional Values to a Shared Network Group

The values in a shared network group that are present on all devices associated with it are called "default values." Security Cloud Control allows you to add "additional values" to the shared network group and assign those values to some devices associated with that shared network group. When Security Cloud Control deploys the changes to the devices, it determines the contents and pushes the "default values" to all devices associated with the shared network group and the "additional values" only to the specified devices.

For example, consider a scenario where you have four AD main servers in your head office that should be accessible from all your sites. Therefore, you have created an object group named "Active-Directory" to use in all your sites. Now you want to add two more AD servers to one of your branch offices. You can do this by adding their details as additional values specific to that branch office on the object group "Active-Directory." These two servers do not participate in determining whether the object "Active-Directory" is consistent or shared. Therefore, the four AD main servers are accessible from all your sites, but the branch office (with two additional servers) can access two AD servers and four AD main servers.

Note

If there are inconsistent shared network groups, you can combine them into a single shared network group with additional values. See Resolve Inconsistent Object Issues for more information.

Note

If Cloud-Delivered Firewall Management Center is deployed on your tenant:

Changes you make to the ASA, FDM, and FTD network objects and groups are reflected in the corresponding Cloud-Delivered Firewall Management Center network object or group. In addition, an entry is created in the Devices with Pending Changes page for each On-Premises Firewall Management Center with Discover & Manage Network Objects enabled, from which you can choose and deploy the changes to the On-Premises Firewall Management Center on which you have these objects.

Deleting a network object or group from either page deletes the object or group from both pages.

Procedure

  1. From the Security Cloud Control Home page, click Firewall.

  2. In the left pane, click Objects.

  3. Locate the shared network group you want to edit by using object filters and search field.

  4. Click the edit icon in the Actions pane.

    • The Devices field shows the devices the shared network group is present.

    • The Usage field shows the rulesets associated with the shared network group.

    • The Default Values field specifies the default network objects and their values associated with the shared network group that was provided during their creation. Next to this field, you can see the number of devices that contain this default value, and you can click to see their names and device types. You can also see the rulesets associated with this value.

  5. In the Additional Values field, enter a value or name. When you start typing, Security Cloud Control provides object names or values that match your entry.

  6. You can choose one of the existing objects shown or create a new one based on the name or value that you have entered.

  7. If Security Cloud Control finds a match, to choose an existing object, click Add to add the network object or network group to the new network group.

  8. If you have entered a value or object that is not present, you can perform one of the following:

    • Click Add as New Object With This Name to create a new object with that name. Enter a value and click the checkmark to save it.

    • Click Add as New Object to create a new object. The object name and value are the same. Enter a name and click the checkmark to save it.

    It is possible to create a new object even though the value is already present. You can make changes to those objects and save them.

  9. In the Devices column, click the cell associated with the newly added object and click Add Devices.

  10. Select the devices that you want and click OK.

  11. Click Save. Security Cloud Control displays the devices that will be affected by the change.

  12. Click Confirm to finalize the change to the object and any devices affected by it.

  13. Preview and Deploy Configuration Changes for All Devices.


Edit Additional Values in a Shared Network Group

Note

If Cloud-Delivered Firewall Management Center is deployed on your tenant:

Changes you make to the ASA, FDM, and FTD network objects and groups are reflected in the corresponding Cloud-Delivered Firewall Management Center network object or group. In addition, an entry is created in the Devices with Pending Changes page for each On-Premises Firewall Management Center with Discover & Manage Network Objects enabled, from which you can choose and deploy the changes to the On-Premises Firewall Management Center on which you have these objects.

Deleting a network object or group from either page deletes the object or group from both pages.

Procedure

  1. From the Security Cloud Control Home page, click Firewall.

  2. In the left pane, click Objects.

  3. Locate the object having the override you want to edit by using object filters and search field.

  4. Click the edit icon in the Actions pane.

  5. Modify the override value:

    • Click the edit icon to modify the value.

    • Click the cell in the Devices column to assign new devices. You can select an already assigned device and click Remove Overrides to remove overrides on that device.

    • Click arrow in Default Values to push and make it an additional value of the shared network group. All devices associated with the shared network group are automatically assigned to it.

    • Click arrow in Override Values to push and make it as default objects of the shared network group.

    • Click the delete icon next to remove the object from the network group.

  6. Click Save. Security Cloud Control displays the devices that will be affected by the change.

  7. Click Confirm to finalize the change to the object and any devices affected by it.

  8. Preview and Deploy Configuration Changes for All Devices.


Objects Associated with Meraki Devices

About Objects Used with Meraki Devices

The Meraki dashboard utilizes groups of IP addresses, protocols, or port ranges in source and destination fields in outbound access control rules. Once onboarded, Security Cloud Control translates IP address into network objects, and application layer protocol values into either service objects or protocol objects.

A single rule in Security Cloud Control can translate into multiple rules in the dashboard. For example, if you add an ASA protocol group that includes both TCP and UDP protocols to a single access control rule in Security Cloud Control, Security Cloud Control translates the one Security Cloud Control rule into multiple rules in the dashboard: one rule containing a TCP protocol and one rule containing a UDP protocol.

Note that the Meraki dashboard and Security Cloud Control both support CIDR subnet notation. For more information on layer 3 switch interfaces and MX device layout, see the Meraki Knowledge Base.

Which Objects Can You Use With a Meraki Device in Security Cloud Control?

There are no objects in Security Cloud Control that are exclusive to MX devices. Instead, you can create or share FTD, FDM, and ASA objects and associate these objects in rules that are deployed to the device. Because Meraki is not fully compatible with FTD and ASA objects, there may be a few limitations that affect how the MX device uses objects.

Note that if you associate an FTD, FDM, and ASA objects with an MX device, that object becomes shared. Any changes to that object will affect all the devices it is shared with and the devices' configuration status will appear as Not Synced. For additional object states that could affect your objects, see the Related Articles section listed at the bottom of this page.

Meraki does not support objects containing IPv6 addresses or FQDNs.

Object in Security Cloud Control

Compatible with Meraki

Protocol Objects

TCP, UDP, ICMP

Network Objects

yes

Network Groups

yes

Service Objects

yes

ASA Service Groups

no

FTD Service Groups

no

Local Network Objects and Object Groups From the Meraki Cloud

Network objects and object groups provide easier management of firewall rules for Meraki devices. They serve as labels to IP Subnets and FQDN that can be used on access policies such as firewall rules. If there are needs to modify multiple access policies that use the same IP Subnets or FQDN, you only need to modify the network object to have it reflect on all policies. At this time, you must use the Meraki dashboard to create and modify these objects. For more information about what these objects can do for your environment, see Meraki's Network Objects Highlights.

Note

Once a device configuration referencing a Meraki network object or network object group is onboarded or synchronized to the Security Cloud Control UI, these objects are displayed as FTD Network objects.

These objects and object groups are read-only in Security Cloud Control.

What Do Meraki Rules Look Like in Security Cloud Control

You can view the objects from the device's policy page, or you can filter the objects page based on device. From the policy page you can view, edit, and reorder the access control rules. Because Security Cloud Control translates the outbound rules from the Meraki dashboard into access control rules with objects, rules and protocols from the Meraki dashboard may look different. The following table addresses the new names for protocols once the device is onboarded to Security Cloud Control:

Rule or Protocol Header in the Meraki dashboard

Rule or Object Header in Security Cloud Control

Policy

Action

Source IP

Network Object or Network Group

Destination IP

Network Object or Network Group

Source Port

Network Object or Network Group

Destination Port

Network Object or Network Group

Layer 3 Application Protocol

Ports (Protocol Groups, Port Groups, or Service Objects)

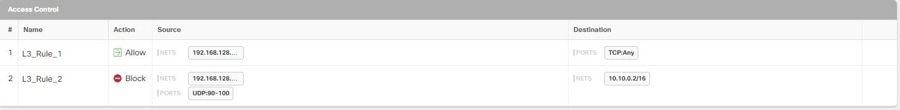
The following is an example of what the outbound rules from the Meraki dashboard look in Security Cloud Control:


Create a Local Meraki Network Object

A local Meraki network object must be made in the Merkai dashboard. If you have a Meraki device that has not been onboarded to Security Cloud Control yet, any pre-existing local objects are onboarded with the device; if you have a Meraki device that has been onboarded, sychronize the device in Security Cloud Control to read the new configuration and local objects.

Note

Once a device configuration referencing a Meraki network object or network object group is onboarded or synchronized with the Security Cloud Control UI, these objects are displayed as FTD Network objects or object groups.

These objects and object groups are read-only in Security Cloud Control.

Before you begin

If you have not enabled Merkai's Open Beta Network Objects, log into the Meraki dashboard and navigate to Organization > Policy Object to enroll and get access to local objects and object groups

Procedure

  1. Log into the Meraki dashboard and create a local object or a local object group. See the Meraki Network Objects Configuration Guide for more information.

  2. Log into Security Cloud Control.

    Note: If you have not yet onboarded your Meraki device to Security Cloud Control, see Onboard an MX device to Security Cloud Control for more information. Onboarding a device also onboards all the pre-existing objects.

  3. In the left pane, click Security Devices.

  4. Locate the Merkai device and select it so the device row is highlighted. The device status is Conflict detected. In the pane located to the right, select either Review Conflict to review the changes made to the device's configuration or Accept without Review to accept all configuration changes.


Create or Edit a Meraki Network Object or Network Group

MX devices use the same format as Firepower and ASA network objects and can contain a host name, an IP address or a subnet address expressed in CIDR notation. Network groups are a collection of network objects and other individual addresses or subnets you add to the group. Network objects and network groups are used in access rules. You can create, read, update, and delete network objects and network groups using Security Cloud Control.

IP addresses that can be added to network objects

Device type

IPv4 / IPv6

Single Address

Range of addresses

Fully Qualified Domain Name

Subnet using CIDR Notation

MX

IPv4

Yes

Yes

No

Yes

Note

If Cloud-Delivered Firewall Management Center is deployed on your tenant:

When you create an FTD, FDM, or ASA network object or group on the Objects page, a copy of the object is automatically added to the Cloud-Delivered Firewall Management Center and vice-versa. In addition, an entry is created in the Devices with Pending Changes page for each On-Premises Firewall Management Center with Discover & Manage Network Objects enabled, from which you can choose and deploy the objects to the On-Premises Firewall Management Center on which you want these objects.

Note

If Cloud-Delivered Firewall Management Center is deployed on your tenant:

Changes you make to the ASA, FDM, and FTD network objects and groups are reflected in the corresponding Cloud-Delivered Firewall Management Center network object or group. In addition, an entry is created in the Devices with Pending Changes page for each On-Premises Firewall Management Center with Discover & Manage Network Objects enabled, from which you can choose and deploy the changes to the On-Premises Firewall Management Center on which you have these objects.

Deleting a network object or group from either page deletes the object or group from both pages.


Create a Meraki Network Object

Note

If Cloud-Delivered Firewall Management Center is deployed on your tenant:

When you create an FTD, FDM, or ASA network object or group on the Objects page, a copy of the object is automatically added to the Cloud-Delivered Firewall Management Center and vice-versa. In addition, an entry is created in the Devices with Pending Changes page for each On-Premises Firewall Management Center with Discover & Manage Network Objects enabled, from which you can choose and deploy the objects to the On-Premises Firewall Management Center on which you want these objects.

Procedure

  1. From the Security Cloud Control Home page, click Firewall.

  2. In the left pane, click Objects.

  3. Click , then click FTD > Network or ASA > Network.

  4. Enter an object name.

  5. Select Create a network object.

  6. In the Value section, enter a single IP address or a subnet address expressed in CIDR notation.

  7. Click Add.

  8. Review and deploy now the changes you made, or wait and deploy multiple changes at once.


Create a Meraki Network Group

A network group is made up of multiple network objects or IP addresses.

If you want your network group to be made up of network objects, use the "Create a Network Object" procedure above to create individual network objects for your IP addresses.

Note

If Cloud-Delivered Firewall Management Center is deployed on your tenant:

When you create an FTD, FDM, or ASA network object or group on the Objects page, a copy of the object is automatically added to the Cloud-Delivered Firewall Management Center and vice-versa. In addition, an entry is created in the Devices with Pending Changes page for each On-Premises Firewall Management Center with Discover & Manage Network Objects enabled, from which you can choose and deploy the objects to the On-Premises Firewall Management Center on which you want these objects.

Procedure

  1. From the Security Cloud Control Home page, click Firewall.

  2. In the Security Cloud Control navigation bar on the left, click Objects.

  3. Click , then click either FTD > Network or ASA > Network.

  4. Enter an object name.

  5. Select Create a network group.

  6. Click Add Object, select the network object from the list and click Select. Continue to do this until you have added all the network objects you want.

  7. Click Add.

  8. Review and deploy now the changes you made, or wait and deploy multiple changes at once.


Edit a Firepower Network Object or Network Group

Note

If Cloud-Delivered Firewall Management Center is deployed on your tenant:

Changes you make to the ASA, FDM, and FTD network objects and groups are reflected in the corresponding Cloud-Delivered Firewall Management Center network object or group. In addition, an entry is created in the Devices with Pending Changes page for each On-Premises Firewall Management Center with Discover & Manage Network Objects enabled, from which you can choose and deploy the changes to the On-Premises Firewall Management Center on which you have these objects.

Deleting a network object or group from either page deletes the object or group from both pages.

Procedure

  1. From the Security Cloud Control Home page, click Firewall.

  2. In the left pane, click Objects.

  3. Locate the object you want to edit by using object filters and search field.

  4. Select the object you want to edit.

  5. Click the edit button in the details pane.

  6. Edit the values in the dialog box in the same fashion that you created them in the procedures above.

  7. Click Save.

  8. Security Cloud Control displays the policies that will be affected by the change. Click Confirm to finalize the change to the object and any policy affected by it.

  9. Review and deploy now the changes you made, or wait and deploy multiple changes at once.