Cisco Security Cloud Control: Secure Firewall Device Management

PDF

Cisco Security Cloud Control: Secure Firewall Device Management

Event logging page search and filter functionality

Want to summarize with AI?

Log in

Describes how to search and filter events using the event logging page functionality.


Event logging page search and filter functionality is a data management feature that

  • enables you to search and filter historical and live event tables for specific events using the same mechanisms as other information in Security Cloud Control,

  • limits what displays on the Event Logging page as you add filter criteria, and

  • allows you to combine filtering and searching mechanisms where search finds values from filtered event results.

Event logging search and filter options

These are the options to conduct a search for event logs:

Filtering works the same way for live events as it does for historical events with the exception that live events cannot be filtered by time.

Learn about these filtering methods:


Filter live or historical events

Filter events to view specific subsets of live or historical events in the Event Logging page, which helps in analyzing security events more effectively.

This procedure explains how to use event filtering to see a subset of events in the Event Logging page. If you find yourself repeatedly using certain filter criteria, you can create a customized filter and save it. See Customizable Event Filters for more information.

Procedure

1.

From the Security Cloud Control Home page, click Firewall.

2.

In the navigation bar, choose Events & Logs > Events > Event Logging

3.

Click either the Historical or Live tab.

4.

Click the filter icon (The image illustrates the process of filtering live or historical events in the FTD Events interface, highlighting key options and features available to users.). Click the pin icon (The FTD Events Connection section illustrates the display of connection events generated by access control rules, highlighting the filtering of live or historical events.) to pin the Filter pane and keep it open.

5.

Click a view tab that has no saved filter elements.

The FTD Events figure illustrates the categorization of connection, file, and intrusion events as reported by access control rules in a network security context.
6.

Select the event details you want to filter by:

  • FTD Events:

    • Connection: Displays connection events from access control rules.

    • File: Displays events reported by file policies in access control rules.

    • Intrusion: Displays events reported by intrusion policy in access control rules.

    • Malware: Displays events reported by malware policies in access control rules.

  • ASA Events: These event types represent groups of syslog or NetFlow events.

    See Security Cloud Control Event Types for more information about events.

  • Time Range: Click the Start or End time fields to select the beginning and end of the time period you want to display. The time stamp is displayed in the local time of your computer.

  • Action: Specifies the security action defined by the rule. The value you enter must be an exact match to what you want to find; however, the case doesn't matter. Enter different values for connection, file, intrusion, malware, syslog, and NetFlow event types:

    • For connection event types, the filter searches for matches in the AC_RuleAction attribute. Those values could be Allow, Block, Trust.

    • For file event types, the filter searches for matches in the FileAction attribute. Those values could be Allow, Block, Trust.

    • For intrusion event types, the filter searches for matches in the InLineResult attribute. Those values could be Allowed, Blocked, Trusted.

    • For malware event types, the filter searches for matches in the FileAction attribute. Those values could be Cloud Lookup Timeout.

    • For syslog and NetFlow events types, the filter searches for matches in the Action attribute.

  • Sensor ID / Hostname: The Sensor ID is the management IP address from which events are sent to the Secure Event Connector or Security Service Exchange.

    For an FDM-managed device, the Sensor ID is typically the IP address of the device's management interface.

  • IP addresses

    • Initiator: This is the IP address of the source of the network traffic. The value of the Initiator address field corresponds to the value of the InitiatorIP field in the event details. You can enter a single address, such as 10.10.10.100, or a network defined in CIDR notation such as 10.10.10.0/24.

    • Responder: This is the destination IP address of the packet. The value of the Destination address field corresponds to the value in the ResponderIP field in the event details. You can enter a single address, such as 10.10.10.100, or a network defined in CIDR notation such as 10.10.10.0/24.

  • Ports

    • Initiator: The port or ICMP type used by the session initiator. The value of the source port corresponds to the value fo the InitiatorPort in the event details. (Add a range - starting port ending port and space in between or both initiator and responder)

    • Reponder: The port or ICMP code used by the session responder. The value of the destination port corresponds to the value of the ResponderPort in the event details.

7.

(Optional) Save your filter as a custom filter by clicking out of the view tab.

The Event Logging page displays only the events that match your selected filter criteria. You can further refine your search by adjusting the filter parameters or save the filter configuration for future use.


Filter for ASA or FDM-Managed Device Syslog Events but not ASA NetFlow Events

This task allows you to isolate syslog events for troubleshooting and analysis by filtering out NetFlow events that may clutter the event view.

This procedure finds only syslog events by ensuring NetFlow events are excluded from both the general filter settings and the ASA Events filter tree.

Procedure

1.

From the Security Cloud Control Home page, click Firewall.

2.

In the left pane, choose Events & Logs > Events > Event Logging.

3.

Click the Filter icon The image illustrates the filter settings used to exclude ASA NetFlow events from syslog events, highlighting the configuration options necessary for this process. and pin the filter open.

4.

Scroll to the bottom of the Filter pane and make sure the Include NetFlow events filter is unchecked.

5.

Scroll back up to the ASA Events filter tree, and make sure the NetFlow box is unchecked.

6.

Select the rest of your ASA or FTD filter criteria.

The event logging interface now displays only ASA or FTD syslog events with NetFlow events excluded from the view.


Combine filter elements

Combine filter elements is a filtering mechanism that

  • follows standard filtering rules where categories are "AND-ed" AND values within categories are "OR-ed"

  • allows combination of filters with custom search criteria

  • applies "OR" logic to device event filters, AND

  • enables filtering by historical events within a time range.

Filter combination behavior

Filtering events generally follows the standard filtering rules in Security Cloud Control: The filtering categories are "AND-ed" AND the values within the categories are "OR-ed." You can also combine the filter with your own search criteria. In the case of event filters; however, the device event filters are also "OR-ed."
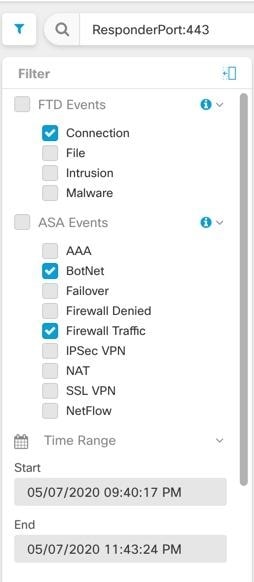
With this filter in use, Security Cloud Control would display Firewall Threat Defense device connection events OR ASA BotNet OR Firewall Traffic events, AND those events that occurred between the two times in the time range, AND those events that also contain the ResponderPort 443. You can filter by historical events within a time range. The live events page always displays the most recent events.

Search for specific attribute: value pairs

You can search for live OR historical events by entering an event attribute AND a value in the search field. The easiest way to do this is to click the attribute in the Event Logging table that you want to search for, AND Security Cloud Control enters it in the Search field. The events you can click on will be blue when you roll over them.
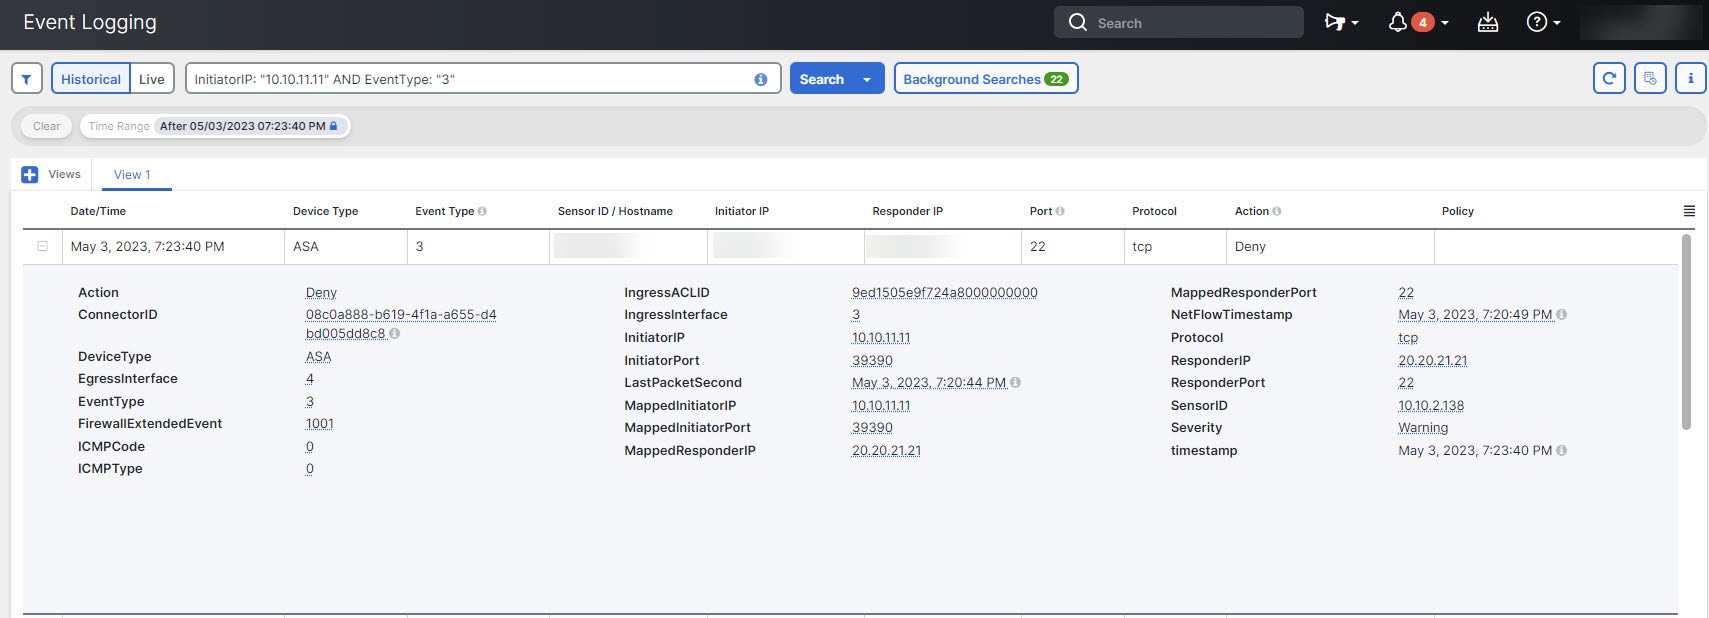
The image illustrates the process of combining filter elements in a search function, showing how to select and add specific attribute-value pairs to refine search results.

In this example, the search started by rolling over the InitiatorIP value of 10.10.11.11 AND clicking it. Initiator IP AND it's value were added to the search string. Next, Event Type, 3 was rolled-over AND clicked AND added to the search string AND an AND was added by Security Cloud Control. So the result of this search will be a list of events that were initiated from 10.10.11.11 AND that are 3 event types.

Notice the magnifying glass next to the value 3 in the example above. If you roll-over the magnifying glass, you could also choose an AND, OR, AND NOT, OR NOT operator to go with the value you want to add to the search.

In the example below, "OR" is chosen. The result of this search will be a list of events that were initiated from 10.10.11.11 OR are a 106023 event type. Note that if the search field is empty AND you right click a value from the table, only NOT is available as there is no other value.
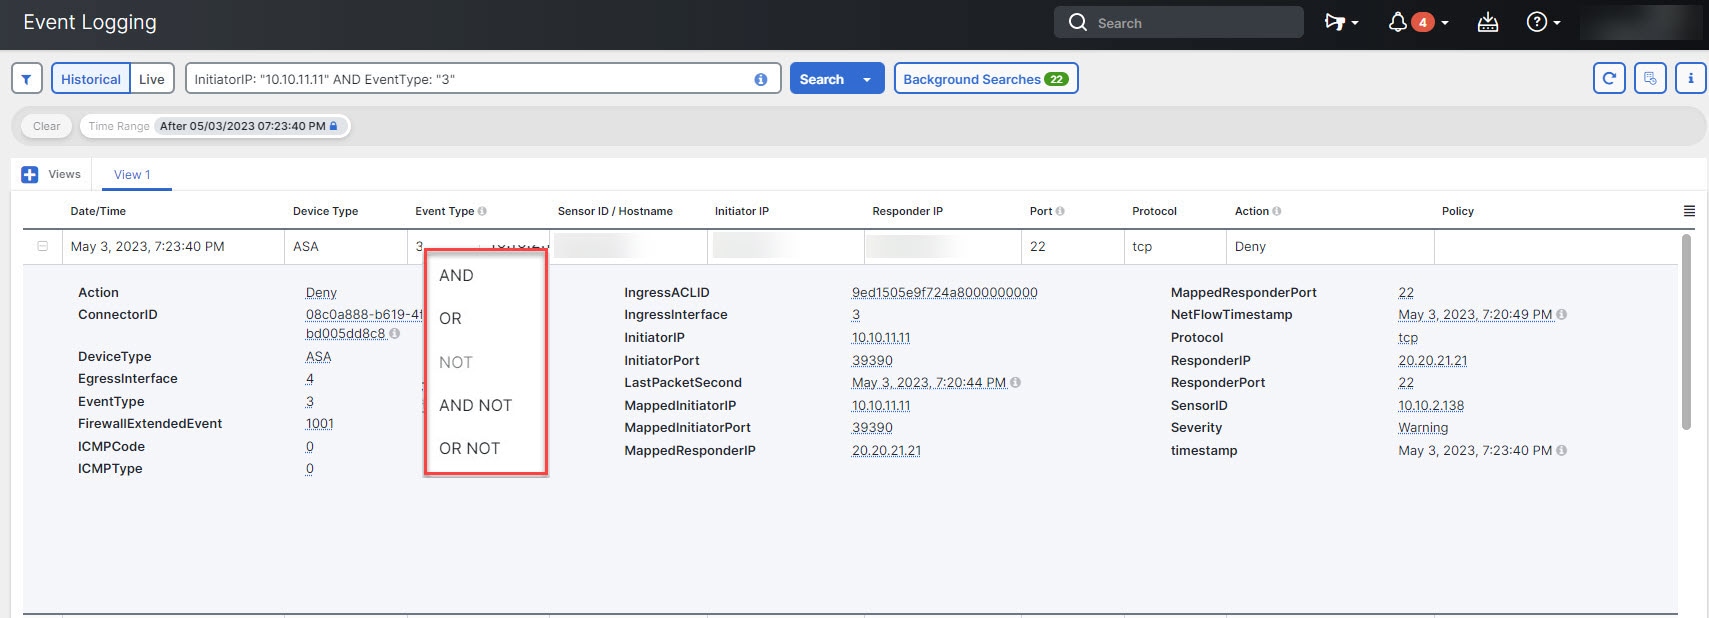
As long as you rollover a value AND it is highlighted blue, you can add that value to the search string.

AND, OR, NOT, AND NOT, OR NOT filter operators behavior:

  • AND: Use the AND operator in the filter string, to find events that include all attributes. The AND operator cannot begin a search string.

  • OR: Use the OR operator in the filter string, to find events that include any of the attributes. The OR operator cannot begin a search string.

  • NOT: Use this only at the beginning of a search string to exclude events with certain attributes.

  • AND NOT: Use the AND NOT operator in the filter string to exclude events that contain certain attributes. AND NOT cannot be used at the beginning of a search string.

  • OR NOT: Use the OR NOT operator to include search results that exclude certain elements. The OR NOT operator cannot be used at the beginning of a search string.

Filter operator examples

AND example:

For example, the search string below will search for events that contain the TCP protocol AND that originated from InitiatorIP address 10.10.10.43, AND that were sent from the Initiator port 59614. One would expect that with each additional AND statement, the number of events that meet the criteria would be small AND smaller.

Protocol: "tcp" AND InitiatorIP: "10.10.10.43" AND InitiatorPort: "59614"

OR example:

For example, the search string below will display events in the event viewer that include events that include the TCP protocol, OR that originated from InitiatorIP address 10.10.10.43, OR that were sent from the Initiator port 59614. One would expect that with each additional OR statement, the number of events that meet the criteria would be bigger AND bigger.

Protocol: "tcp" OR InitiatorIP: "10.10.10.43" OR InitiatorPort: "59614"

NOT example:

For example, this search string would exclude any event with the InitiatorIP 192.168.25.3 from the results.

NOT InitiatorIP: "192.168.25.3"

AND NOT example:

For example, this filter string will display events with the InitiatorIP 192.168.25.3 but NOT those whose ResponderIP address is also 10.10.10.1.

InitiatorIP: "192.168.25.3" AND NOT ResponderIP: "10.10.10.1"

You can also combine NOT AND AND NOT to exclude several attributes. For example this filter string, will exclude events with InitiatorIP 192.168.25.3 AND events with ResponderIP 10.10.10.1

NOT InitiatorIP: "192.168.25.3" AND NOT ResponderIP: "10.10.10.1"

OR NOT example:

For example, this search string will find events with the Protocol of TCP, OR that have the InitiatorIP of 10.10.10.43, OR those NOT from InitiatorPort 59614.

Protocol: "tcp" OR InitiatorIP: "10.10.10.43" OR NOT InitiatorPort: "59614"

You could also think of it this way: Search for (Protocol: "TCP") OR (InitiatorIP: "10.10.10.43") OR (NOT InitiatorPort: "59614").

Wildcard searches:

Use an asterisk (*) to represent a wildcard in the value field of an attribute:value search to find results within events. For example, this filter string,

URL:*feedback*

will find strings in the URL attribute field of events that contain the string feedback.

Related information:


Search events using the events logging page

This task allows you to search all logged events and find the information you need using the search and report capabilities in the Event Logging page.

Use the search and report capabilities in the Event Logging page to search all logged events and find the information you need. Note that you can generate reports only for historical events.

Procedure

1.

From the Security Cloud Control Home page, click Firewall.

2.

In the navigation bar, choose Events & Logs > Events > Event Logging.

3.

Click either the Historical or Live tab.

4.

Type the search query in the search bar and click Search to execute the search.

Alternatively, click the search box to choose from a list of Sample Filters to quickly search for events. Use the sample filters to quickly populate a search query in the search bar and then modify it to match your specific needs. Find more information about using the sample filters in Use sample filters to search events.

5.

(optional)To run a search in the background and generate a report while you move away from the search page, do these steps:

  1. Type your search query and choose Schedule Report from the Search drop-down list.

  2. Click Generate Report.

    The search is queued, and you are notified when it is complete. You can run multiple searches in the background.

    For more information about scheduling a report, refer to Schedule to generate a search report in the background

6.

(Optional) If you want to view and manage your search reports, click Reports.

From this view, you can do these actions:

  • The Reports page allows you to view, download, or delete the search reports.

  • Click Schedule a Report to generate a one-time report or to schedule a recurring report.

  • Click View Notification Settings to navigate to the Notification Preferences page to view or modify your notification settings.

You can convert any one-time report into a recurring report schedule if you need recurring searches. For more information, refer to Schedule to generate a search report in the background.

You have successfully searched for events and can view the results in the Event Logging page. Any scheduled reports will run in the background and notify you when complete.


Use sample filters to search events

Sample filters allow you to construct common search queries quickly without requiring you to type the full query.

You can select a filter and modify the query parameters to fit your specific needs when searching for events.

Procedure

1.

In the Event Logging page, click the search bar.

A list of Sample Filters appears below the search bar.

2.

Choose a filter from the drop-down list.

The search bar automatically populates with the corresponding search query.

3.

Modify the values in the predefined query to refine your search.

Examples

  • To search for events related to a specific website, select Wildcard URL. The search bar displays URL: "*.sharepoint.com". You can then change sharepoint.com to any other domain you wish to investigate.

  • To search for events involving a specific device, select Specific Host. The search bar displays InitiatorIP: "192.168.55.55" OR ResponderIP: "192.168.55.55". Change 192.168.55.55 to the IP address of the device you want to monitor.

4.

Click Search.

The search results display events that match your filter criteria, allowing you to analyze specific network activity OR investigate particular devices OR websites.


Search historical events in the background

A background historical event search is a feature that allows you to define search criteria and search for event logs based on that criteria, with the Reports feature enabling you to perform the event log searches in the background and generate reports.

Background search capabilities

The background search functionality provides these capabilities:

  • You receive a notification when the report generation is complete, based on your configured notification preferences.

  • You can view, download, or delete the reports from the Reports page.

  • You can schedule to generate either a one-time report or a recurring report.

  • Navigate to the Notification Settings page to view or modify the subscription options.


Schedule to generate a search report in the background

Use the Report feature to run one-time or scheduled event log searches in the background and generate reports for analysis and compliance purposes.

You can modify or cancel the scheduled report at any time. You can also modify a one-time search query to be a recurring search.

  • You can schedule to generate reports only for historical events.

  • You can opt to get alerts on reports that have started, completed, or have failed.

Before you begin

Follow these steps to schedule a search and generate report:

Procedure

1.

From the Security Cloud Control Home page, click Firewall.

2.

In the navigation bar, choose Events & Logs > Events > Event Logging.

3.

Click the Historical tab to view historical events.

4.

Type the search query in the search bar.

5.

Click the Search drop-down and choose Schedule Report.

6.

(Optional) Enter a name for the report to identify it.

7.

The Generate report now check box is checked by default. When checked, the report generation starts upon saving.

8.

Check the Setup recurring schedule check box and configure these settings:

  • Search Logs for the Last: Specify how far back you want to search through.

  • Frequency: Specify how frequent you want the scheduled search to occur and the time at which you want it to run.

9.

Confirm the scheduled search criteria at the bottom of the window. Click Schedule and Generate Now. If you did not opt for the search to start immediately, click Schedule Report.

Scheduled search reports are available to view for up to seven days before Security Cloud Control automatically deletes them.

The scheduled search is created and will generate reports according to the specified frequency. If you opted to generate the report immediately, the initial report generation begins upon saving.


Download a search report

Download search results and scheduled queries in CSV format for local storage and analysis before they are automatically removed after seven days.

Search results and schedules queries are stored for seven days before Security Cloud Control automatically removes them. You can download a copy of the search report in CSV format.

Procedure

1.

From the Security Cloud Control Home page, click Firewall.

2.

In the navigation bar, choose Events & Logs > Events > Event Logging.

3.

Click Reports.

4.

In the Actions column, click Download next to the report to download it. The report file in CSV format is automatically downloaded to the default storage location on your local drive.

5.

(Optional) To view the search query and download the report, follow these steps:

  1. click Queries tab.

  2. Expand the report to see the search query details.

  3. Click View Reports next to the report you want to view and download.

  4. Click Download.

The search report is downloaded in CSV format to your local drive's default storage location, allowing you to analyze the data before it is automatically removed from the system.