- Overview
- Getting Started
- Configuring RBAC
- Configuring Primary Authentication
- Configuring Trusted Points
- Configuring VM Managers
- Configuring System Profiles
- Configuring Tenants
- Configuring Service Policies and Profiles
- Configuring Device Policies and Profiles
- Configuring Managed Resources
- Integrating with DCNM
- Configuring Administrative Operations
Getting Started
This section contains the following topics:
Logging Into
The default HTTPS URL for logging into the user interface is https://server-ip-address, where server-ip-address is the IP address assigned to the server. The IP address is the address for the management port.
 Note | If you log in using HTTP, you are automatically redirected to the HTTPS link. |
Configuration Workflow
The following table provides the most common initial and ongoing workflow tasks to configure .
| Initial Configuration Tasks (Administrative) | Description | ||
|---|---|---|---|
|
Configure roles for user access. |
|||
|
Configure LDAP providers and select a primary authentication service. |
|||
|
Configure trusted points for LDAP over SSL. |
|||
|
Configure access with hypervisors. |
|||
|
Configure the default system profile. |
|||
| Ongoing Configuration Tasks | |||
|
Add tenants for resource and service support. |
|||
|
Configure access and security-related policies for access to resources. |
|||
|
Configure device-specific policies and profiles. |
|||
|
Add and configure enterprise and cloud resources.
|
|||
GUI Overview
provides a browser-based interface that enables you to configure managed endpoints, perform administrative operational tasks, and define and apply policies and profiles. You also use the GUI to manage and provision device resources.
- User Interface Components
- Toolbar
- Tables
- Field Aids
- Firewall Access
- Setting the Idle Timeout Period - Preferences
- Search
- Clone
User Interface Components
When you log into , the user interface is displayed.
The user interface contains the components described in the following table:
The following table provides information about the tabs in the GUI:
| Tab | Description |
|---|---|
|
Tenant Management |
Enables you to manage tenants in the current instance. A system or server administrator can use this tab to create organizational hierarchies and enable multi-tenant management domains. The organizational hierarchy levels are Tenant > Virtual Data Center > Application > Tier. |
|
Resource Management |
Enables you to manage logical resources, such as VSGs, ASA 1000Vs, VSGs, and vCenters. |
|
Policy Management |
Enables you to configure service and device policies and profiles, and to assign policies to profiles. |
|
Administration |
Provides the tools needed for administering . |
Toolbar
The toolbar displays in the upper-right portion of the user interface. The following table describes the toolbar options:
| Option | Description |
|---|---|
|
(username) |
Username of the current session. |
|
Preferences |
Enables you to specify the amount of time that the session can remain inactive before the session times out. The value that you specify applies to the system from which you logged into . |
|
Log Out |
Logs you out of the current session. |
|
About |
Provides version information. |
|
Help |
Launches online help for the currently displayed screen. |
|
Feedback |
Allows you to provide feedback on . |
Tables
The tables in the GUI contain the following features:
|
Feature |
Description |
|---|---|
|
Actions drop-down list |
For tables that provide many actions, a drop-down list displays the options. The actions that are available for the selected item appear in normal font, whereas those actions that are not available for the selected item are dimmed. |
|
Filter |
You can filter the table contents by a value that you enter. |
|
Record count |
The number of entries in the table. |
|
Sort by column |
You can sort all table entries by clicking on a column heading. |
|
Table-specific toolbars |
Toolbars are available for most tables, with options that are appropriate for the specific table. |
Field Aids
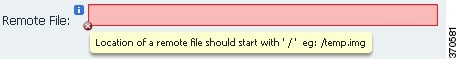
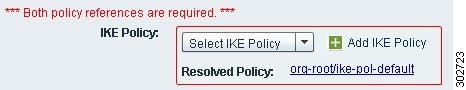
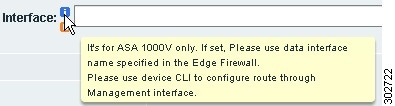
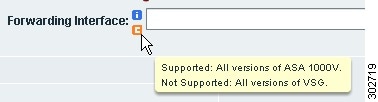
includes the following aids to assist you in your tasks, whether configuring policies and profiles, troubleshooting faults, or looking for additional information for a particular window or dialog box.

Firewall Access
Setting the Idle Timeout Period - Preferences
The Preferences dialog box allows you to specify the length of time, from 5 to 60 minutes, that a session on your current machine can remain idle before the session is closed. The value that you enter applies to the system that you used to log into .
Search
The Search tab enables you to search for instances of organizations in . From the search result, you can expand an organization's hierarchy and launch devices and polices in that organization.
Note | Searching for organization names does not work if the organization names contain special characters. |
1.
Do any of the following to launch the Search tab:
2.
Enter organization names as a *pattern or a regular expression.
3. Click Search.
DETAILED STEPS
Clone
You can create a clone for an organization, policy, policy set, or profile at a destination of your choice. The hierarchy of an organization's clone or the names of the elements in it cannot be changed. After a clone is created, it cannot be renamed or moved to another location.
Note | If you clone a policy set, such as a NAT policy set, the contained policies are not cloned. You must clone policies separately. |
1.
Based on the
element you want to clone, do one of the following:
2. Right-click the element to be cloned and choose Clone.
3. In the Clone dialog box that appears:
DETAILED STEPS
 Feedback
