- Overview
- Getting Started
- Configuring RBAC
- Configuring Primary Authentication
- Configuring Trusted Points
- Configuring VM Managers
- Configuring System Profiles
- Configuring Tenants
- Configuring Service Policies and Profiles
- Configuring Device Policies and Profiles
- Configuring Managed Resources
- Integrating with DCNM
- Configuring Administrative Operations
- Device Policies and Profiles
- Device Configuration
- Device Policies
- Configuring Device Policies
Configuring Device Policies and Profiles
This section includes the following topics:
- Device Policies and Profiles
- Device Configuration
- Device Policies
- Configuring Device Policies
- Configuring Device Profiles
- Configuring NTP
- Associating Device Policies with Profiles
Device Policies and Profiles
enables you to create device profiles and policies at any organizational level.
Device Profiles
A device profile is a set of custom security attributes and device policies. For Nexus 1000V VSMs, the device profile is added to the port profile. The port profile is assigned to the Nexus 1000V VSM vNIC, making the device profile part of the virtual machine (VM). Adding a device profile to the VM allows the addition of custom attributes to the VM. Firewall rules can be written using custom attributes such that traffic between VMs can be allowed to pass or be dropped.
You apply device profiles by choosing Resource Management > Managed Resources and then navigating to the required device at the root or tenant level. The Firewall Settings area of the firewall pane includes the Device Profile option.
includes a default device profile at root level. The default device profile can be edited but cannot be deleted.
Policies
supports the following objects related to policies:
- Policy set—Contains policies. After a policy set is created, it can be assigned to a profile. An existing default policy set is automatically assigned at system boot up.
Policy—Contains rules that can be ordered. An existing default policy is automatically assigned at system boot up. The default policy contains a rule with an action of drop.
Rule—Contains conditions for regulating traffic. The default policy contains a rule with an action of drop. Conditions for a rule can be set using the network, custom, and virtual machine attributes.
Object group—Can be created under an organization node. An object group defines a collection of condition expressions on a system-defined or user-defined attribute. An object group can be referred to in a policy rule condition when the member or not-member operator is selected. A rule condition that refers to an object group resolves to true if any of the expressions in the object group are true.
Security Profile Dictionary—Logical collection of security attributes. You define dictionary attributes for use in a security profile. A security profile dictionary is created at the root or tenant node. You can create only one dictionary for a tenant and one for root. The security profile dictionary allows the user to define names of custom attributes. Custom attribute values are specified on security profile objects. Custom attributes can be used to define policy rule conditions. Attributes configured in a root level dictionary can be used by any tenant. You cannot create a dictionary below the tenant level.
Zone—Set of VMs based on conditions. The zone name is used in the authoring rules.
Security policies are created and then pushed to the Cisco VSG or ASA 1000V.
Device Configuration
enables you to configure devices by adding policies to a device profile and then applying that profile to a device. To create a root device profile, choose and click Add Device Profile. Device profiles contain options for the following policies and settings:
Device Policies
provides default polices for fault, logging, SNMP, and syslog. The default policies cannot be deleted but can be modified. A device profile uses name resolution to resolve policy assignments. For details, see Name Resolution in a Multi-Tenant Environment.
Policies created under root are visible to both the profile and the Device profile.
Configuring Device Policies
- Configuring AAA Policies
- Configuring Core File Policies
- Configuring Fault Policies
- Configuring Log File Policies
- Configuring SNMP Policies
- Configuring Syslog Policies
Configuring AAA Policies
Authentication, authorization, and accounting (AAA) policies verify users before they are allowed access to a network and network services. By creating AAA policies in and associating the policies with objects through device profiles, you can ensure that only authenticated users can access the objects.
 Note | Edge Firewall supports only Remote Access Method under Authentication Policy. Compute Firewall supports all the AAA policies. |
supports authentication and authorization for edge firewalls, compute firewalls, and server groups using the following protocols:
Note | Cisco VSG Release 5.2(1)VSG2(2.0) and later releases support AAA with RADIUS and TACACS+ protocols. |
You can use to configure an AAA policy on ASA 1000V. does not support AAA policies on VSG, VPX, or CSR 1000V.
1. Choose .
2. In the General tab, click Add Authentication Policy.
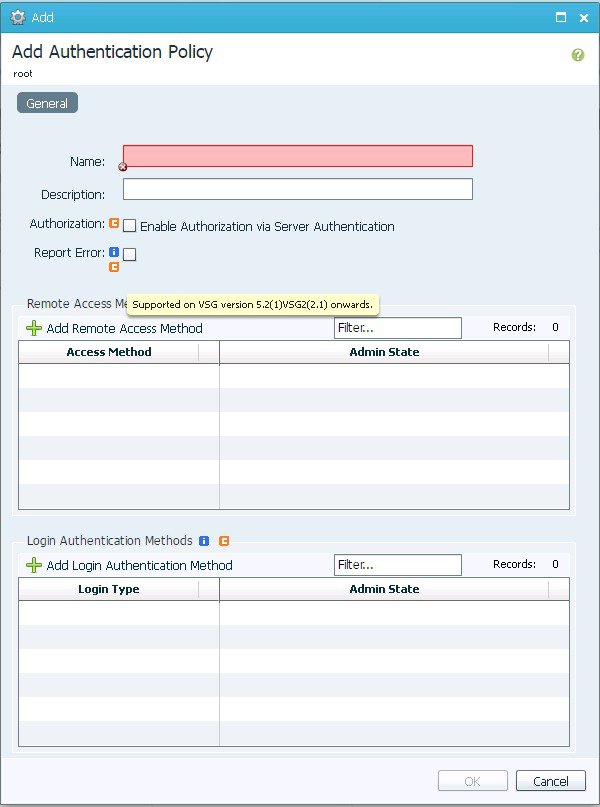
3. In the Add Authentication Policy dialog box, enter the information as described in Add Authentication Policy Dialog Box, then click OK.
DETAILED STEPS
| Step 1 | Choose . | ||
| Step 2 | In the General tab, click Add Authentication Policy. | ||
| Step 3 | In the Add
Authentication Policy dialog box, enter the information as described in
Add Authentication Policy Dialog Box,
then click
OK.
|
Field Descriptions
Add Authentication Policy Dialog Box
| Field | Description | ||
|---|---|---|---|
|
Name |
Policy name. |
||
|
Description |
Brief policy description. |
||
|
Authorization |
Check the Enable check box to enable authorization via server authentication.
|
||
|
Remote Access Methods |
|||
|
Add Remote Access Method |
Adds a remote access method to the policy. For more information, see Remote Access Method Dialog Box. |
||
|
Access Method |
One of the following access methods:
|
||
|
Admin State |
Whether the administrative state of the policy is enabled or disabled. |
||
|
Login Authentication Method |
|||
|
Add Login Authentication Method |
Adds a login method to the policy. |
||
|
Login Type |
|
||
|
Admin State |
Whether the administrative state of the policy is enabled or disabled. |
||
Remote Access Method Dialog Box
Login Authentication Method Dialog Box
Note | Supported by Compute Firewall in Cisco VSG Release 5.2.(1)VSG2(2.0) and later releases. |
| Field | Description | ||
|---|---|---|---|
|
Login Type |
|
||
|
Admin State |
Whether the administrative state of the access method is enabled or disabled. |
||
|
Server Group |
Select the server groups in "Available" Group and with the arrows buttons move them to "Assigned" Group.
|
Configuring Authorization Policies
Note | Supported by Compute Firewall in Cisco VSG Release 5.2.(1)VSG2(2.x) onwards. |
1. Choose .
2. In the General tab, click Add Authorization Policy.
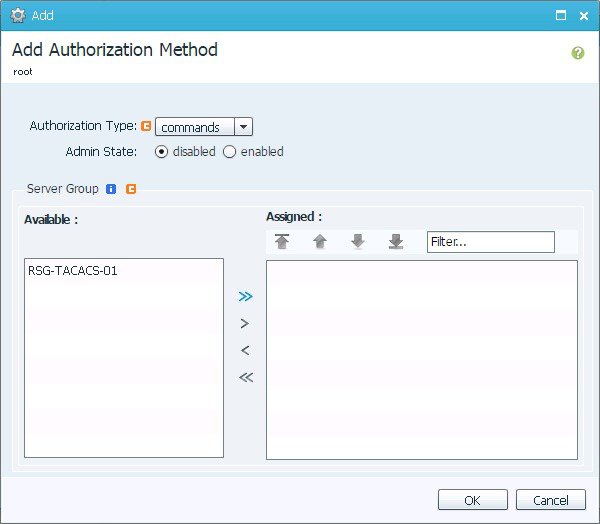
3. In the Add Authorization Policy dialog box, enter the information as described in following table, then click OK.
DETAILED STEPS
| Step 1 | Choose . | ||
| Step 2 | In the General tab, click Add Authorization Policy. | ||
| Step 3 | In the Add
Authorization Policy dialog box, enter the information as described in
following table, then click
OK.
|
Add Authorization Policy Dialog Box
| Field | Description |
|---|---|
|
Name |
Policy name. |
|
Description |
A brief policy description. |
|
Authorization Type |
|
|
Admin State |
Whether the administrative state of the policy is enabled or disabled. |
Authorization Method Dialog Box
| Field | Description | ||
|---|---|---|---|
|
Authorization Type |
|
||
|
Admin State |
Whether the administrative state of the access method is enabled or disabled. |
||
|
Server Group |
Select the server groups in "Available" Group and with the arrows buttons move them to "Assigned" Group.
|
Configuring Accounting Policy
Note | Supported only by Compute Firewall in Cisco VSG Release 5.2.(1)VSG2(2.x) and later releases. |
1. Choose .
2. In the General tab, click Add Accounting Policy.
3. In the Add Accounting Policy dialog box, enter the information as described in following table, then click OK.
DETAILED STEPS
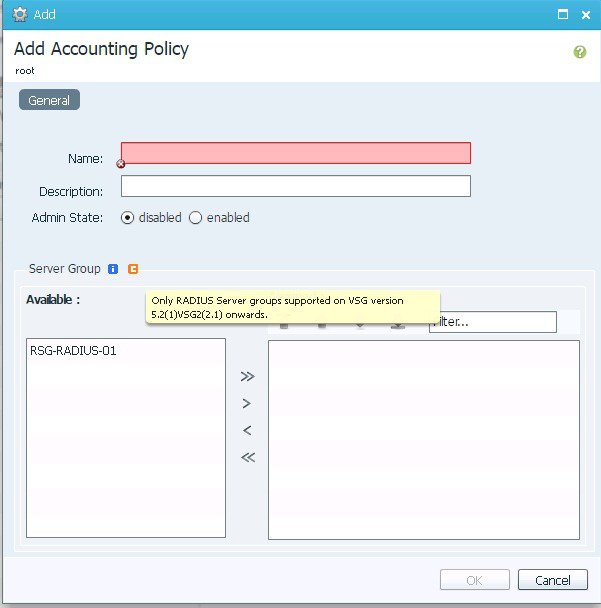
Add Accounting Policy Dialog Box
| Field | Description | ||
|---|---|---|---|
|
Name |
Policy name. |
||
|
Description |
A brief policy description. |
||
|
Admin State |
Whether the administrative state of the policy is enabled or disabled. |
||
|
Server Group |
Select the server groups in "Available" Group and with the arrows buttons move them to "Assigned" Group.
|
Configuring Global Server Timers
Note | Supported only by Compute Firewall in Cisco VSG Release 5.2.(1)VSG2(2.x) and later releases. |
1. Choose .
2. In the General tab, click Global Server Timers.
3. In the Add Global Server Timers dialog box, enter the information as described in following table, then click OK.
DETAILED STEPS
Add Global Server Timers Dialog Box
| Field | Description |
|---|---|
|
Name |
Name of the Global Server Timer. |
|
Description |
A brief description of the timer. |
|
Admin State |
Whether the administrative state of the policy is enabled or disabled. |
|
Dead Time |
Duration for which non-reachable server is skipped. |
|
Timeout |
Server timeout period. |
|
Retransmit Count |
Retry count for server request. |
|
Global Server Monitoring Parameters |
|
|
Idle Time |
Time interval for monitoring the server. |
|
User Name |
Username in test packets for server monitoring only. |
|
Password |
Password for the User. |
Configuring Core File Policies
Adding a Core File Policy for a Device
You can add a core file policy at any organizational level.
1. Choose Policy Management > Device Configurations > root > Policies > Core File.
2. In the General tab, click Add Core File Policy.
3. In the Add Core File Policy dialog box, add the information as described in the following table, then click OK:
DETAILED STEPS
| Step 1 | Choose Policy Management > Device Configurations > root > Policies > Core File. | ||||||||||||||||
| Step 2 | In the General tab, click Add Core File Policy. | ||||||||||||||||
| Step 3 | In the Add Core File Policy dialog box, add the information as described in the following table, then click OK:
|
Editing a Core File Policy for a Device Profile
1. Choose .
2. In the General tab, select the core file policy you want to edit, then click Edit.
3. In the Edit Core File Policy dialog box, edit the fields as required, using the information in the following table, then click OK.
DETAILED STEPS
| Step 1 | Choose . | ||||||||||||||||
| Step 2 | In the General tab, select the core file policy you want to edit, then click Edit. | ||||||||||||||||
| Step 3 | In the Edit Core File Policy dialog box, edit the fields as required, using the information in the following table, then click OK.
|
Deleting a Core File Policy from a Device Profile
1. Choose Policy Management > Device Configurations > root > Policies > Core File.
2. In the General tab, select the core file policy you want to delete, then click Delete.
3. When prompted, confirm the deletion.
DETAILED STEPS
Configuring Fault Policies
Adding a Fault Policy for a Device Profile
You can add a fault policy at any organizational level.
1. Choose .
2. In the General tab, click Add Fault Policy.
3. In the Add Fault Policy dialog box, enter the information as described in the following table, then click OK.
DETAILED STEPS
| Step 1 | Choose . | ||||||||||||
| Step 2 | In the General tab, click Add Fault Policy. | ||||||||||||
| Step 3 | In the Add Fault Policy dialog box, enter the information as described in the following table, then click OK.
|
Editing a Fault Policy for a Device Profile
Note | When the system boots up, a default policy already exists. You can modify the default policy, but you cannot delete it. |
1. Choose Policy Management > Device Configurations > root > Policies > Fault.
2. In the General tab, select the fault policy you want to edit, then click Edit.
3. In the Edit Fault Policy dialog box, modify the following fields as required, then click OK.
DETAILED STEPS
| Step 1 | Choose Policy Management > Device Configurations > root > Policies > Fault. | ||||||||||||
| Step 2 | In the General tab, select the fault policy you want to edit, then click Edit. | ||||||||||||
| Step 3 | In the Edit Fault Policy dialog box, modify the following fields as required, then click OK.
|
Deleting a Fault Policy for a Device Profile
Note | When the system boots up, a default policy already exists. You can modify the default policy, but you cannot delete it. |
1. Choose Policy Management > Device Configurations > root > Policies > Fault.
2. In the General tab, select the fault policy that you want to delete, then click Delete.
3. When prompted, confirm the deletion.
DETAILED STEPS
Configuring Log File Policies
Adding a Logging Policy for a Device Profile
You can add a logging policy for a device at any organizational level.
1. Choose Policy Management > Device Configurations > root > Policies > Log File.
2. In the General tab, click Add Logging Policy.
3. In the Add Logging Policy dialog box, complete the following fields, then click OK.
DETAILED STEPS
| Step 1 | Choose Policy Management > Device Configurations > root > Policies > Log File. | ||||||||||||
| Step 2 | In the General tab, click Add Logging Policy. | ||||||||||||
| Step 3 | In the Add Logging Policy dialog box, complete the following fields, then click OK.
|
Editing a Logging Policy for a Device Profile
Note | When the system boots up, a default policy already exists. You can modify the default policy, but you cannot delete it. |
1. Choose Policy Management > Device Configurations > root > Policies > Log File.
2. In the General tab, select the log file policy that you want to edit, then click Edit.
3. In the Edit Log File Policy dialog box, edit the fields as required by using the information in the following table, then click OK.
DETAILED STEPS
| Step 1 | Choose Policy Management > Device Configurations > root > Policies > Log File. | ||||||||||||
| Step 2 | In the General tab, select the log file policy that you want to edit, then click Edit. | ||||||||||||
| Step 3 | In the Edit Log File Policy dialog box, edit the fields as required by using the information in the following table, then click OK.
|
Deleting a Logging Policy for a Device Profile
Note | When the system boots up, a default policy already exists. You can modify the default policy, but you cannot delete it. |
1. Choose Policy Management > Device Configurations > root > Policies > Log File.
2. In the General tab, select the logging policy you want to delete, then click Delete.
3. When prompted, confirm the deletion.
DETAILED STEPS
Configuring SNMP Policies
Adding an SNMP Policy
You can add an SNMP policy at any organizational level.
1. Choose .
2. In the General tab, click Add SNMP Policy.
3. In the Add SNMP dialog box, complete the following fields as appropriate:
4. Click the Configuration tab, then complete the following steps:
5. In the Add SNMP dialog box, click OK.
DETAILED STEPS
| Step 1 | Choose . | ||||||||||||||
| Step 2 | In the General tab, click Add SNMP Policy. | ||||||||||||||
| Step 3 | In the Add SNMP
dialog box, complete the following fields as appropriate:
| ||||||||||||||
| Step 4 | Click the
Configuration tab, then complete the following
steps:
| ||||||||||||||
| Step 5 | In the Add SNMP dialog box, click OK. |
Editing an SNMP Policy
Note | When the system boots up, a default policy already exists. You can modify the default policy, but you cannot delete it. |
1. Choose Policy Management > Device Configurations > root > Policies > SNMP.
2. In the General tab, select the SNMP policy that you want to edit, then click Edit.
3. In the Edit SNMP Policy dialog box, edit the information in the General tab as required, using the information in the following table:
4. In the Configuration tab, edit the information as required:
5. In the Traps tab, edit the information as required:
6. Click OK.
DETAILED STEPS
| Step 1 | Choose Policy Management > Device Configurations > root > Policies > SNMP. | ||||||||||||||||
| Step 2 | In the General tab, select the SNMP policy that you want to edit, then click Edit. | ||||||||||||||||
| Step 3 | In the
Edit SNMP Policy dialog box, edit the
information in the General tab as required, using the information in the
following table:
| ||||||||||||||||
| Step 4 | In the
Configuration tab, edit the information as
required:
| ||||||||||||||||
| Step 5 | In the Traps
tab, edit the information as required:
| ||||||||||||||||
| Step 6 | Click OK. |
Deleting an SNMP Policy
Note | When the system boots up, a default policy already exists. You can modify the default policy, but you cannot delete it. |
1. Choose Policy Management > Device Configurations > root > Policies > SNMP.
2. In the General tab, select the SNMP policy that you want to delete, then click Delete.
3. When prompted, confirm the deletion.
DETAILED STEPS
Adding an SNMP Trap Receiver
1. Choose .
2. In the General tab, click .
3. In the Add SNMP Trap dialog box, enter the following information, then click OK:
DETAILED STEPS
| Step 1 | Choose . | ||||||||
| Step 2 | In the General tab, click . | ||||||||
| Step 3 | In the Add SNMP Trap dialog box, enter the following information, then click OK:
|
Editing an SNMP Trap Receiver
1. Choose Policy Management > Device Configurations > root > Policies > SNMP.
2. In the General tab, select the SNMP policy with the SNMP trap that you want to edit, then click Edit.
3. In the Edit SNMP Policy dialog box, click the Traps tab.
4. In the Traps tab, select the entry that you want to edit, then click Edit.
5. In the Edit SNMP Trap dialog box, edit the information in the General tab as required, using the following information:
6. Click OK in the open dialog boxes.
DETAILED STEPS
| Step 1 | Choose Policy Management > Device Configurations > root > Policies > SNMP. | ||||||||
| Step 2 | In the General tab, select the SNMP policy with the SNMP trap that you want to edit, then click Edit. | ||||||||
| Step 3 | In the Edit SNMP Policy dialog box, click the Traps tab. | ||||||||
| Step 4 | In the Traps tab, select the entry that you want to edit, then click Edit. | ||||||||
| Step 5 | In the Edit SNMP Trap dialog box, edit the information in the General tab as required, using the following information:
| ||||||||
| Step 6 | Click OK in the open dialog boxes. |
Deleting an SNMP Trap Receiver
1. Choose Policy Management > Device Configurations > root > Policies > SNMP.
2. In the General tab, select the SNMP policy with the SNMP trap that you want to delete, then click Edit.
3. In the Edit SNMP Policy dialog box, click the Traps tab.
4. In the Traps tab, select the entry that you want to delete, then click Delete.
5. When prompted, confirm the deletion.
DETAILED STEPS
| Step 1 | Choose Policy Management > Device Configurations > root > Policies > SNMP. |
| Step 2 | In the General tab, select the SNMP policy with the SNMP trap that you want to delete, then click Edit. |
| Step 3 | In the Edit SNMP Policy dialog box, click the Traps tab. |
| Step 4 | In the Traps tab, select the entry that you want to delete, then click Delete. |
| Step 5 | When prompted, confirm the deletion. |
Configuring Syslog Policies
Adding a Syslog Policy for a Device
enables you to configure syslog policies for syslog messages and then attach a created syslog policy to a device profile for implementation on all devices using that profile.
You can create syslog policies for logging syslog messages to a remote syslog server or to a local buffer for later review.
1. Choose Policy Management > Device Configurations > root > Policies > Syslog.
2. In the General tab, click Add Syslog Policy.
3. In the Add Syslog dialog box, provide the information as described in Add Syslog Policy Dialog Box, then click OK.
DETAILED STEPS
| Step 1 | Choose Policy Management > Device Configurations > root > Policies > Syslog. |
| Step 2 | In the General tab, click Add Syslog Policy. |
| Step 3 | In the Add Syslog dialog box, provide the information as described in Add Syslog Policy Dialog Box, then click OK. |
Field Descriptions
Add Syslog Policy Dialog Box
| Field | Description |
|---|---|
|
General Tab |
|
|
Name |
Policy name. |
|
Description |
Brief policy description. |
|
Use Emblem Format |
Check the check box to use the EMBLEM format for syslog messages. This option appears only on supported devices. |
|
Continue if Host is Down |
Check the check box to continue logging if the syslog server is down. This option only appears on supported devices. |
|
Servers Tab |
|
|
Add Syslog Server |
Click to add a new syslog server. |
|
Syslog Servers table |
List of configured syslog servers. |
|
Local Destinations Tab |
|
|
Console |
|
|
Monitor |
|
|
File |
|
|
Buffer |
|
|
Time Stamp |
Check the check box for each of the following options that you want to enable for timestamp display: |
Editing a Syslog Policy for a Device Profile
1. Choose .
2. In the General tab, select the policy you want to edit, then click Edit.
3. In the Edit Syslog Policy dialog box, in the General tab, edit the information as required, using the following information:
4. In the Servers tab, click Add Syslog Server to add a new syslog server, or select an existing server and click Edit to edit it.
5. In the Local Destinations tab, edit the information as required, using the following information:
6. Click OK.
DETAILED STEPS
| Step 1 | Choose . | ||||||||||||
| Step 2 | In the General tab, select the policy you want to edit, then click Edit. | ||||||||||||
| Step 3 | In the Edit Syslog Policy dialog box, in the General tab, edit the information as required, using the following information:
| ||||||||||||
| Step 4 | In the Servers tab, click Add Syslog Server to add a new syslog server, or select an existing server and click Edit to edit it. | ||||||||||||
| Step 5 | In the Local Destinations tab, edit the information as required, using the following information:
| ||||||||||||
| Step 6 | Click OK. |
Deleting a Syslog Policy for a Device Profile
Note | When the system boots up, a default policy already exists. You can modify the default policy, but you cannot delete it. |
1. Choose Policy Management > Device Configurations > root > Policies > Syslog.
2. In the General tab, select the syslog policy that you want to delete, then click Delete.
3. When prompted, confirm the deletion.
DETAILED STEPS
Adding a Syslog Server for a Device Profile
1. Choose Policy Management > Device Configurations > root > Policies > Syslog.
2. In the General tab, click Add Syslog Policy.
3. In the Add Syslog Policy dialog box, click the Servers tab, then click Add Syslog Server.
4. In the Add Syslog Server dialog box, provide the information as described in Add Syslog Server Dialog Box, then click OK in the open dialog boxes.
DETAILED STEPS
| Step 1 | Choose Policy Management > Device Configurations > root > Policies > Syslog. |
| Step 2 | In the General tab, click Add Syslog Policy. |
| Step 3 | In the Add Syslog Policy dialog box, click the Servers tab, then click Add Syslog Server. |
| Step 4 | In the Add Syslog Server dialog box, provide the information as described in Add Syslog Server Dialog Box, then click OK in the open dialog boxes. |
Field Descriptions
Add Syslog Server Dialog Box
| Field | Description |
|---|---|
|
Server Type |
One of the following server types: |
|
Hostname/IP Address |
Hostname or IP address where the syslog file resides. If you use a hostname, you must configure a DNS server. |
|
Severity |
One of the following severity levels: |
|
Forwarding Facility |
One of the following forwarding facilities: |
|
Admin State |
Administrative state of the server: disabled or enabled. |
|
Port |
Port to use to send data to the syslog server. The default port selection is 514 for UDP. |
|
Protocol |
Protocol to use: TCP or UDP (default). |
|
Use Transport Layer Security |
Check the check box to use Transport Layer Security. This option is available only for TCP. |
|
Server Interface |
Interface to use to access the syslog server. |
Editing a Syslog Server for a Device Profile
1. Choose Policy Management > Device Configurations > root > Policies > Syslog.
2. In the General tab, select the required syslog policy, then choose Edit.
3. In the Edit Syslog Policy dialog box, from the Servers tab, select the syslog server you want to edit, then click Edit
4. In the Edit Syslog Server dialog box, edit the fields as required, using the information in the following table.
5. Click OK in the open dialog boxes to save your changes.
DETAILED STEPS
| Step 1 | Choose Policy Management > Device Configurations > root > Policies > Syslog. | ||||||||||||||||||||
| Step 2 | In the General tab, select the required syslog policy, then choose Edit. | ||||||||||||||||||||
| Step 3 | In the Edit Syslog Policy dialog box, from the Servers tab, select the syslog server you want to edit, then click Edit | ||||||||||||||||||||
| Step 4 | In the Edit Syslog Server dialog box, edit the fields as required, using the information in the following table.
| ||||||||||||||||||||
| Step 5 | Click OK in the open dialog boxes to save your changes. |
Deleting a Syslog Server for a Device Profile
1. Choose Policy Management > Device Configurations > root > Policies > Syslog.
2. In the General tab, select the syslog policy with the server you want to delete, then click Edit.
3. In the Edit Syslog Policy dialog box, click the Servers tab.
4. In the Servers tab, select the syslog server that you want to delete, then click Delete.
5. When prompted, confirm the deletion.
6. Click OK to save the policy.
DETAILED STEPS
| Step 1 | Choose Policy Management > Device Configurations > root > Policies > Syslog. |
| Step 2 | In the General tab, select the syslog policy with the server you want to delete, then click Edit. |
| Step 3 | In the Edit Syslog Policy dialog box, click the Servers tab. |
| Step 4 | In the Servers tab, select the syslog server that you want to delete, then click Delete. |
| Step 5 | When prompted, confirm the deletion. |
| Step 6 | Click OK to save the policy. |
Configuring Device Profiles
Adding a Firewall Device Profile
1. Choose .
2. In the General tab, click Add Device Profile.
3. In the New Device Profile dialog box, enter the required information in the General and Policies tabs, then click OK:
DETAILED STEPS
| Step 1 | Choose . | ||||||||||||||||||||||
| Step 2 | In the General tab, click Add Device Profile. | ||||||||||||||||||||||
| Step 3 | In the New Device Profile dialog box, enter the required information in the General and Policies tabs, then click OK:
|
Editing a Firewall Device Profile
After you create a firewall device profile, you can edit it as needed.
1. Choose .
2. In the Device Profiles pane, select the profile you want to edit, then click Edit.
3. In the Edit Firewall Device Policy dialog box, update the information in the General tab as described in the following table:
4. In the Policies tab, update the information as described in the following table, then click OK:
DETAILED STEPS
| Step 1 | Choose . | ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
| Step 2 | In the Device Profiles pane, select the profile you want to edit, then click Edit. | ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
| Step 3 | In the Edit
Firewall Device Policy dialog box, update the information in the General tab as
described in the following table:
| ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
| Step 4 | In the Policies
tab, update the information as described in the following table, then click
OK:
| ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
Deleting a Firewall Device Profile
1. Choose .
2. In the Work pane, click the device profile you want to delete.
3. Click Delete.
4. In the Confirm dialog box, click OK.
DETAILED STEPS
Configuring NTP
Network Time Protocol (NTP) is a networking protocol used to synchronize the time on a network of machines. An NTP network usually gets its time from an authoritative time source, such as a radio clock or an atomic clock attached to a time server.
enables you to configure NTP for compute firewalls, edge firewalls, and itself.
The following topics describe how to perform these steps.
For information on configuring NTP on , see Adding an NTP Server.
- Creating a Device Profile with NTP
- Applying Device Profiles to Compute Firewalls
- Applying Device Profiles to Edge Firewalls
Creating a Device Profile with NTP
This procedure describes how to create a device profile with NTP that you can apply to an edge or compute firewall.
1. Choose Policy Management > Device Configurations > root > Device Profiles.
2. In the General tab, click Add Device Profile.
3. In the New Device Profile dialog box, provide the following information:
4. Click the Policies tab.
5. In the NTP servers area, click Add NTP Server.
6. In the Add NTP Server dialog box, enter the information as described in Add NTP Server Dialog Box, then click OK.
7. Click OK.
DETAILED STEPS
| Step 1 | Choose Policy Management > Device Configurations > root > Device Profiles. |
| Step 2 | In the General tab, click Add Device Profile. |
| Step 3 | In the New Device Profile dialog box, provide the following information: |
| Step 4 | Click the Policies tab. |
| Step 5 | In the NTP servers area, click Add NTP Server. |
| Step 6 | In the Add NTP Server dialog box, enter the information as described in Add NTP Server Dialog Box, then click OK. |
| Step 7 | Click OK. |
What to Do Next
After you have configured the device profile, you can apply it to a firewall as described in the following topics:
Field Descriptions
Add NTP Server Dialog Box
Add NTP Server Dialog Box
| Field | Description | ||
|---|---|---|---|
|
Hostname/IP Address |
NTP server name or IP address. For and VSGs, you can enter either a hostname or IP address. For ASA 1000Vs, you must enter an IP address.
|
||
|
Interface Name |
(Policy Management Device Profiles only) Device interface to reach the NTP server. Only ASA 1000Vs support interface names. |
||
|
Authentication Key |
(Policy Management Device Profiles only) Authentication key to access the NTP server. Only ASA 1000Vs support authentication keys. |
Applying Device Profiles to Compute Firewalls
After you have created a device profile, you can apply the profile to a compute firewall.
Note | Starting with Cisco VSG Release 5.2.(1)VSG2(2.0), ensure that at least one NTP server is defined in Device Profile for Compute firewall. |
1. Choose Resource Management > Managed Resources > root > tenant > Compute Firewalls > compute-firewall.
2. In the General tab, click Select in the Device Profile field.
3. In the Select Device Profile dialog box, select the desired profile, then click OK.
4. Click Save.
DETAILED STEPS
Applying Device Profiles to Edge Firewalls
After you have created a device profile, you can apply the profile to an edge firewall.
1. Choose Resource Management > Managed Resources > root > tenant > Edge Firewalls > edge-firewall.
2. In the General tab, click Select in the Device Profile field.
3. In the Select Device Profile dialog box, select the desired profile, then click OK.
4. Click Save.
DETAILED STEPS
Associating Device Policies with Profiles
After you create a device policy, you can associate it with a device profile. By doing so, you can ensure that all devices associated with the device profile use the same policy.
1. Choose Policy Management > Device Configurations > root > Device Profiles > profile where profile is the device profile that you want to add the device policy to.
2. Click the Policies tab.
3. In the Policies tab, locate the drop-down list for the type of policy you want to associate, such as Syslog or Auth Policy.
4. From the drop-down list, choose the policy to add to the profile, then click Save.
DETAILED STEPS
| Step 1 | Choose Policy Management > Device Configurations > root > Device Profiles > profile where profile is the device profile that you want to add the device policy to. |
| Step 2 | Click the Policies tab. |
| Step 3 | In the Policies tab, locate the drop-down list for the type of policy you want to associate, such as Syslog or Auth Policy. |
| Step 4 | From the drop-down list, choose the policy to add to the profile, then click Save. The policy is automatically applied to all devices using the selected profile. |
 Feedback
