Cisco APIC Layer 3 Networking Configuration Guide, Release 6.2(x)

PDF

Cisco APIC Layer 3 Networking Configuration Guide, Release 6.2(x)

BGP Domain-Path feature for loop prevention

Want to summarize with AI?

Log in

Describes a BGP mechanism that prevents routing loops by tracking routing domains traversed by routes and blocking routes that would create loops.


A BGP Domain-Path feature for loop prevention is a routing mechanism that

  • keeps track of the distinct routing domains traversed by a route within the same VPN or extended VRFs, AS well AS across different VPNs or VRFs

  • detects when a route loops back to a VRF in a domain where it has already traversed, and

  • prevents the route from getting imported or accepted when it would lead to a loop.

BGP routing loop scenarios

BGP routing loops might occur in certain situations due to various conditions:

  • Intentional disabling of existing BGP loop prevention mechanisms, such AS AS Path checks

  • Route leaks across different VRFs or VPNs

This is an example scenario where a BGP routing loop might occur:

  1. A prefix P1 received from a BGP IP L3Out peer is advertised in the ACI fabric using the Multiprotocol Border Gateway Protocol (MP-BGP).
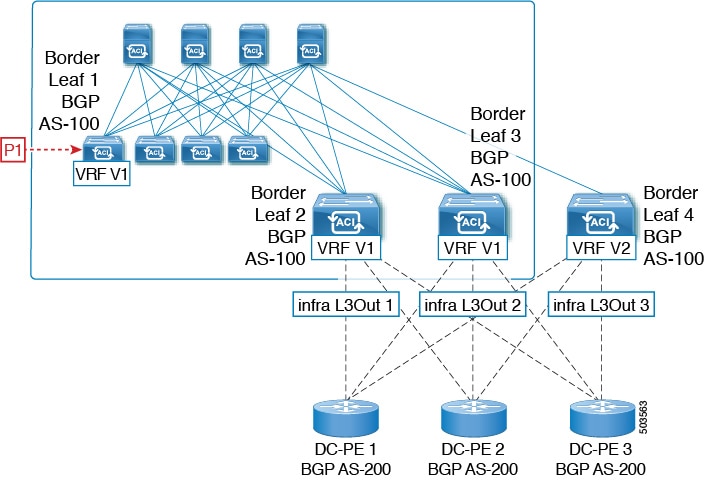
    The diagram illustrates a BGP routing loop scenario, highlighting how a prefix received from a BGP IP L3Out peer can be advertised within the ACI fabric and potentially lead to routing loops when re-imported.
  2. AS a transit case, this prefix can be advertised out externally through an SR-MPLS infra L3Out.
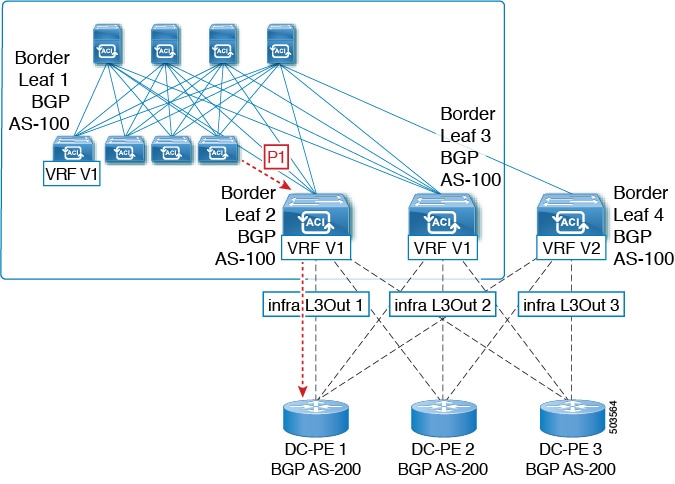
    The diagram illustrates a BGP routing loop scenario involving multiple VRFs and VPNs, highlighting how a prefix can be advertised and re-imported, potentially leading to a loop in the ACI fabric.
  3. This prefix could then be imported back into the ACI fabric from the core, either in the same VRF or in a different VRF.
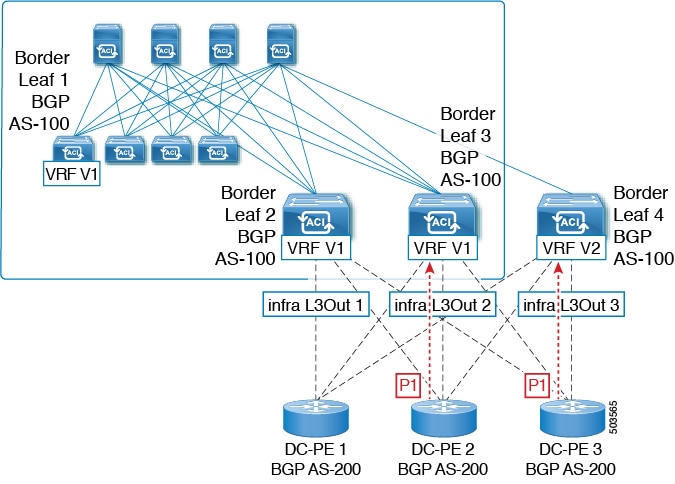
    The diagram illustrates the BGP Domain-Path feature, highlighting how it prevents routing loops in a network by managing prefix advertisements between different VRFs and the core infrastructure.
  4. A BGP routing loop would occur when this imported prefix is then advertised back to the originating switch, either from the same VRF or through a leak from a different VRF.
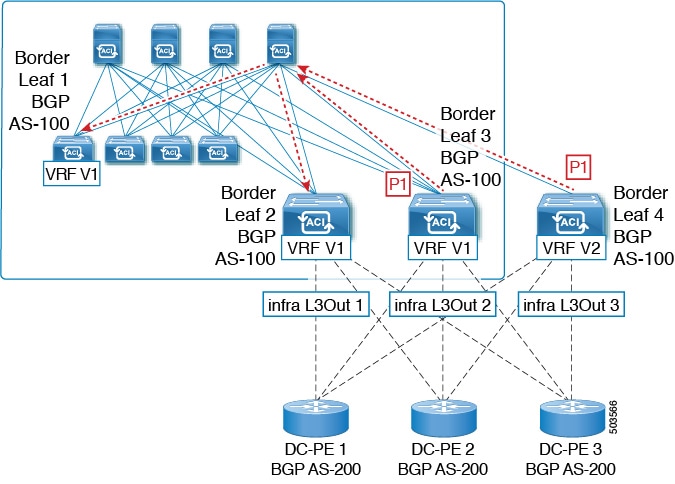
    The BGP Domain-Path feature prevents routing loops by blocking routes exported from a VRF on one switch from being received back into the same VRF on another switch. This ensures that prefixes are not advertised back to their originating switch, maintaining network stability.

Within an ACI fabric, the VRF scope is global and is extended to all switches where it is configured. Therefore, a route that is exported out of a domain in a VRF is blocked from being received back into the VRF on any other switch.

These components are used with the BGP Domain-Path feature for loop prevention:

  • Routing domain ID: Every tenant VRF in an ACI site is associated with one internal fabric domain, one domain for each VRF in each SR-MPLS infra L3Out, and one domain for each IP L3Out. When the BGP Domain-Path feature is enabled, each of these domains is assigned a unique routing domain ID, in the format Base:<variable>, where:

    • Base is the non-zero value that was entered in the Domain ID Base field in the BGP Route Reflector Policy page

    • <variable> is a randomly-generated value specifically for that domain

  • Domain path: The domain segments traversed by a route are tracked using a BGP domain path attribute:

    • The domain ID of the VRF for the source domain where the route is received is prepended to the domain path

    • The source domain ID is prepended to the domain path while re-originating a route across domains on the border leaf switches

    • An external route is not accepted if any of the local domain IDs for the VRFs is in the domain path

    • The domain path is carried AS an optional and transitive BGP path attribute with each domain segment, represented AS <Domain-ID:SAFI>

    • The ACI border leaf switches prepend the VRF internal domain ID for both locally originated and external routes to track leaks within the domain

    • A route from the internal domain can be imported and installed in a VRF on a node with a conflicting external domain ID to provide an internal backup or transit path

    • For infra L3Out peers, the advertisement of a route to a peer is skipped if the domain ID of the peer domain is present in the domain path of the route (outbound check is not applicable for IP L3Out peers)

    • The border leaf switches and non-border leaf switches will both process the domain path attribute

Note

You can configure the BGP Domain-Path feature for loop prevention, or simply enable the configuration to send a received domain path, through the GUI or REST API. You cannot configure the BGP Domain-Path feature for loop prevention or enable the configuration to send a received domain path through the NX-OS style CLI.

Note

When upgrading to Release 5.1(3) from a previous release, if you have contracts configured for inter-VRF shared services, those contracts might not work AS expected with the BGP Domain-Path feature for loop prevention because the BGP domain ID would not have been set in those contracts that were configured before you upgraded to Release 5.1(3). In those situations, delete the contract and then add the contract back, which will allow the BGP domain update to occur. This is only an issue when you have contracts that were configured prior to your upgrade to Release 5.1(3); this is not an issue when you create new contracts after you've completed the upgrade to Release 5.1(3).


Configure the BGP Domain-Path feature for loop prevention using the GUI

Enable BGP Domain-Path feature to prevent routing loops by identifying different routing domains and controlling BGP route propagation between them.
The BGP Domain-Path feature provides loop prevention by assigning routing domain IDs to VRFs, IP L3Outs, and SR-MPLS infra L3Outs. Configure this feature when you need to prevent BGP routing loops in complex network topologies, especially in Multi-Site environments.

Before you begin

Become familiar with the BGP Domain-Path feature using the information provided in BGP Domain-Path feature for loop prevention.

Procedure

  1. If you want to use the BGP Domain-Path feature for loop prevention, set the BGP Domain-Path attribute on the BGP route reflector.

    Note

    If you do not want to use the BGP Domain-Path feature for loop prevention but you still want to send a received domain path, do not enable the BGP Domain-Path feature on the BGP route reflector in this step. Instead, go directly to 2 to only enable the Send Domain Path field in the appropriate BGP connectivity window.

    1. Navigate to System > System Settings > BGP Route Reflector.

      The BGP Route Reflector window appears. Verify that the Policy page tab is selected in this window.

    2. Locate the Domain ID Base field.
    3. Enter a number in the Domain ID Base field.
      • Enter a value between 1-4294967295 to enable the BGP Domain-Path feature. If your ACI fabric is part of a Multi-Site environment, make sure that you use a unique value that will be specific for this ACI fabric in this Domain ID Base field.

      • To disable the BGP Domain-Path feature, enter 0 in this Domain ID Base field.

      When the BGP Domain-Path feature for loop prevention is enabled, an implicit routing domain ID of the format Base:<variable> will be allocated, where:

      • Base is the non-zero value that you entered in this Domain ID Base field

      • <variable> is a randomly-generated value specifically for the VRF or L3Out that will be used for the BGP Domain-Path feature for loop prevention

      This routing domain ID is passed to BGP to identify the following domains:

      • VRF: Identified by an internal domain ID using a randomly-generated value specifically for each VRF, as shown in the Routing Domain ID field in the Policy tab in the VRF window for that tenant

      • IP L3Out: Identified by an external domain ID using a randomly-generated value specifically for each IP L3Out, as shown in the Routing Domain ID field in the BGP Peer Connectivity Profile window for that IP L3Out

      • SR-MPLS infra L3Out: Identified by an external domain ID using a randomly-generated value specifically for each VRF in each SR-MPLS infra L3Out, as shown in the Routing Domain ID column in the SR-MPLS Infra L3Outs table in the window for each SR-MPLS VRFL3Out

      The Domain-Path attribute is processed on the inbound directions to check for loops based on the routing domain IDs in the path. The Domain-Path attribute is sent to a peer, which is controlled separately through the BGP peer-level Send Domain Path field in the IP L3Out or in the SR-MPLS infraL3Out, as described in the next step.

  2. To send the BGP domain path attribute to a peer, enable the Send Domain Path field in the appropriate BGP connectivity window.

    If you want to use the BGP Domain-Path feature for loop prevention, first set the Domain Base ID in 1, then enable the Send Domain Path field here. If you do not want to use the BGP Domain-Path feature for loop prevention but you still want to send a received domain path, only enable the Send Domain Path field here (do not set the Domain Base ID in 1 in that case).

    • To enable the Send Domain Path field for a IP L3Out peer:

      1. Navigate to the BGP Peer Connectivity Profile window for the IP L3Out peer:

        Tenant > tenant_name > Networking > L3Outs > L3Out_name > Logical Node Profile > log_node_prof_name > Logical Interface Profile > log_int_prof_name > BGP Peer <address>-Node-<node_ID>

        The BGP Peer Connectivity Profile window for this configured L3Out appears.

      2. Locate the BGP Controls area in the BGP Peer Connectivity Profile window.

      3. In the BGP Controls area, click the box next to the Send Domain Path field.

      4. Click Submit.

        This action sends the BGP domain path attribute to a peer.

    • To enable the Send Domain Path field for a SR-MPLS infra L3Out peer:

      1. Navigate to Tenant > infra > Networking > SR-MPLS Infra L3Outs > SR-MPLS-infra-L3Out_name > Logical Node Profiles > log_node_prof_name.

        The Logical Node Profile window for this configured SR-MPLS infra L3Out appears.

      2. Locate the BGP-EVPN Connectivity Profile area, then determine if you want to create a new BGP-EVPN connectivity policy or if you want to enable the Send Domain Path field in an existing BGP-EVPN connectivity policy.

        • If you want to create a new a create a new BGP-EVPN connectivity policy, click + above the table in the BGP-EVPN Connectivity Profile area. The Create BGP-EVPN Connectivity Policy window appears.

        • If you want to enable the Send Domain Path field in an existing BGP-EVPN connectivity policy, double-click on that policy in the table in the BGP-EVPN Connectivity Profile area. The BGP-EVPN Connectivity Policy window appears.

      3. Locate the BGP Controls area in the window.

      4. In the BGP Controls area, click the box next to the Send Domain Path field.

      5. Click Submit.

        This action sends the BGP domain path attribute to a peer.

  3. Navigate to the appropriate areas to see the routing IDs assigned to the various domains.

    • To see the routing ID assigned to the VRF domain, navigate to:

      Tenants > tenant_name > Networking > VRFs > VRF_name, then click on the Policy tab for that VRF and locate the entry in the Routing Domain ID field in the VRF window.

    • To see the routing ID assigned to the IP L3Out domain, navigate to:

      Tenants > tenant_name > Networking > L3Outs > L3Out_name > Logical Node Profiles > log_node_prof_name > BGP Peer, then locate the entry in the Routing Domain ID field in the BGP Peer Connectivity Profile window.

    • To see the routing ID assigned to the SR-MPLS infra L3Out domain, navigate to:

      Tenants > tenant_name > Networking > SR-MPLS VRF L3Outs > SR-MPLS_VRF_L3Out_name, then locate the entry in the Routing Domain ID column in the SR-MPLS Infra L3Outs table in the window for that SR-MPLS VRFL3Out.

The BGP Domain-Path feature is configured for loop prevention, with routing domain IDs assigned to VRFs, IP L3Outs, and SR-MPLS infra L3Outs. BGP peers will receive domain path attributes according to your configuration settings.