Lists the network, AWS infrastructure, and Catalyst Center Global Manager instance requirements—including VPC, security group, and region settings—needed to prepare for a Catalyst Center Global Manager on AWS deployment using AWS CloudFormation.
Before deploying Catalyst Center Global Manager on AWS, ensure you meet these network, AWS, and requirements.
Network environment requirements
You have this information about your network environment on hand:
-
Enterprise DNS server IP address
-
(Optional) HTTPS network proxy details
AWS account requirements
You must meet these AWS account requirements:
-
You have valid credentials to access your AWS account.
We recommend that your AWS account be a subaccount (a child account) to maintain resource independence and isolation. A subaccount ensures that the Catalyst Center Global Manager deployment does not impact your existing resources.
-
Important: Your AWS account is subscribed to Cisco Catalyst Center Global Manager Virtual Appliance - BYOL in AWS Marketplace.
-
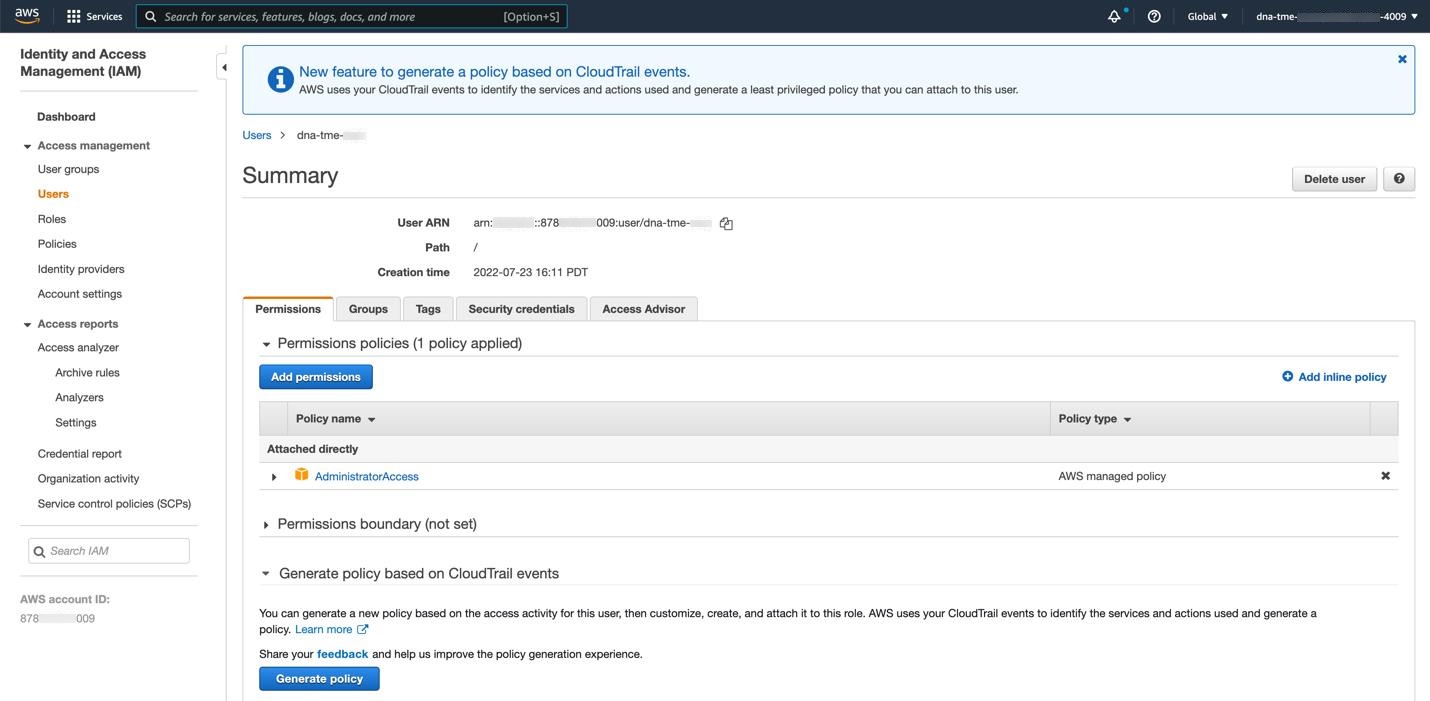
You have administrator access permission for your AWS account. In AWS, the policy name is displayed as AdministratorAccess.
AWS network infrastructure requirements
You must set up these resources and services in AWS:
-
VPC: The recommended CIDR range is /25. In IPv4 CIDR notation, the last octet (the fourth octet) of the IP address can only be 0 or 128. For example, x.x.x.0 or x.x.x.128 are valid options.
-
Subnets: The recommended subnet range is /28, and it should not overlap with your corporate subnet.
-
Route tables: Make sure that your VPC subnet is allowed to communicate with your enterprise network through your VPN Gateway (VPN GW) or Transit Gateway (TGW).
-
Security groups: To ensure communication between Catalyst Center Global Manager on AWS and the Catalyst Center in your enterprise network, the AWS security group attached to Catalyst Center Global Manager on AWS must allow the TCP port 443.
-
TCP ports: 443
For more information about the ports that Catalyst Center Global Manager uses, see Required firewall ports and connectivity.
-
-
VPN GW or TGW: You must have an existing connection to your enterprise network, which is your Customer Gateway (CGW).
For your existing connection from the CGW to AWS, ensure that the correct ports are open for traffic flow to and from your Catalyst Center Global Manager VA. You can open them using either the firewall settings or a proxy gateway. For information about the well-known network service ports that the appliance uses, see Required firewall ports and connectivity.
-
Site-to-Site VPN connection: You can use TGW attachments and TGW route tables.
AWS region configuration requirements
You must meet these AWS region configuration requirements:
-
Your AWS environment must be configured with one of these regions:
-
af-south-1 (Cape Town)
-
ap-east-1 (Hong Kong)
-
ap-northeast-1 (Tokyo)
-
ap-northeast-2 (Seoul)
-
ap-northeast-3 (Osaka)
-
ap-south-1 (Mumbai)
-
ap-south-2 (Hyderabad)
-
ap-southeast-1 (Singapore)
-
ap-southeast-2 (Sydney)
-
ap-southeast-3 (Jakarta)
-
ap-southeast-4 (Melbourne)
-
ca-central-1 (Canada Central)
-
ca-west-1 (Calgary)
-
eu-central-1 (Frankfurt)
-
eu-central-2 (Zurich)
-
eu-north-1 (Stockholm)
-
eu-south-1 (Milan)
-
eu-south-2 (Spain)
-
eu-west-1 (Ireland)
-
eu-west-2 (London)
-
eu-west-3 (Paris)
-
il-central-1 (Tel Aviv)
-
sa-east-1 (São Paulo)
-
us-east-1 (Northern Virginia)
-
us-east-2 (Ohio)
-
us-gov-east-1 (AWS GovCloud US-East)
-
us-gov-west-1 (AWS GovCloud US-West)
-
us-west-1 (Northern California)
-
us-west-2 (Oregon)
-
IAM user group requirement (optional)
If you want to enable multiple IAM users with the ability to configure Catalyst Center Global Manager using the same environment setup, you need to create a group with these policies and then add the required users to that group:
-
IAMReadOnlyAccess
-
AmazonEC2FullAccess
-
AWSCloudFormationFullAccess
Catalyst Center Global Manager instance requirements
The Catalyst Center Global Manager instance size must meet these minimum resource requirements:
-
c5.2xlarge
Catalyst Center Global Manager supports only the c5.2xlarge instance size. Any changes to this configuration aren't supported.
-
8 virtual CPUs (vCPUs)
-
16-GB RAM
-
650-GB storage, provisioned as two separate EBS-gp3 disks:
-
100-GiB disk
-
550-GiB disk
-
-
2500 disk input and output operations per second (IOPS)
-
180-MBps disk bandwidth
Catalyst Center Global Manager backup instance requirements
The Catalyst Center Global Manager backup instance must meet these minimum resource requirements based on if you use a cloud server or an enterprise (on-premises) server:
-
Cloud backup: t3.micro, 2 vCPUs, 1-GB RAM, and for storage, see Backup storage requirements.
-
Enterprise backup: See Backup server requirements and Backup storage requirements.
AWS information requirements
You have this AWS information on hand:
-
Subnet ID
-
Security group ID
-
Keypair ID
-
Environment name
-
CIDR reservation
Catalyst Center Global Manager environment requirements
You must meet these requirements for your Catalyst Center Global Manager environment:
-
You have access to the Catalyst Center Global Manager GUI.
-
You have this Catalyst Center Global Manager information on hand:
-
Default gateway setting
-
CLI password
-
FQDN for the Catalyst Center Global Manager VA IP address
-