Cisco Catalyst Center Global Manager Deployment Guide, Release 1.4.1

PDF

Cisco Catalyst Center Global Manager Deployment Guide, Release 1.4.1

Deploy Catalyst Center Global Manager on AWS using AWS CloudFormation

Want to summarize with AI?

Log in

Provides step-by-step instructions for creating the stack and configuring the parameters to deploy Catalyst Center Global Manager on AWS.


Follow these steps to deploy Catalyst Center Global Manager on AWS using AWS CloudFormation. The provided AWS CloudFormation template contains the relevant details for all required parameters.

Before you begin

Ensure that

Procedure

1.

Verify that the TAR file is genuine and from Cisco Systems, Inc.

2.

Log in to the AWS console.

The AWS console is displayed.

3.

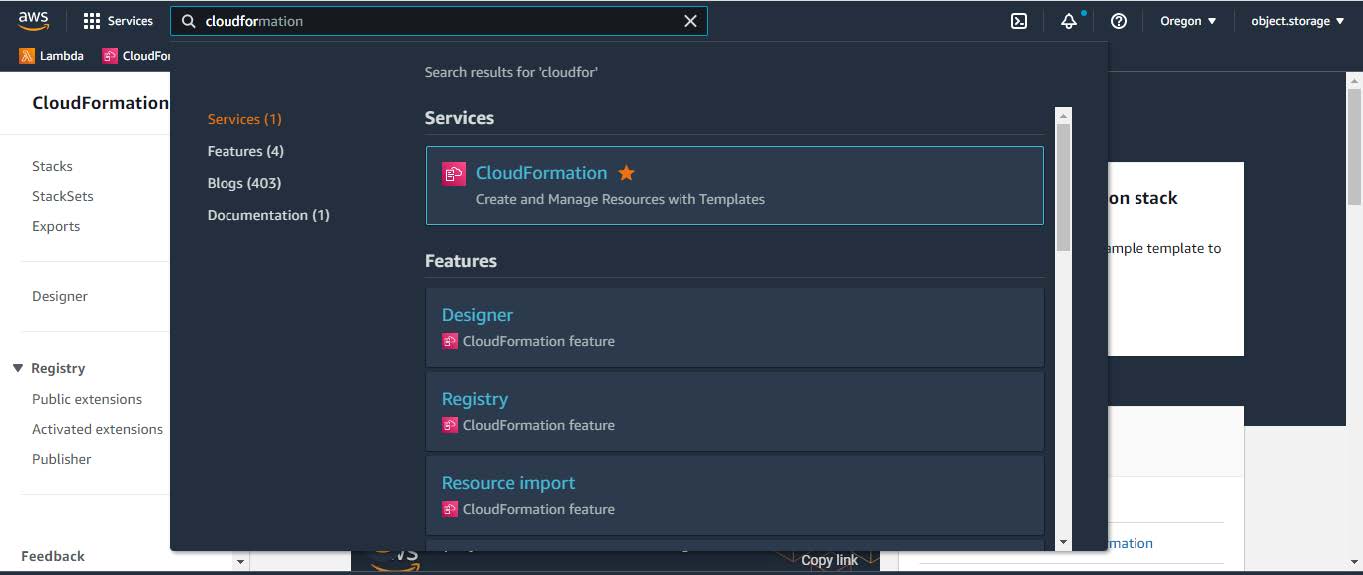
In the search bar, enter cloudformation.
4.

From the drop-down menu, choose CloudFormation.

5.

Click Create stack and choose With new resources (standard).

6.

Under Specify template, select Upload a template file, and choose the AWS CloudFormation template that you downloaded in Step 1.

7.

Enter a stack name and review these parameters:

  • EC2 Instance Configuration

    • Environment Name: Assign a unique environment name.

      The environment name is used to differentiate the deployment and is prepended to your AWS resource names. If you use the same environment name as a previous deployment, the current deployment will fail.

    • Private Subnet ID: Enter the VPC subnet to be used for Catalyst Center Global Manager.

    • Security Group: Enter the security group to be attached to the Catalyst Center Global Manager VA that you are deploying.

    • Keypair: Enter the SSH keypair used to access the CLI of Catalyst Center Global Manager VA that you are deploying.

  • Catalyst Center Global Manager Configuration: Enter this information:

    • CatalystCenterGlobal ManagerInstanceIP: Catalyst Center Global ManagerIP address.

    • CatalystCenterGlobal ManagerNetmask: Catalyst Center Global Manager netmask.

    • CatalystCenterGlobal ManagerGateway: Catalyst Center Global Manager gateway address.

    • CatalystCenterGlobal ManagerDnsServer: Enterprise DNS Server.

    • CatalystCenterGlobal ManagerPassword: Catalyst Center Global Manager password.

      Note

      You can use the Catalyst Center Global Manager password to access the Catalyst Center Global Manager VA CLI through the AWS EC2 Serial Console.

      The password must

      • omit any tab or line breaks

      • have at least eight characters, and

      • contain characters from at least three of these categories.

        • Lowercase letters (a-z)

        • Uppercase letters (A-Z)

        • Numbers (0-9)

        • Special characters (for example, ! or #)

    • CatalystCenterGlobal ManagerFQDN: Catalyst Center Global Manager FQDN.

    • CatalystCenterGlobal ManagerHttpsProxy: (Optional) Enterprise HTTPS proxy.

    • CatalystCenterGlobal ManagerHttpsProxyUsername: (Optional) HTTPS proxy username.

    • CatalystCenterGlobal ManagerHttpsProxyPassword: (Optional) HTTPS proxy password.

8.

(Optional) Click Next to configure the stack options.

9.

Click Next to review your stack information.

10.

Click Submit when you are satisfied with the configuration.

Stack creation usually takes 45 to 60 minutes.


Verify the Catalyst Center Global Manager VA TAR file

Before deploying the Catalyst Center VA, we recommend that you verify that the TAR file that you downloaded is a genuine Cisco TAR file.

Before you begin

Ensure that you downloaded the Catalyst Center Global Manager VA TAR file from the Cisco Software Download site.

Procedure

1.

Download the secure hash algorithm (SHA512) checksum file for the TAR file from the same location specified for downloading the Catalyst Center Global Manager OVA file, as specified by Cisco.

2.

Obtain the signature file (.sig) for the TAR file from Cisco support through email or by download from the secure Cisco website (if available).

3.

(Optional) Perform an SHA verification to determine whether the TAR file is corrupted due to a partial download.

Depending on your operating system, enter one of these commands:

  • On a Linux system: sha512sum <tar-file-filename>

  • On a macOS system: shasum -a 512 <tar-file-filename>

On Microsoft Windows, use the certutil tool because it does not include a built-in checksum utility:

certutil -hashfile <filename> sha256

For example:

On Windows, you can also use Windows PowerShell to generate the digest. For example:

Compare the command output to the SHA512 checksum file that you downloaded. If the command output does not match the SHA512 checksum file, download the TAR file again and run the appropriate command again. If the output still does not match, contact Cisco support.

4.

Verify that the TAR file is genuine and from Cisco by verifying its signature:

openssl dgst -sha512 -verify cisco_image_verification_key.pub -signature <signature-filename> <tar-file-filename>

Note

This command works in both Mac and Linux environments. For Windows, you must download and install OpenSSL (available on the OpenSSL Downloads site) if you have not already done so.

If the TAR file is genuine, running this command displays a Verified OK message. If this message fails to appear, do not install the TAR file and contact Cisco support.


Validate the deployment

Perform these validation checks to ensure that your environment setup and Catalyst Center Global Manager VA configuration work.

Before you begin

Ensure that your stack creation on AWS CloudFormation has no errors.

Procedure

1.

From the Amazon EC2 console, validate the network and system configuration and verify that the Catalyst Center Global Manager IP address is correct.

2.

Send a ping to the Catalyst Center Global Manager IP address to ensure that your host details and network connection are valid.

3.

Establish an SSH connection with Catalyst Center Global Manager to verify that Catalyst Center Global Manager is authenticated.

4.

Test HTTPS accessibility to the Catalyst Center Global Manager GUI using one of these methods: