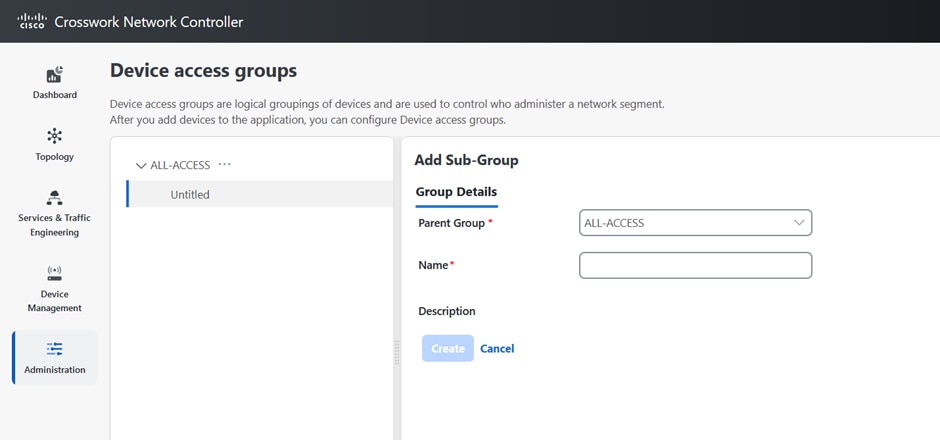
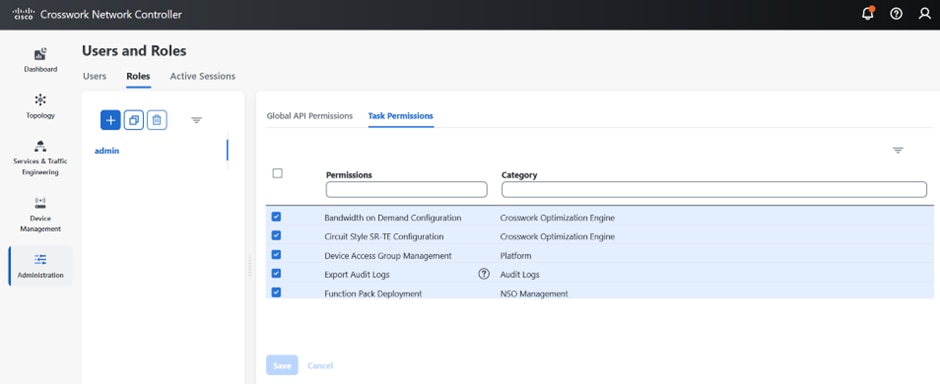
When a user is associated with one or more Device Access Groups, they can make configuration changes and provision services on the devices within those groups. A Crosswork Network Controller user with an administrator role or a mapped Device Access Groups management task can:
-
Create and manage Device Access Groups.
-
Assign users to specific Device Access Groups.
-
Define and control which devices users can access and modify.
-
Ensure that users have the appropriate permissions to perform their tasks on designated devices.
Device Access Groups control device-level WRITE or Provisioning and Crosswork Network Controller flows that trigger such operations. They do not affect WRITE or EDIT operations within Crosswork Network Controller itself.
You can restrict users to specific tasks based on their role's permissions, ensuring only authorized individuals have access and control over their actions within the system. Crosswork Network Controller's role-based access control synchronizes with NSO and Device Access Groups to streamline device configurations, using JWT tokens for authentication and authorization in RESTCONF and JSON-RPC API workflows. However, reverse synchronization is not possible; changes in NSO are not reflected in Crosswork Network Controller Device Access Groups (for detailed information on the prerequisites for setting up NSO, refer to Configure NSO Servers). External LDAP, TACACS, and RADIUS servers support Device Access Groups integration.
Summary
The Device Access Group process involves Crosswork Network Controller users, roles, Device Access Groups, NSO synchronization, and external authentication servers.
-
Crosswork Network Controller users make configuration changes and provision services on devices in associated Device Access Groups.
-
Administrators or users with the mapped Device Access Groups management task create groups, assign users, and control device access.
-
Crosswork Network Controller role-based access control synchronizes with NSO and Device Access Groups for RESTCONF and JSON-RPC API workflows.
Workflow
These stages describe how device access groups work.
- A Crosswork Network Controller user is associated with one or more Device Access Groups.
- The user makes configuration changes and provisions services on devices within those groups.
- Crosswork Network Controller uses role permissions and Device Access Group privileges to restrict or allow operations on devices.
- Crosswork Network Controller synchronizes role-based access control with NSO and Device Access Groups for supported workflows.
 icon next to ALL-ACCESS, then click