Explains the various types of certificates used in Crosswork Network Controller, their roles, properties, and usage for different communication channels.
The following figure shows how Crosswork Network Controller uses certificates for various communication channels.
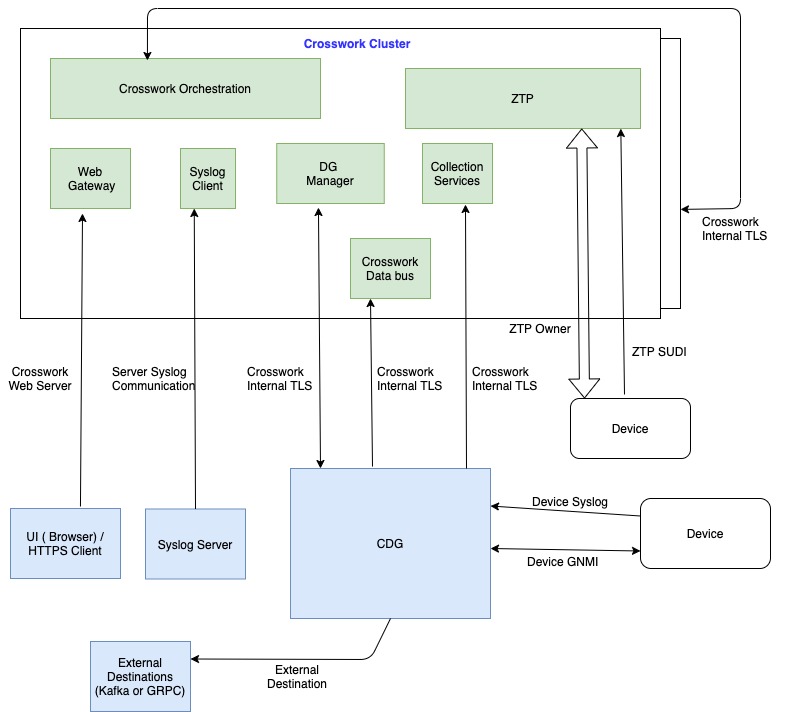
These certificates are classified into various roles with different properties depending on their use case as shown in the following table.
| Role |
Crosswork internal TLS |
| UI Name |
Crosswork-Internal-Communication |
| Description |
|
| Server |
Crosswork Network Controller |
| Client |
Crosswork Data Gateway Crosswork Network Controller |
| Allowed operations |
Download |
| Default expiry |
5 years |
| Allowed expiry |
— |
| Role |
Device syslog communication |
| UI Name |
Crosswork-Device-Syslog |
| Description |
|
| Server |
Crosswork Data Gateway |
| Client |
Device |
| Allowed operations |
Download |
| Default expiry |
5 years |
| Allowed expiry |
— |
| Role |
ZTP SUDI |
| UI Name |
Crosswork-ZTP-Device-SUDI |
| Description |
|
| Server |
Crosswork ZTP |
| Client |
Device |
| Allowed operations |
|
| Default expiry |
100 years |
| Allowed expiry |
31 days to 100 years. The validity period is user-defined. |
| Role |
Secure ZTP provisioning |
| UI Name |
Crosswork-ZTP-Owner |
| Description |
|
| Server |
Crosswork ZTP |
| Client |
Device |
| Allowed operations |
|
| Default expiry |
5 years |
| Allowed expiry |
31 days to 30 years. The validity period is user-defined. |
| Role |
Crosswork web server |
| UI Name |
Crosswork-Web-Cert |
| Description |
|
| Server |
Crosswork Web Server |
| Client |
User browser or API client |
| Allowed operations |
|
| Default expiry |
5 years |
| Allowed expiry |
Default expiry period is 5 years. Users can override this by uploading their own certificate. The allowed period is 31 days to 10 years. |
| Role |
Provider gRPC communication |
| UI Name |
— |
| Description |
SR-PCE requires gRPC to discover topology and SR-MPLS policies. This certificate enables Transport Layer Security (TLS) and is required when the SR-PCE provider protocol is set to GRPC_SECURE. |
| Server |
Crosswork Network Controller |
| Client |
Clients that want secure connection to the gRPC server (Crosswork Data gateway, Device Group Manager pods, and so on) |
| Allowed operations |
|
| Default expiry |
— |
| Allowed expiry |
The validity period is user-defined. |
| Role |
Device gNMI/gRPC communication |
| UI Name |
— |
| Description |
Provides GNMI telemetry communications between devices and Crosswork Data Gateway. |
| Server |
Crosswork Data Gateway |
| Client |
Device |
| Allowed operations |
|
| Default expiry |
100 years |
| Allowed expiry |
31 days to 100 years. The validity period is user-defined. |
| Role |
Server syslog communication |
| UI Name |
— |
| Description |
|
| Server |
External syslog server |
| Client |
Crosswork Network Controller |
| Allowed operations |
|
| Default expiry |
— |
| Allowed expiry |
31 days to 100 years. The validity period is user-defined. |
| Role |
External destination |
| UI Name |
— |
| Description |
Exports telemetry data from Crosswork Data Gateway to external destinations (Kafka or gRPC) after performing a mutual-authentication. |
| Server |
External Destinations (Kafka or gRPC) |
| Client |
Crosswork Data Gateway |
| Allowed operations |
|
| Default expiry |
100 years |
| Allowed expiry |
31 days to 100 years. The validity period is user-defined. |
| Role |
External destination server auth |
| UI Name |
— |
| Description |
Exports telemetry data from Crosswork Data Gateway to external destinations (Kafka or gRPC) after performing a server-based authentication. |
| Server |
External Crosswork Data Gateway Destinations (Kafka or gRPC) |
| Client |
Crosswork Data Gateway |
| Allowed operations |
|
| Default expiry |
100 years |
| Allowed expiry |
31 days to 100 years. The validity period is user-defined. |
| Role |
Secure LDAP communication |
| UI Name |
— |
| Description |
Crosswork Network Controller uses the trust chain of this certificate to authenticate the secure LDAP server. |
| Server |
Secure LDAP server |
| Client |
Crosswork Network Controller |
| Allowed operations |
|
| Default expiry |
— |
| Allowed expiry |
31 days to 30 years. The validity period is user-defined. |
| Role |
Accedian provider mutual auth |
| UI Name |
— |
| Description |
Required to add provider connectivity assurance as a provider |
| Server |
Provider |
| Client |
Crosswork Network Controller |
| Allowed operations |
|
| Default expiry |
— |
| Allowed expiry |
31 days to 30 years. The validity period is user-defined. |
There are two category roles in Crosswork Network Controller:
-
Roles which allow you to upload or download trust chains only.
-
Roles that allow upload or download of both the trust chain and an intermediate certificate and key.