Radio Aware Routing and Dynamic Link Exchange Protocol

This chapter contains the following sections:

Radio aware routing

Radio aware routing is a mechanism that

  • uses radios to interact with the routing protocol OSPFv3/EIGRP to signal the appearance, disappearance, and link conditions of one-hop routing neighbors,

  • addresses the need for faster convergence, more efficient route selection, and better performance for delay-sensitive traffic in mobile ad hoc networks, and

  • provides a solution for lengthy protocol timers that are not recommended in mobile networks.

Mobile ad hoc networking characteristics

Relief workers, soldiers, public safety personnel, and others need the right information, in the right place, at the right time, wherever they are located. Mobile ad hoc networks are emerging to address these needs. The IETF request for comment, RFC RFC5578, defines a PPP-over-Ethernet (PPPoE) based mechanism for integrating IP routers and mobile radios in ad hoc networks, enabling faster convergence, more efficient route selection, and better performance for delaysensitive traffic.

In large mobile networks, connections to the routing neighbors are often interrupted due to distance and radio obstructions. When these signals do not reach the routing protocols, protocol timers are used to update the status of a neighbor. Routing protocols have lengthy timers, which is not recommended in mobile networks.

The RAR feature is supported on the Cisco ESR6300 Embedded Series Router.

Mobile ad hoc networks are emerging as a means for delivering the benefits of IP networking to users operating beyond the reach of a fixed network. In ad hoc networks, mobile nodes associate on an extemporaneous or ad hoc basis. Ad hoc networks have numerous distinguishing characteristics when compared to conventional networking solutions:

  • Self-forming — Nodes that come within radio range of each other can establish a network association without any pre-configuration or manual intervention.

  • Self-healing — Nodes can join or leave rapidly without affecting operation of the remaining nodes.

  • No infrastructure — In an ad hoc network, mobile nodes form their own network, and essentially become their own infrastructure.

  • Peer to peer — Traditional networks typically support end systems operating in client-server mode. In an ad hoc network, mobile nodes can communicate and exchange information without prior arrangement and without reliance on centralized resources.

  • Predominantly wireless — Historically networks have been mostly wired, and enhanced or extended through wireless access. The ad hoc environment is essentially wireless, but can be extended to support wired resources.

  • Highly dynamic — Mobile nodes are in continuous motion and ad hoc networking topologies are constantly changing.

Collectively, these characteristics will enable ad hoc networks to deliver timely information to a new and underserved class of users. Ad hoc networking solutions can be applied to virtually any scenario that involves a cadre of highly mobile users or platforms (which may include stationary devices as well), a strong need to share IP-based information, and an environment in which fixed infrastructure is impractical, impaired, or impossible.

Real-world problem scenario

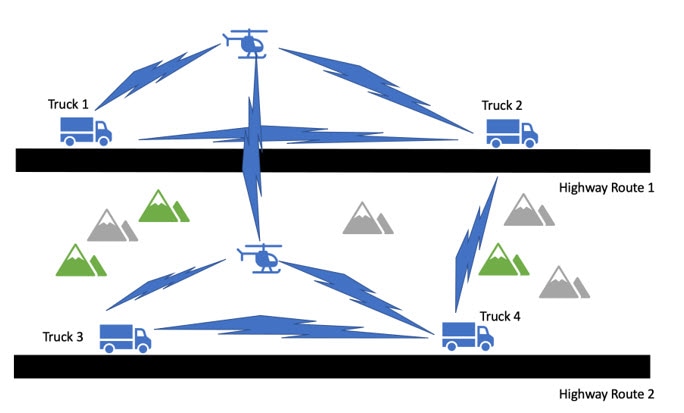
Consider the scenario in this network diagram:

The network diagram illustrates a voice, video, and data communication setup between moving vehicles, highlighting the ad hoc networking capabilities in environments where fixed infrastructure is not feasible.

The network is a voice, video, data network between moving vehicles that consists of both ground and air vehicles, hence the network is mobile and it is a peer to peer mesh that changes as topographical obstructions are encountered. This is where we get the term mobile ad hock network or MANET for short.

In the scenario in the drawing, all 4 trucks always have connectivity with the helicopters that are flying over the same road. The two helicopters always have line of sight and will always have a connection between each other. The trucks may even be able to connect to the other helicopter or a truck on the opposite road when conditions are favorable.

Here we see that the path between trucks 1 and 3 are completely blocked. The path between Truck 2 and 4 is about to be blocked.

Our existing routing protocols such as OSPFv3 and EIGRP need to adjust its path metrics very quickly to maintain a cohesive operational network. The routing protocol also needs a way to get that information from the radios and that requires a radio to router protocol that is delivered by Cisco Radio Aware Routing in the form of two open protocols:

  • PPP over Ethernet (PPPoE)

  • Dynamic Link Exchange Protocol (DLEP)

Both protocols are discussed later in this document.

Benefits of radio aware routing

The Radio Aware Routing feature offers multiple benefits for network performance and routing optimization.

  • Provides faster network convergence through immediate recognition of changes.

  • Enables routing for failing or fading radio links.

  • Allows easy routing between line-of-sight and non-line-of-sight paths.

  • Provides faster convergence and optimal route selection so that delay-sensitive traffic, such as voice and video, is not disrupted

  • Provides efficient radio resources and bandwidth usage.

  • Reduces impact on the radio links by performing congestion control in the router.

  • Allows route selection based on radio power conservation.

  • Enables decoupling of the routing and radio functionalities.

  • Provides simple Ethernet connection to RFC 5578 and DLEP compliant radios.

Restrictions for radio aware routing and DLEP features

The Radio Aware Routing and DLEP features have these restrictions and limitations:

  • Multicast traffic is not supported with DLEP, but is supported with PPPOE.

  • DLEP does not support IPv6

  • Cisco High Availability (HA) technology is not supported.

  • Requires the Network Advantage license.


Note


There is a condition that exists with DLEP that is not unique to the ESR6300. An ARP which has been learned on a VMI does not get deleted when the mapped physical interface goes down.

Note


Previous releases of IOS XE offered support for IPv4 unicast traffic over an IPv4 DLEP session. IOS XE 17.12.1a provides support for IPv6 unicast, IPv4 multicast and IPv6 multicast over an IPv4 DLEP. See the Restrictions for DLEP IPv6 unicastsection.

Performance

The Radio Aware Routing feature supports a maximum of 10 neighbors per radio or VMI interface, with a total capacity of 30 to 40 neighbors.

System components

System components are infrastructure elements that

  • implement the Radio Aware Routing (RAR) feature using the MANET (Mobile adhoc network) infrastructure

  • include PPPOE, Virtual multipoint interface (VMI), QoS, routing protocol interface and RAR protocols, and

  • provide communication mechanisms between radio and router components.

Component details

The system includes multiple specialized components:

  • Point-to-Point Protocol over Ethernet PPPOE or PPPOE: PPPOE is a well-defined communication mechanism between the client and the server. In the RAR implementation, radio takes the role of the PPPOE client and router takes the role of the PPPOE server. This allows a loose coupling of radio and router, while providing a well-defined and predictable communication mechanism. As PPPOE is a session or a connection oriented protocol, it extends the point-to-point radio frequency (RF) link from an external radio to an IOS router.

  • PPPOE Extensions: PPPOE extensions are used when the router communicates with the radio. In the Cisco IOS implementation of PPPOE, each individual session is represented by virtual access interface (connectivity to a radio neighbor) on which, QoS can be applied with these PPPOE extensions. RFC5578 provides extensions to PPPOE to support credit-based flow control and session-based real time link metrics, which are very useful for connections with variable bandwidth and limited buffering capabilities (such as radio links).

  • Virtual Multipoint Interface (VMI): Though PPPOE Extensions provides most of the setup to communicate between a router and a radio, VMI addresses the need to manage and translate events that higher layers (example, routing protocols) consume. In addition, VMI operates in the Bypass mode.

VMI supports two operational modes:

  • Bypass mode: Every Virtual Access Interface (VAI) representing a radio neighbor is exposed to routing protocols OSPFv3 and EIGRP, so that, the routing protocol directly communicates with the respective VAI for both unicast and multicast routing protocol traffic.

  • Aggregate mode: VMI is exposed to the routing protocols (OSPF) so that the routing protocols can leverage VMI for their optimum efficiency. When the network neighbors are viewed as a collection of networks on a point-to-multipoint link with broadcast and multicast capability at VMI, VMI helps in aggregating the multiple virtual access interfaces created from PPPOE. VMI presents a single multi access layer 2 broadcast capable interface. The VMI layer re-directs unicast routing protocol traffic to the appropriate P2P link (Virtual-Access interface), and replicates any Multicast/Broadcast traffic that needs to flow. Since the routing protocol communicates to a single interface, the size of the topology database is reduced, without impacting the integrity of the network.


Note


DLEP only supports aggregate mode. The preferred mode for PPPOE is bypass.

Radio aware routing topology

A radio aware routing topology is a network architecture that

  • integrates IP routing and mobile radio communications through device-to-radio links

  • enables immediate notification when nodes join or leave the network, allowing devices to recognize topology changes faster than timer-based methods

  • provides cross-layer feedback using PPPoE extensions defined in RFC 5578 for Ethernet-based communications between devices and mobile radios, and

  • establishes PPPoE sessions on behalf of every device and radio neighbor discovered in the network to report radio network status.

Mobile ad hoc networks implementation

Mobile Ad Hoc Networks (MANETs) for device-to-radio communications address the challenges faced when merging IP routing and mobile radio communications in ad hoc networking applications.

Through the device-to-radio link, the radio can inform the device immediately when a node joins or leaves, and this enables the device to recognize topology changes more quickly than if it had to rely on timers. Without this link-status notification from the radio, the device would likely time out while waiting for traffic. The link-status notification from the radio enables the device to respond faster to network topology changes. Metric information regarding the quality of a link is passed between the device and radio, enabling the device to more intelligently decide on which link to use.

With the link-status signaling provided by the device-to-radio link, applications such as voice and video work better because outages caused by topology changes are reduced or eliminated. Sessions are more stable and remain active longer.

Cross-layer feedback for device-to-radio integration of Radio-Aware Routing (RAR) takes advantage of the functions defined in RFC 5578. The RFC 5578 is an Internet Engineering Task Force (IETF) standard that defines PPP over Ethernet (PPPoE) extensions for Ethernet-based communications between a device and a mobile radio, that operates in a variable-bandwidth environment and has limited buffering capabilities. These extensions provide a PPPoE session-based mechanism for sharing radio network status such as link-quality metrics and establishing flow control between a device and an RAR-compliant radio.

An RAR-compliant radio initiates a Layer 2 PPPoE session with its adjacent device on behalf of every device and radio neighbor discovered in the network. These Layer 2 sessions are the means by which radio network status for each neighbor link is reported to the device. The radio establishes the correspondence between each PPPoE session and each link to a neighbor.

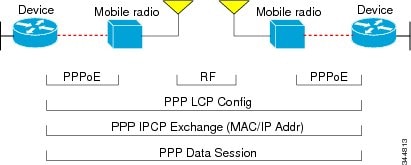
PPPoE interfaces enable intranodal communications between devices and radios:

  • Each radio initiates the PPPoE session as soon as the radio establishes a radio link to another radio

  • After the PPPoE sessions are active, a PPP session is established end-to-end (device-to-device)

  • The virtual multipoint interface (VMI) on the device can aggregate multiple PPPoE sessions and multiplex them to look like a single interface to the routing processes

  • Virtual access interfaces are associated with each of the PPP and PPPoE connections underneath the VMI

Figure 1. PPPoE session exchange between mobile devices and directional radios
The diagram illustrates the PPPoE session exchange process between mobile devices and directional radios, highlighting the establishment of end-to-end PPP sessions and the role of the virtual multipoint interface in aggregating multiple sessions.

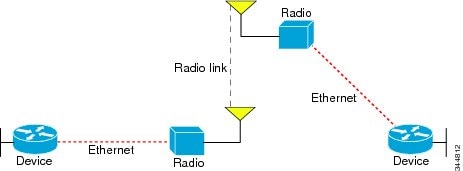
This capability requires that a Radio-Aware Routing (RAR)-compliant radio be connected to a device through Ethernet. The device always considers the Ethernet link to be up. If the radio side of the link goes down, the device waits until a routing update timeout occurs to declare the route down and then updates the routing table.

Figure 2. Device-to-radio link
The device-to-radio link illustrates the connection between a device and a Radio-Aware Routing-compliant radio, highlighting the signaling process for neighbor status in dynamic Mobile Ad Hoc Networks.

Neighbor up and down signaling

Mobile Ad Hoc Networks (MANETs) are highly dynamic environments. Nodes might move into, or out of, radio range at a fast pace. Each time a node joins or leaves, the network topology must be logically reconstructed by the devices. Routing protocols normally use timer-driven hello messages or neighbor timeouts to track topology changes, but MANETs reliance on these mechanisms can result in unacceptably slow convergence.

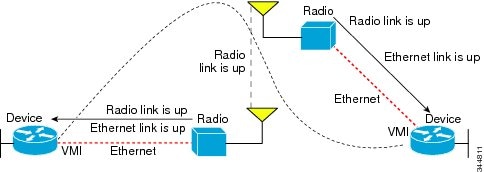
The neighbor up/down signaling capability provides faster network convergence by using link-status signals generated by the radio. The radio notifies the device each time a link to another neighbor is established or terminated by the creation and termination of PPP over Ethernet (PPPoE) sessions. In the device, the routing protocols (Open Shortest Path First version 3 [OSPFv3] or Enhanced Interior Gateway Routing Protocol [EIGRP]) respond immediately to these signals by expediting formation of a new adjacency (for a new neighbor) or tearing down an existing adjacency (if a neighbor is lost). For example, if a vehicle drives behind a building and loses its connection, the device immediately senses the loss and establishes a new route to the vehicle through neighbors that are not blocked. This high-speed network convergence is essential for minimizing dropped voice calls and disruptions to video sessions.

When virtual multipoint interfaces (VMIs) with PPPoE are used and a partner node has left or a new one has joined, the radio informs the device immediately of the topology change. Upon receiving the signal, the device immediately declares the change and updates the routing tables. The signaling capability provides these advantages:

  • Reduces routing delays and prevents applications from timing out

  • Enables network-based applications and information to be delivered reliably and quickly over directional radio links

  • Provides faster convergence and optimal route selection so that delay-sensitive traffic such as voice and video are not disrupted

  • Reduces impact on radio equipment by minimizing the need for internal queueing and buffering

  • Provides consistent quality of service for networks with multiple radios

The messaging allows for flexible rerouting when necessary because of these factors:

  • Fading of the radio links

  • Congestion of the radio links

  • Radio link power fade

  • Utilization of the radio

Figure 3. Up and down signaling sequence
The up and down signaling sequence illustrates the process of establishing PPPoE sessions between radios in a network, highlighting the interactions necessary for maintaining quality of service amid varying conditions.

PPPoE credit-based and metric-based scaling and flow control

Each radio initiates a PPP over Ethernet (PPPoE) session with its local device as soon as the radio establishes a link to another radio. Once the PPPoE sessions are active for each node, a PPP session is then established end-to-end (device-to-device). This process is duplicated each time a radio establishes a new link.

The carrying capacity of each radio link might vary due to location changes or environmental conditions, and many radio transmission systems have limited buffering capabilities. To minimize the need for packet queueing in the radio, PPPoE protocol extensions enable the device to control traffic buffering in congestion situations. Implementing flow-control on these device-to-radio sessions allows use of quality of service (QoS) features such as fair queueing.

The flow-control solution utilizes a credit-granting mechanism documented in RFC 5578. When the PPPoE session is established, the radio can request a flow-controlled session. If the device acknowledges the request, all subsequent traffic must be flow controlled. If a flow-control session is requested and cannot be supported by the device, the session is terminated. Typically, both the radio and the device initially grant credits during session discovery. Once a device exhausts its credits, it must stop sending until additional credits are granted. Credits can be added incrementally over the course of a session.

Metrics scaling is used with high-performance radios that require high-speed links. The radio can express the maximum and current data rates with different scaler values. Credit scaling allows a radio to change the default credit grant (or scaling factor) of 64 bytes to its default value. You can display the maximum and current data rates and the scalar value set by the radio in the show VMI neighbor detail command output.

QoS provisioning on PPPoE extension session

This example describes QoS provisioning on PPPoE extension session.

policy-map rar_policer
 class class-default
  police 10000 2000 1000 conform-action transmit  exceed-action drop  violate-action drop
policy-map rar_shaper
 class class-default
  shape average percent 1
 
interface Virtual-Template2
 ip address 92.92.2.1 255.255.255.0
 no peer default ip address
 no keepalive
 service-policy input rar_policer
end

Configure the RAR feature in bypass mode

This task configures the RAR feature in bypass mode to provide radio-aware routing capabilities with Point-to-Point Protocol over Ethernet (PPPoE) services.

This configuration enables end-to-end RAR functionality in bypass mode. Before beginning the RAR configuration, you must first configure the subscriber authorization enable command to bring up the RAR session. Without enabling authorization, the Point-to-Point protocol does not recognize this as a RAR session and may not tag manet_radio in presentation of a PPPoE Active Discovery Initiate (PADI). By default, bypass mode does not appear in the configuration. It appears only if the mode is configured as bypass.

Procedure


Step 1

Configure a service for RAR.

Example:

policy-map type service rar-lab 
 pppoe service manet_radio //note: Enter the pppoe service policy name as manet_radio
!

Step 2

Configure broadband settings.

Example:

bba-group pppoe VMI2
 virtual-template 2
service profile rar-lab 
!
interface GigabitEthernet0/0/0
 description Connected to Client1
  negotiation auto
  pppoe enable group VMI2
!

Step 3

Configure the virtual template for bypass mode using one of the following options.

  • IP Address Configured under Virtual-Template Explicitly


    interface Virtual-Template2
    ip address 192.168.90.3 255.255.255.0
    no ip redirects
    peer default ip address pool PPPoEpool2
    ipv6 enable
    ospfv3 1 network manet
    ospfv3 1 ipv4 area 0
    ospfv3 1 ipv6 area 0
    no keepalive
    service-policy input rar_policer Or/And
    service-policy output rar_shaper
    
  • VMI Unnumbered Configured under Virtual Template

    
    interface Virtual-Template2
    ip unnumbered vmi2
    no ip redirects
    peer default ip address pool PPPoEpool2 
    ipv6 enable
    ospfv3 1 network manet
    ospfv3 1 ipv4 area 0
    ospfv3 1 ipv6 area 0
    no keepalive
    service-policy input rar_policer Or/And
    service-policy output rar_shaper
    

Step 4

Configure the virtual multipoint interface in bypass mode.

Example:


interface vmi2 //configure the virtual multi interface
ip address 192.168.2.1 255.255.255.0
physical-interface GigabitEthernet0/0/0
mode bypass     

Step 5

Configure OSPF routing.

Example:

router ospfv3 1
 router-id 1.1.1.1
!
 address-family ipv4 unicast
  redistribute connected metric 1 metric-type 1
  log-adjacency-changes
 exit-address-family
 !
 address-family ipv6 unicast
  redistribute connected metric-type 1
  log-adjacency-changes
 exit-address-family
!
ip local pool PPPoEpool2 192.168.2.3 192.168.2.254

The RAR feature is configured in bypass mode with PPPoE services, virtual template interfaces, and OSPF routing enabled for radio-aware routing functionality.

Verifying RAR Session Details

Use the provided show commands to monitor PPPoE session packets, VMI counters, neighbor details, and platform-specific hardware information for troubleshooting and verification.

Router#show pppoe session packets all
Total PPPoE sessions 2
session id: 9
local MAC address: 006b.f10e.a5e0, remote MAC address: 0050.56bc.424a
virtual access interface: Vi2.1, outgoing interface: Gi0/0/0
1646 packets sent, 2439363 received
176216 bytes sent, 117250290 received
PPPoE Flow Control Stats
Local Credits: 65535   Peer Credits: 65535   Local Scaling Value 64 bytes
Credit Grant Threshold: 28000    Max Credits per grant: 65535
Credit Starved Packets: 0
PADG xmit Seq Num: 32928     PADG Timer index: 0
PADG last rcvd Seq Num: 17313
PADG last nonzero Seq Num: 17306
PADG last nonzero rcvd amount: 2
PADG Timers: (ms)   [0]-1000    [1]-2000    [2]-3000    [3]-4000    [4]-5000
PADG xmit: 33308  rcvd: 17313
PADC xmit: 17313  rcvd: 19709
In-band credit pkt xmit: 7 rcvd: 2434422
Last credit packet snapshot
PADG xmit: seq_num = 32928, fcn = 0, bcn = 65535
PADC rcvd: seq_num = 32928, fcn = 65535, bcn = 65535
PADG rcvd: seq_num = 17313, fcn = 0, bcn = 65535
PADC xmit: seq_num = 17313, fcn = 65535, bcn = 65535
In-band credit pkt xmit: fcn = 61, bcn = 65533
In-band credit pkt rcvd: fcn = 0, bcn = 65534
==== PADQ Statistics ====
PADQ xmit: 0  rcvd: 0
session id: 10
local MAC address: 006b.f10e.a5e1, remote MAC address: 0050.56bc.7dcb
virtual access interface: Vi2.2, outgoing interface: Gi0/0/1
1389302 packets sent, 1852 received
77869522 bytes sent, 142156 received
PPPoE Flow Control Stats
Local Credits: 65535   Peer Credits: 65535   Local Scaling Value 64 bytes
Credit Grant Threshold: 28000    Max Credits per grant: 65535
Credit Starved Packets: 0
PADG xmit Seq Num: 18787     PADG Timer index: 0
PADG last rcvd Seq Num: 18784
PADG last nonzero Seq Num: 18768
PADG last nonzero rcvd amount: 2
PADG Timers: (ms)   [0]-1000    [1]-2000    [2]-3000    [3]-4000    [4]-5000
PADG xmit: 18787  rcvd: 18784
PADC xmit: 18784  rcvd: 18787
In-band credit pkt xmit: 1387764 rcvd: 956
Last credit packet snapshot
PADG xmit: seq_num = 18787, fcn = 0, bcn = 65535
PADC rcvd: seq_num = 18787, fcn = 65535, bcn = 65535
PADG rcvd: seq_num = 18784, fcn = 0, bcn = 65535
PADC xmit: seq_num = 18784, fcn = 65535, bcn = 65535
In-band credit pkt xmit: fcn = 0, bcn = 64222
In-band credit pkt rcvd: fcn = 0, bcn = 65534
==== PADQ Statistics ====
PADQ xmit: 0  rcvd: 1
Router#show pppoe session packets 
Total PPPoE sessions 2
SID     Pkts-In         Pkts-Out        Bytes-In        Bytes-Out
9       2439391         1651            117252098       176714
10      1858            1389306         142580          77869914
Router#show vmi counters 
Interface vmi2: - Last Clear Time =                               
Input Counts:
  Process Enqueue      =          0 (VMI)
  Fastswitch           =          0      
  VMI Punt Drop:                         
       Queue Full      =          0      
Output Counts:
  Transmit:   
       VMI Process DQ  =       4280
       Fastswitch VA   =          0
       Fastswitch VMI  =          0
  Drops:                           
       Total           =          0
       QOS Error       =          0
       VMI State Error =          0
       Mcast NBR Error =          0
       Ucast NBR Error =          0
Interface vmi3: - Last Clear Time = 
Input Counts:
  Process Enqueue      =          0 (VMI)
  Fastswitch           =          0
  VMI Punt Drop:
       Queue Full      =          0
Output Counts:
  Transmit:
       VMI Process DQ  =       2956
       Fastswitch VA   =          0
       Fastswitch VMI  =          0
  Drops:
       Total           =          0
       QOS Error       =          0
       VMI State Error =          0
       Mcast NBR Error =          0
       Ucast NBR Error =          0
Interface vmi4: - Last Clear Time =
Input Counts:
  Process Enqueue      =          0 (VMI)
  Fastswitch           =          0
  VMI Punt Drop:
       Queue Full      =          0
Output Counts:
  Transmit:
       VMI Process DQ  =          0
       Fastswitch VA   =          0
       Fastswitch VMI  =          0
  Drops:
       Total           =          0
       QOS Error       =          0
       VMI State Error =          0
       Mcast NBR Error =          0
       Ucast NBR Error =          0
Router#
Router#show vmi neighbor details 
1 vmi2 Neighbors
1 vmi3 Neighbors
0 vmi4 Neighbors
2 Total Neighbors
vmi2   IPV6 Address=FE80::21E:E6FF:FE43:F500
       IPV6 Global Addr=::                  
       IPV4 Address=92.92.2.2, Uptime=05:15:01
       Output pkts=89, Input pkts=0           
       No Session Metrics have been received for this neighbor.
       Transport PPPoE, Session ID=9                           
       INTERFACE STATS:                                        
          VMI Interface=vmi2,                                  
             Input qcount=0, drops=0, Output qcount=0, drops=0 
          V-Access intf=Virtual-Access2.1,                     
             Input qcount=0, drops=0, Output qcount=0, drops=0 
          Physical intf=GigabitEthernet0/0/0,                  
             Input qcount=0, drops=0, Output qcount=0, drops=0 
PPPoE Flow Control Stats
 Local Credits: 65535   Peer Credits: 65535   Local Scaling Value 64 bytes
 Credit Grant Threshold: 28000    Max Credits per grant: 65535            
 Credit Starved Packets: 0                                                
 PADG xmit Seq Num: 33038     PADG Timer index: 0                         
 PADG last rcvd Seq Num: 17423                                            
 PADG last nonzero Seq Num: 17420                                         
 PADG last nonzero rcvd amount: 2                                         
 PADG Timers: (ms)   [0]-1000    [1]-2000    [2]-3000    [3]-4000    [4]-5000 
 PADG xmit: 33418  rcvd: 17423                                                
 PADC xmit: 17423  rcvd: 19819                                                
 In-band credit pkt xmit: 7 rcvd: 2434446                                     
 Last credit packet snapshot                                                  
  PADG xmit: seq_num = 33038, fcn = 0, bcn = 65535                            
  PADC rcvd: seq_num = 33038, fcn = 65535, bcn = 65535                        
  PADG rcvd: seq_num = 17423, fcn = 0, bcn = 65535                            
  PADC xmit: seq_num = 17423, fcn = 65535, bcn = 65535                        
  In-band credit pkt xmit: fcn = 61, bcn = 65533                              
  In-band credit pkt rcvd: fcn = 0, bcn = 65534                               
    ==== PADQ Statistics ====                                                 
     PADQ xmit: 0  rcvd: 0                                                    
vmi3   IPV6 Address=FE80::21E:7AFF:FE68:6100
       IPV6 Global Addr=::                  
       IPV4 Address=91.91.91.4, Uptime=05:14:55
       Output pkts=6, Input pkts=0             
       METRIC DATA: Total rcvd=1, Avg arrival rate (ms)=0
          CURRENT: MDR=128000 bps, CDR=128000 bps        
                   Lat=0 ms, Res=100, RLQ=100, load=0    
          MDR      Max=128000 bps, Min=128000 bps, Avg=128000 bps
          CDR      Max=128000 bps, Min=128000 bps, Avg=128000 bps
          Latency  Max=0, Min=0, Avg=0 (ms)
          Resource Max=100%, Min=100%, Avg=100%
          RLQ      Max=100, Min=100, Avg=100
          Load     Max=0%, Min=0%, Avg=0%
       Transport PPPoE, Session ID=10
       INTERFACE STATS:
          VMI Interface=vmi3,
             Input qcount=0, drops=0, Output qcount=0, drops=0
          V-Access intf=Virtual-Access2.2,
             Input qcount=0, drops=0, Output qcount=0, drops=0
          Physical intf=GigabitEthernet0/0/1,
             Input qcount=0, drops=0, Output qcount=0, drops=0
PPPoE Flow Control Stats
 Local Credits: 65535   Peer Credits: 65535   Local Scaling Value 64 bytes
 Credit Grant Threshold: 28000    Max Credits per grant: 65535
 Credit Starved Packets: 0
 PADG xmit Seq Num: 18896     PADG Timer index: 0
 PADG last rcvd Seq Num: 18894
 PADG last nonzero Seq Num: 18884
 PADG last nonzero rcvd amount: 2
 PADG Timers: (ms)   [0]-1000    [1]-2000    [2]-3000    [3]-4000    [4]-5000
 PADG xmit: 18896  rcvd: 18894
 PADC xmit: 18894  rcvd: 18896
 In-band credit pkt xmit: 1387764 rcvd: 961
 Last credit packet snapshot
  PADG xmit: seq_num = 18896, fcn = 0, bcn = 65535
  PADC rcvd: seq_num = 18896, fcn = 65535, bcn = 65535
  PADG rcvd: seq_num = 18894, fcn = 0, bcn = 65535
  PADC xmit: seq_num = 18894, fcn = 65535, bcn = 65535
  In-band credit pkt xmit: fcn = 0, bcn = 64222
  In-band credit pkt rcvd: fcn = 0, bcn = 65534
    ==== PADQ Statistics ====
     PADQ xmit: 0  rcvd: 1
Router#show vmi neighbor details vmi 2
              1 vmi2 Neighbors      
vmi2   IPV6 Address=FE80::21E:E6FF:FE43:F500
       IPV6 Global Addr=::
       IPV4 Address=92.92.2.2, Uptime=05:16:03
       Output pkts=89, Input pkts=0
       No Session Metrics have been received for this neighbor.
       Transport PPPoE, Session ID=9
       INTERFACE STATS:
          VMI Interface=vmi2,
             Input qcount=0, drops=0, Output qcount=0, drops=0
          V-Access intf=Virtual-Access2.1,
             Input qcount=0, drops=0, Output qcount=0, drops=0
          Physical intf=GigabitEthernet0/0/0,
             Input qcount=0, drops=0, Output qcount=0, drops=0
PPPoE Flow Control Stats
 Local Credits: 65535   Peer Credits: 65535   Local Scaling Value 64 bytes
 Credit Grant Threshold: 28000    Max Credits per grant: 65535
 Credit Starved Packets: 0
 PADG xmit Seq Num: 33100     PADG Timer index: 0
 PADG last rcvd Seq Num: 17485
 PADG last nonzero Seq Num: 17449
 PADG last nonzero rcvd amount: 2
 PADG Timers: (ms)   [0]-1000    [1]-2000    [2]-3000    [3]-4000    [4]-5000
 PADG xmit: 33480  rcvd: 17485
 PADC xmit: 17485  rcvd: 19881
 In-band credit pkt xmit: 7 rcvd: 2434460
 Last credit packet snapshot
  PADG xmit: seq_num = 33100, fcn = 0, bcn = 65535
  PADC rcvd: seq_num = 33100, fcn = 65535, bcn = 65535
  PADG rcvd: seq_num = 17485, fcn = 0, bcn = 65535
  PADC xmit: seq_num = 17485, fcn = 65535, bcn = 65535
  In-band credit pkt xmit: fcn = 61, bcn = 65533
  In-band credit pkt rcvd: fcn = 0, bcn = 65534
    ==== PADQ Statistics ====
     PADQ xmit: 0  rcvd: 0
Router#show platform hardware qfp active feature ess session
Current number sessions: 2
Current number TC flow: 0
Feature Type: A=Accounting D=Policing(DRL) F=FFR M=DSCP Marking L=L4redirect P=Portbundle T=TC
   Session    Type      Segment1      SegType1      Segment2      SegType2 Feature Other
----------------------------------------------------------------------------------------
        21     PPP 0x0000001500001022    PPPOE 0x0000001500002023    LTERM -------
        24     PPP 0x0000001800003026    PPPOE 0x0000001800004027    LTERM -------
Router#show platform software subscriber pppoe_fctl evsi 21
PPPoE Flow Control Stats
 Local Credits: 65535   Peer Credits: 65535   Local Scaling Value 64 bytes
 Credit Grant Threshold: 28000    Max Credits per grant: 65535
 Credit Starved Packets: 0
 PADG xmit Seq Num: 33215     PADG Timer index: 0
 PADG last rcvd Seq Num: 17600
 PADG last nonzero Seq Num: 17554
 PADG last nonzero rcvd amount: 2
 PADG Timers: (ms)   [0]-1000    [1]-2000    [2]-3000    [3]-4000    [4]-5000
 PADG xmit: 33595  rcvd: 17600
 PADC xmit: 17600  rcvd: 19996
 In-band credit pkt xmit: 7 rcvd: 2434485
 Last credit packet snapshot
  PADG xmit: seq_num = 33215, fcn = 0, bcn = 65535
  PADC rcvd: seq_num = 33215, fcn = 65535, bcn = 65535
  PADG rcvd: seq_num = 17600, fcn = 0, bcn = 65535
  PADC xmit: seq_num = 17600, fcn = 65535, bcn = 65535
  In-band credit pkt xmit: fcn = 61, bcn = 65533
  In-band credit pkt rcvd: fcn = 0, bcn = 65534
BQS buffer statistics
 Current packets in BQS buffer: 0
 Total en-queue packets: 0 de-queue packets: 0
 Total dropped packets: 0
Internal flags: 0x0
Router#show platform hardware qfp active feature ess session id 21
Session ID: 21
  EVSI type: PPP
  SIP Segment ID: 0x1500001022
  SIP Segment type: PPPOE
  FSP Segment ID: 0x1500002023
  FSP Segment type: LTERM
  QFP if handle: 16
  QFP interface name: EVSI21
  SIP TX Seq num: 0
  SIP RX Seq num: 0
  FSP TX Seq num: 0
  FSP RX Seq num: 0
  Condition Debug: 0x00000000
    session
Router#show ospfv3 neighbor
          OSPFv3 1 address-family ipv4 (router-id 3.3.3.3)
Neighbor ID     Pri   State           Dead Time   Interface ID    Interface
1.1.1.1           0   FULL/  -        00:01:32    19              Virtual-Access2.1
          OSPFv3 1 address-family ipv6 (router-id 3.3.3.3)
Neighbor ID     Pri   State           Dead Time   Interface ID    Interface
1.1.1.1           0   FULL/  -        00:01:52    19              Virtual-Access2.1
Router#
Router#show ip route 
Codes: L - local, C - connected, S - static, R - RIP, M - mobile, B - BGP
D - EIGRP, EX - EIGRP external, O - OSPF, IA - OSPF inter area 
N1 - OSPF NSSA external type 1, N2 - OSPF NSSA external type 2
E1 - OSPF external type 1, E2 - OSPF external type 2
i - IS-IS, su - IS-IS summary, L1 - IS-IS level-1, L2 - IS-IS level-2
ia - IS-IS inter area, * - candidate default, U - per-user static route
o - ODR, P - periodic downloaded static route, H - NHRP, l - LISP
a - application route
+ - replicated route, % - next hop override, p - overrides from PfR
Gateway of last resort is not set
      90.0.0.0/8 is variably subnetted, 3 subnets, 2 masks
C        90.90.90.0/24 is directly connected, Virtual-Access2.1
O        90.90.90.4/32 [110/1] via 90.90.90.4, 00:00:03, Virtual-Access2.1
L        90.90.90.5/32 is directly connected, Virtual-Access2.1
      92.0.0.0/32 is subnetted, 1 subnets
C        92.92.2.21 is directly connected, Virtual-Access2.1
DLEP

Cisco Dynamic Link Exchange Protocol (DLEP) is a protocol in the Radio Aware Routing (RAR) family that addresses the challenges faced when merging IP routing and radio frequency (RF) communications.

DLEP capabilities

Cisco provides capabilities that enable:

  • Optimal route selection based on feedback from radios

  • Faster convergence when nodes join and leave the network

  • Efficient integration of point-to-point, point-to-multipoint and broadcast multi-access radio topologies with multi-hop routing

  • Flow-controlled communications between the radio and its partner router using rate-based Quality of Service (QoS) policies

  • Dynamic shaping of fluctuating RF bandwidth in near real time to provide optimized use of actual RF bandwidth

DLEP topology and packet flow

DLEP topology and packet flow is a communication mechanism that

  • enables radios to communicate link quality information to routers in real-time

  • allows routing metrics to be adjusted dynamically to favor the best path, and

  • supports multiple packet flow scenarios through virtual interfaces in IOS-XE platforms.

DLEP topology characteristics

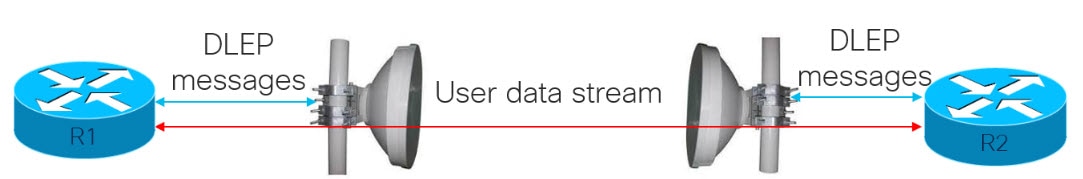
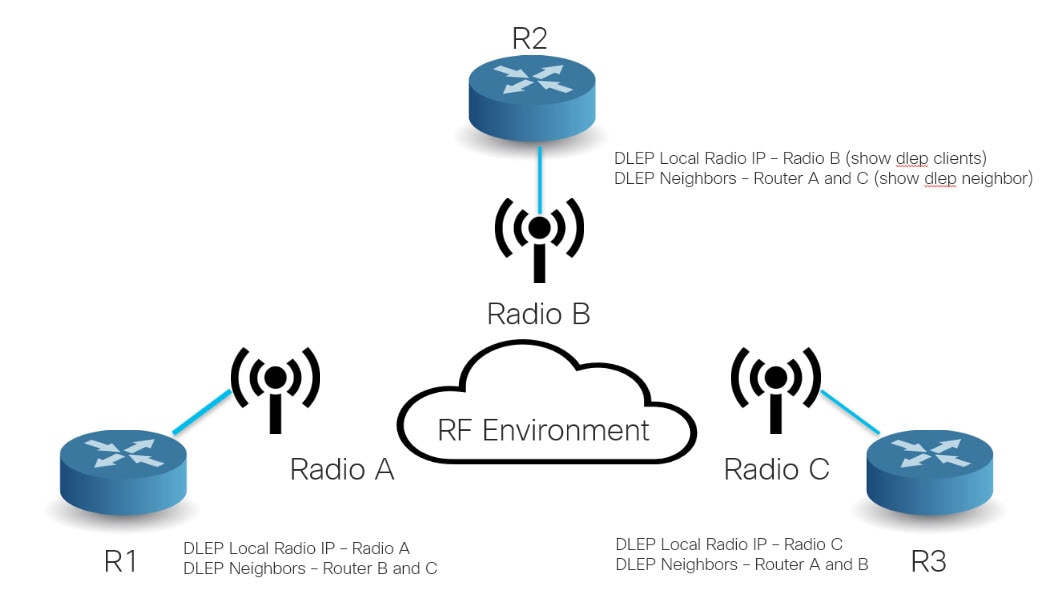
The DLEP exchange between the router and radio allows the radio to tell the router about the link quality. This is somewhat analogous to the way the bar icon on your cell phone tells you about your Wi-Fi or LTE signal quality.

The DLEP topology diagram illustrates the communication flow between radios and routers, highlighting how link quality information is exchanged in real-time to optimize routing metrics and support various packet flow scenarios.

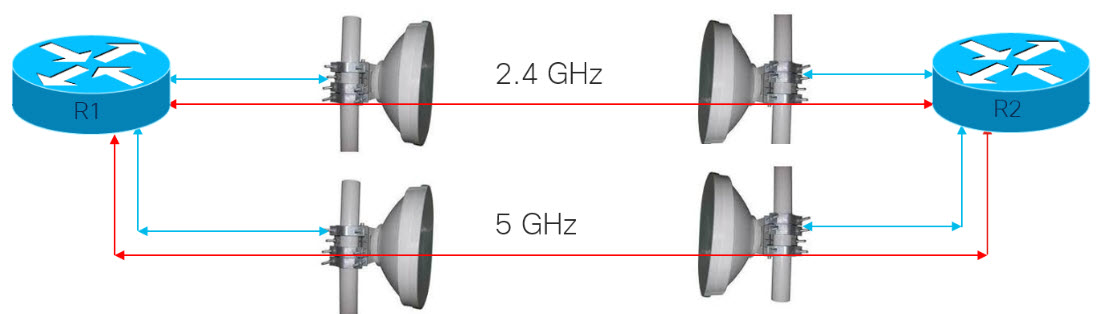
With DLEP, we can make use of routing distances with equal cost, where metrics are updated based in real time based on best path.

Without DLEP, there are two equal cost paths to any unadjusted routing protocol. With DLEP, routing metrics can be adjusted in real-time to favor the best path.

The DLEP topology diagram illustrates the packet flow between the router and radio, highlighting how link quality information is exchanged to optimize routing metrics in real-time.

Note


Atmospheric conditions and interference will ultimately favor one band versus the other.


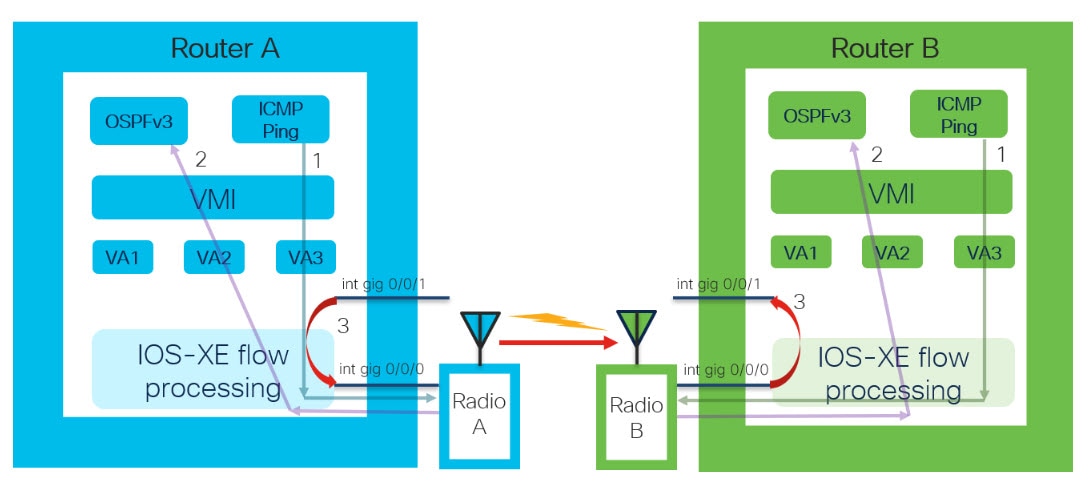
DLEP packet flow includes three different scenarios:

  • Packet sent from IOS-XE to the DLEP neighbor (radio)

  • Packet sent from DLEP neighbor (radio) to IOS-XE

  • Non-DLEP traffic passing between the ESR-6300 Layer 3 (WAN) interfaces, for example, user traffic

IOS-XE platform interfaces include:

  • Virtual Multipoint Interface (VMI): The VMI interface acts as an umbrella interface for all virtual access interfaces, which is used for routing protocols such as OSPFv3 and EIGRP. Routing protocols, for example OSPFv3, see a single VMI interface instead of all VA interfaces. This helps reduce routing table size without impacting the integrity of network.

  • Virtual Template (VT): Virtual Template serves as the template for every Virtual Access interface.

  • Virtual Access (VA) interface: One VA is created for each DLEP Neighbor (Radio) discovered.

  • Underlaying physical Layer 3 WAN interface (Gi 0/0/0 and Gi 0/0/1), or even sub-interface (Gi 0/0/0.2 or Gi0/0/1.2

This diagram describes the packet flow:

The diagram illustrates the DLEP topology and packet flow, showing the relationship between the Virtual Template, Virtual Access interfaces, and the underlying physical Layer 3 WAN interfaces.

Item

Description

1

Packet sent from IOS-XE to DLEP neighbor (to Radio): packet with DST MAC of neighbor MAC, neighbor IP sent out from DLEP Physical interface.

2

DLEP Packet (from radio) received thru DLEP Physical interface to IOS-XE: packet needs to be delivered to IOS routing protocol marked as from VMI interface.

3

End to End user data.

DLEP communication analogy

The DLEP exchange between the router and radio is somewhat analogous to the way the bar icon on your cell phone tells you about your Wi-Fi or LTE signal quality.

License requirements

The Cisco Dynamic Link Exchange Protocol (DLEP) feature requires the Network Advantage license.

Configuring DLEP with OSPFv3

Configuring DLEP with OSPFv3 is a network configuration process that

  • initiates, verifies, and manages all aspects of Dynamic Link Exchange Protocol (DLEP) on an interface

  • requires configuration of physical interfaces, VMI interfaces, and Virtual Templates, and

  • must include VMI and Virtual-Template configuration before attaching a Virtual-Template to a physical interface.

DLEP interface configuration requirements

DLEP uses these interfaces that need to be configured:

  • Physical interface

  • VMI interface

  • Virtual Templates


Important


Before attaching a Virtual-Template to a physical interface, you need to configure the VMI and Virtual-Template. See this example of the error you receive:


Router(config)#int gi0/0/0
Router(config-if)#ip dlep vtemplate 1
DLEP: ERROR. A valid VMI and Virtual Template MUST be present before configurating ip dlep
DLEP: ERROR. An Interface IP address MUST be specified for DLEP.

Configure the virtual multipoint interface

Use this task to configure virtual multipoint interfaces (VMIs) to aggregate the virtual access interfaces created by DLEP sessions and to enable routing protocol support.

By default, VMIs operate in aggregate mode, which means that all the virtual access interfaces created by DLEP sessions are aggregated logically under the configured VMI. Applications above Layer 2, such as Enhanced Interior Gateway Routing Protocol (EIGRP) and Open Shortest Path First version 3 (OSPFv3), must be defined only on the VMI. Packets sent to the VMI are forwarded to the correct virtual access interface.

Procedure


Step 1

Use the configure terminal command to enter the global configuration mode.

Example:

Router# configure terminal
                        Enter configuration commands, one per line.  End with CNTL/Z.
                        Router(config)#

Step 2

Use the interface vmi number command to create a VMI and enter interface configuration mode.

This example creates vmi1.

Example:

Router(config)# interface vmi 1
                        Router(config-if)#

Step 3

Use the ip unnumbered interface command to configure the VMI to use the IP address of the physical interface.

Example:

Router(config-if)# ip unnumbered gigabitEthernet 0/0/0

Step 4

Use the physical-interface interface command to bind the physical interface to the VMI for packet flow.

Example:

Router(config-if)# physical-interface gigabitEthernet 0/0/0

Step 5

Use the ipv6 enable command to enable IPv6 support on the VMI.

OSPFv3 IPv4 requires IPv6 support to be enabled at the interface level.

Example:

Router(config-if)# ipv6 enable

Step 6

Use the ospfv3 process-id ipv4 area area-id command to enable the VMI to participate in OSPFv3 or EIGRP routing.

Example:

Router(config-if)# ospfv3 1 ipv4 area 0

Step 7

Use the exit command to exit interface configuration mode and return to global configuration mode.

Example:

Router(config-if)# exit
Router(config)#

Step 8

Use the router ospfv3 process-id command to enter the global configuration for OSPFv3.

Example:

Router(config)# router ospfv3 1

Step 9

Use the address-family ipv4 unicast command to add the address family for IPv4 unicast routing under the global OSPFv3 configuration.

Example:

Router(config-router)# address-family ipv4 unicast
Router(config-router-af)#

The virtual multipoint interface is configured and enabled for routing protocols, allowing DLEP sessions to create virtual access interfaces that are aggregated under the VMI.

Configure the virtual template

Use this task to create the DLEP virtual template that enables Dynamic Link Exchange Protocol (DLEP) functionality on the router interface. DLEP configuration requires a virtual template to be defined for proper operation.

Procedure


Step 1

Use the enable command to enter the privileged EXEC mode. Enter your password if prompted.

Example:

Router> enable
Router#

Step 2

Use the configure terminal command to enter the global configuration mode.

Example:

Router# configure terminal
Enter configuration commands, one per line.  End with CNTL/Z.
Router(config)#

Step 3

Use the interface Virtual-Template number command to create the virtual template interface and enter interface configuration mode.

You must use the same virtual template interface when you configure DLEP on the physical interface.

Example:

Router(config)# interface Virtual-Template 1
Router(config-if)#

Step 4

Use the ip unnumbered interface command to configure the virtual template interface to use the IP address of the physical interface.

Example:

Router(config-if)# ip unnumbered gigabitEthernet 0/0/0

Step 5

Use the ipv6 enable command to enable IPv6 support on the virtual template interface.

OSPFv3 IPv4 requires IPv6 support to be enabled at the interface level.

Example:

Router(config-if)# ipv6 enable

Step 6

Use the exit command to exit interface configuration mode and return to global configuration mode.

Example:

Router(config-if)# exit
Router(config)#

The virtual template interface is configured and ready for DLEP configuration on the physical interface.

Configure the physical interface

Before you begin

Before you attach a DLEP template to a WAN interface, configure a physical IP address and create the VMI and virtual template interfaces.

Use this task to enable Dynamic Link Exchange Protocol (DLEP) functionality on a physical WAN interface by applying the necessary configuration commands and attaching a DLEP template.

DLEP configuration is currently supported on the WAN interface of IOS XE platforms. You must configure both the VMI and the virtual template interface before you configure the physical interface. You can attach the DLEP configuration to the WAN interface in several ways. The following are some examples:

  • DLEP template with a well-known IP address (recommended)

  • DLEP template with TCP or UDP ports configured between the server (router) and the client (radio)

  • DLEP template with a dynamic port on the server (router)

  • DLEP template attached in discovery mode

For each of these four modes, you also have the option to enable Generalized TTL Security Mechanism (GTSM).

Procedure


Step 1

Use the configure terminal command to enter the global configuration mode.

Example:

Router# configure terminal
Enter configuration commands, one per line.  End with CNTL/Z.
Router(config)#

Step 2

Use the interface type number command to enter interface configuration mode for the WAN interface.

Example:

Router(config)# interface gigabitEthernet 0/0/0
Router(config-if)#

Step 3

Use the ipv6 enable command to enable IPv6 support at the interface level.

Example:

Router(config-if)# ipv6 enable

Step 4

Use the ip address ip-address subnet-mask command to assign a physical IP address to the WAN interface.

Example:

Router(config-if)# ip address 10.0.0.1 255.255.255.0

Step 5

Use the ip dlep vtemplate number command to attach the DLEP template to the WAN interface in discovery mode.

The other configuration examples are described separately.

Example:

Router(config-if)# ip dlep vtemplate 1

Step 6

Use the no shutdown command to bring up the interface.

Example:

Router(config-if)# no shutdown

Step 7

Use the exit command to exit interface configuration mode and return to global configuration mode.

Example:

Router(config-if)# exit

The physical interface is configured with DLEP support, and the DLEP template is attached to the WAN interface. The interface is enabled and ready for DLEP communication.

DLEP configuration modes

DLEP configuration modes are attachment methods that enable DLEP virtual templates to be connected to different router interface types in various operational configurations.

Configuration requirements

DLEP virtual templates can be attached in different modes to the WAN or sub-interface of the router.


Note


You must have VMI and Virtual-Templates already configured prior to continuing with any of the configuration modes in this section.


Configure the DLEP client and server based on port number

Use this task to configure the DLEP server and client UDP and TCP ports to enable proper communication between the router and radio devices with custom port assignments.

DLEP (Dynamic Link Exchange Protocol) is used for dynamic link management between routers and radio devices. By default, DLEP uses standard ports, but you may need to configure custom ports for specific network requirements or to avoid port conflicts.

In this example, you configure the DLEP server, and the client UDP and TCP ports.

Procedure


Step 1

Use these steps to configure the interface with IP addressing and DLEP parameters:

  1. Use the interface type number command to enter interface configuration mode for the specified interface.

    Example:

    Router(config)# interface gi0/0/0
  2. Use the ip address ip-address subnet-mask command to assign an IP address and subnet mask to the interface.

    Example:

    Router(config-if)# ip address 10.0.0.1 255.255.255.0
  3. Use the ipv6 enable command to enable IPv6 processing on the interface.

    Example:

    Router(config-if)# ipv6 enable
  4. Use the ip dlep vtemplate number port udp-port tcp port tcp-port client ip ip-address port client-port command to attach the DLEP virtual template to the interface and specify the server and client port numbers.

    Example:

    Router(config-if)# ip dlep vtemplate 1 port 11113 tcp port 11114 client ip 10.0.0.3 port 11115
  5. Use the no shutdown command to enable the interface.

    Example:

    Router(config-if)# no shutdown

In this DLEP configuration, the server (router) listens on UDP port 11113 and TCP port 11114, and the client (radio) listens on TCP port 11115. The UDP port of the client is 854 by default.

Step 2

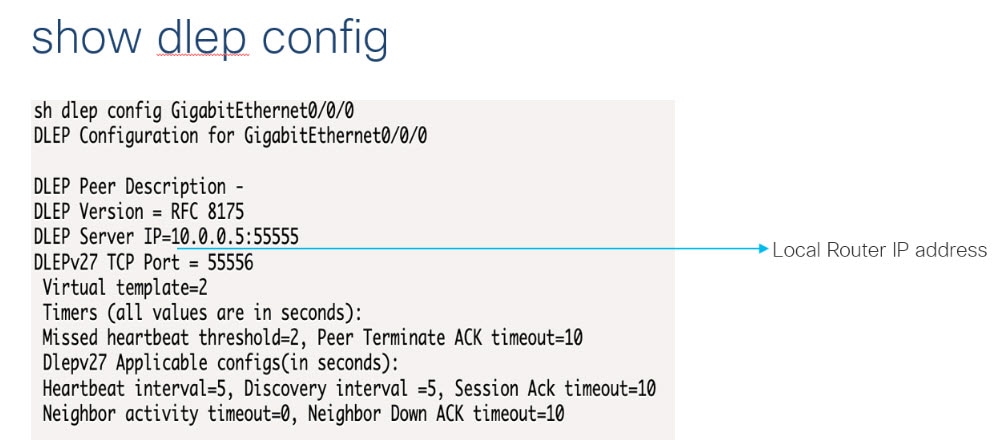
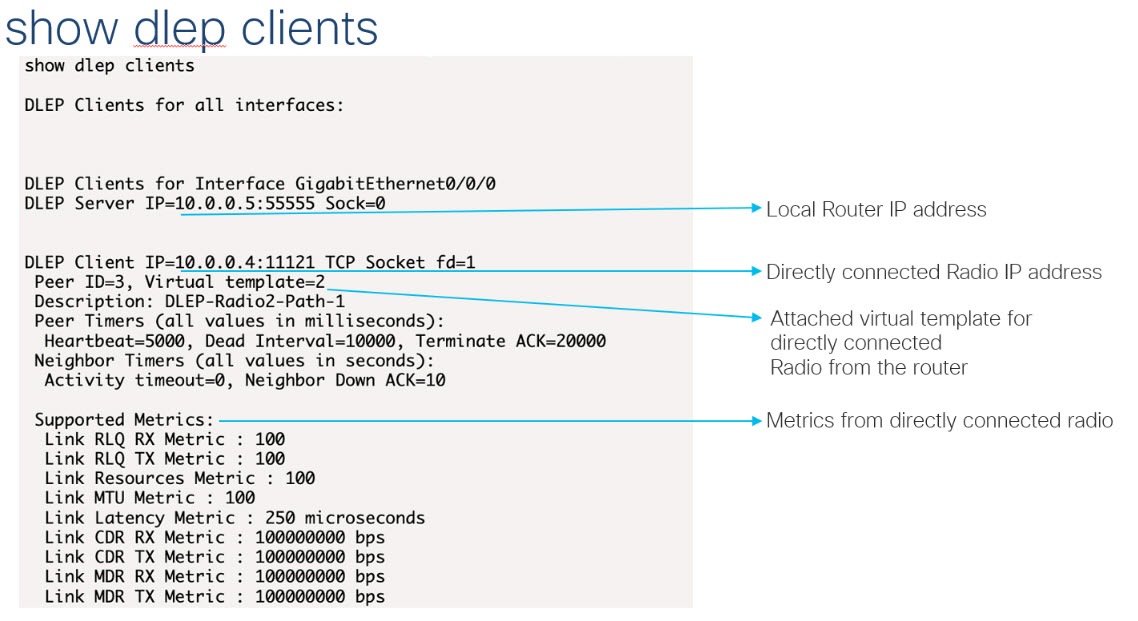
Use the show dlep clients command to validate the configuration.

Example:

Router# show dlep clients
DLEP Clients for all interfaces:

DLEP Clients for Interface GigabitEthernet0/0/0
DLEP Server IP=10.0.0.1:11113 Sock=0

DLEP Client IP=10.0.0.3:11115 TCP Socket fd=1
Peer ID=1, Virtual template=1
Description: DLEP-Radio1-Path-1
Peer Timers (all values in milliseconds):
Heartbeat=5000, Dead Interval=10000, Terminate ACK=20000
Neighbor Timers (all values in seconds):
Activity timeout=0, Neighbor Down ACK=10

Supported Metrics:
Link RLQ RX Metric : 100
Link RLQ TX Metric : 100
Link Resources Metric : 100
Link MTU Metric : 100
Link Latency Metric : 250 microseconds
Link CDR RX Metric : 100000000 bps
Link CDR TX Metric : 100000000 bps
Link MDR RX Metric : 100000000 bps
Link MDR TX Metric : 100000000 bps

The DLEP server and client are configured with custom port numbers, and the configuration is validated, displaying the established connection and supported metrics between the router and radio device.

Configure DLEP with dynamic port on server (router)

Configure DLEP server and client communication settings to establish proper connectivity between the router (server) and radio (client) with specific port configurations.

In this configuration, you are setting up the DLEP server where the server (router) listens on default UDP/TCP ports while the client (radio) listens on a specific TCP port.

Procedure


Step 1

Configure the interface with IP address and DLEP settings.

Example:

Router(config)#interface gi0/0/0
Router(config-if)# ip address 10.0.0.1 255.255.255.0
Router(config-if)# ipv6 enable
Router(config-if)# ip dlep vtemplate 1 client ip 10.0.0.3 port 11115
Router(config-if)# no shutdown

DLEP configuration where server (router) is listening to default UDP/TCP ports. Whereas client (radio) is listening to TCP port 11115. UDP port of client is by default on 854.

Step 2

Validate the configuration using the show DLEP clients command.

Example:

Router# show dlep clients
DLEP Clients for all interfaces:

DLEP Clients for Interface GigabitEthernet0/0/0
DLEP Server IP=10.0.0.1:55555 Sock=0

DLEP Client IP=10.0.0.3:11115 TCP Socket fd=1
Peer ID=1, Virtual template=1
 Description: DLEP-Radio1-Path-1
Peer Timers (all values in milliseconds):
Heartbeat=5000, Dead Interval=10000, Terminate ACK=20000
Neighbor Timers (all values in seconds):
Activity timeout=0, Neighbor Down ACK=10

Supported Metrics:
Link RLQ RX Metric : 100
Link RLQ TX Metric : 100
Link Resources Metric : 100
Link MTU Metric : 100
Link Latency Metric : 250 microseconds
Link CDR RX Metric : 100000000 bps
Link CDR TX Metric : 100000000 bps
Link MDR RX Metric : 100000000 bps
Link MDR TX Metric : 100000000 bps

Step 3

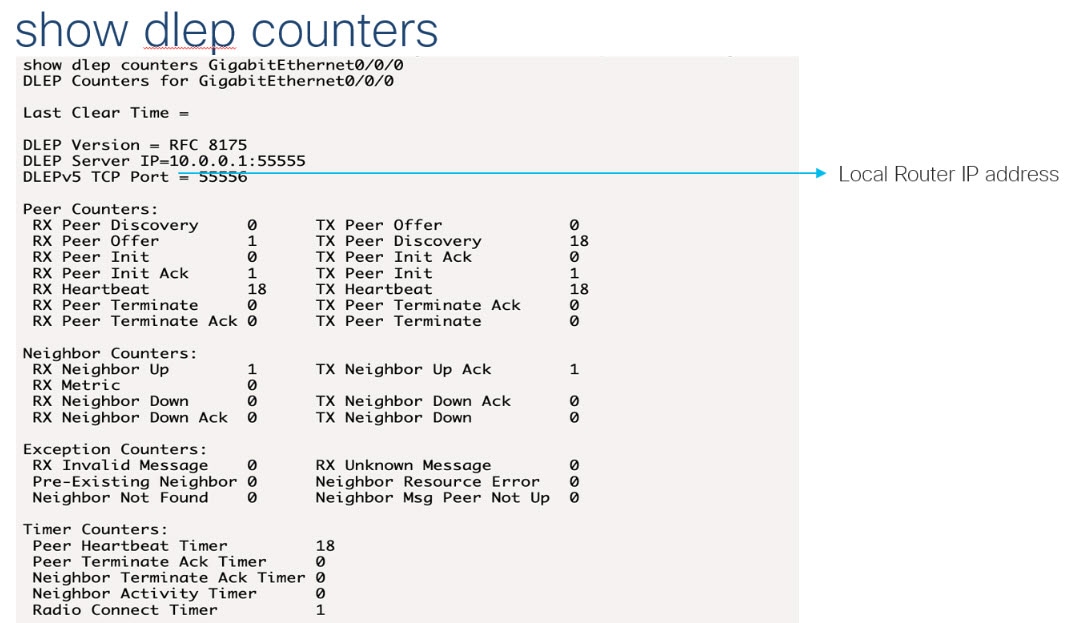
Validate the configuration using the show DLEP counters command.

Example:

Router# show dlep counters
DLEP Counters for GigabitEthernet0/0/0

Last Clear Time = 

DLEP Version = RFC 8175
DLEP Server IP=10.0.0.1:55555
DLEPv5 TCP Port = 55556

Peer Counters:
RX Peer Discovery     0      TX Peer Offer             0     
RX Peer Offer         0      TX Peer Discovery         0     
RX Peer Init          0      TX Peer Init Ack          0     
RX Peer Init Ack      1      TX Peer Init              1     
RX Heartbeat          58     TX Heartbeat              58    
RX Peer Terminate     0      TX Peer Terminate Ack     0     
RX Peer Terminate Ack 0      TX Peer Terminate         0     

Neighbor Counters:
RX Neighbor Up        0      TX Neighbor Up Ack        0     
RX Metric             0     
RX Neighbor Down      0      TX Neighbor Down Ack      0     
RX Neighbor Down Ack  0      TX Neighbor Down          0     

Exception Counters:
RX Invalid Message    0      RX Unknown Message        0     
Pre-Existing Neighbor 0      Neighbor Resource Error   0     
Neighbor Not Found    0      Neighbor Msg Peer Not Up  0     

Timer Counters:
Peer Heartbeat Timer         58    
Peer Terminate Ack Timer     0     
Neighbor Terminate Ack Timer 0     
Neighbor Activity Timer      0     
Radio Connect Timer          5     

Single Timer Wheel "Manet Infra Wheel"
Granularity      = 250 msec
Wheel size       = 4096
Spoke index      = 3592
Tick count       = 3592
Flags            = 0x00
Active timers    = 1
High water mark  = 2
Started timers   = 164
Restarted timers = 2
Cancelled timers = 3
Expired timers   = 158
Long timers      = 0
Long timer revs  = 0
Timer suspends   = 0

The DLEP configuration is complete and validated. The server (router) is listening on default UDP/TCP ports while communicating with the client (radio) on the specified TCP port 11115. The show commands confirm proper connectivity and display DLEP metrics and counters.

Attach the DLEP template in discovery mode

Use this task to configure DLEP server operation in discovery mode, enabling it to send Peer Discovery signals and establish communication with DLEP clients.

When in discovery mode, the DLEP server sends out Peer Discovery signals and waits for a Peer Offer signal from the radio.

Procedure


Step 1

Use these steps to configure the interface with the DLEP template and enable discovery mode:

  1. Use the interface type number command to enter interface configuration mode for the specified interface.

    Example:

    Router(config)# interface gi0/0/0
  2. Use the ip address ip-address subnet-mask command to assign an IP address and subnet mask to the interface.

    Example:

    Router(config-if)# ip address 10.0.0.1 255.255.255.0
  3. Use the ipv6 enable command to enable IPv6 processing on the interface.

    Example:

    Router(config-if)# ipv6 enable
  4. Use the ip dlep vtemplate number command to attach the DLEP virtual template to the interface.

    Example:

    Router(config-if)# ip dlep vtemplate 1
  5. Use the no shutdown command to enable the interface.

    Example:

    Router(config-if)# no shutdown

In this DLEP configuration, the server (router) listens on the default UDP and TCP ports.

Note

 
To receive the peer discovery messages, you must explicitly configure the UDP port on the client to 55555.

Step 2

Validate the configuration using the show dlep clients and show dlep counters commands.

  1. Use the show dlep clients command to display the DLEP client connections.

    Example:

    Router# show dlep clients
    DLEP Clients for all interfaces:
    
    DLEP Clients for Interface GigabitEthernet0/0/0
    DLEP Server IP=10.0.0.1:55555 Sock=0
    
    DLEP Client IP=10.0.0.3:11115 TCP Socket fd=1
     Peer ID=1, Virtual template=1
     Description: DLEP-Radio1-Path-1
     Peer Timers (all values in milliseconds):
      Heartbeat=5000, Dead Interval=10000, Terminate ACK=20000
     Neighbor Timers (all values in seconds):
      Activity timeout=0, Neighbor Down ACK=10
    
     Supported Metrics:
      Link RLQ RX Metric : 100
      Link RLQ TX Metric : 100
      Link Resources Metric : 100
      Link MTU Metric : 100
      Link Latency Metric : 250 microseconds
      Link CDR RX Metric : 100000000 bps
      Link CDR TX Metric : 100000000 bps
      Link MDR RX Metric : 100000000 bps
      Link MDR TX Metric : 100000000 bps
  2. Use the show dlep counters command to verify peer communication.

    Example:

    Router# show dlep counters
    DLEP Counters for GigabitEthernet0/0/0
    
    Last Clear Time =
    
    DLEP Version = RFC 8175
    DLEP Server IP=10.0.0.1:55555
    DLEPv5 TCP Port = 55556
    
    Peer Counters:
    RX Peer Discovery     0      TX Peer Offer             0
    RX Peer Offer         3      TX Peer Discovery         194
    RX Peer Init          0      TX Peer Init Ack          0
    RX Peer Init Ack      3      TX Peer Init              3
    RX Heartbeat          710    TX Heartbeat              707
    RX Peer Terminate     0      TX Peer Terminate Ack     0
    RX Peer Terminate Ack 0      TX Peer Terminate         2
    
    Neighbor Counters:
    RX Neighbor Up        0      TX Neighbor Up Ack        0
    RX Metric             0
    RX Neighbor Down      0      TX Neighbor Down Ack      0
    RX Neighbor Down Ack  0      TX Neighbor Down          0
    
    Exception Counters:
    RX Invalid Message    0      RX Unknown Message        0
    Pre-Existing Neighbor 0      Neighbor Resource Error   0
    Neighbor Not Found    0      Neighbor Msg Peer Not Up  0
    
    Timer Counters:
    Peer Heartbeat Timer         709
    Peer Terminate Ack Timer     2
    Neighbor Terminate Ack Timer 0
    Neighbor Activity Timer      0
    Radio Connect Timer          3
    
    Single Timer Wheel "Manet Infra Wheel"
    Granularity      = 250 msec
    Wheel size       = 4096
    Spoke index      = 8
    Tick count       = 24584
    Flags            = 0x00
    Active timers    = 1
    High water mark  = 2
    Started timers   = 1209
    Restarted timers = 4
    Cancelled timers = 14
    Expired timers   = 1190
    Long timers      = 0
    Long timer revs  = 0
    Timer suspends   = 0

The DLEP server is successfully configured in discovery mode and can communicate with DLEP clients. The verification commands display active client connections and communication statistics.

Use a DLEP template with a well-known IP address

Use this task to configure DLEP with a well-known IP address to enable standardized multicast communication between routers and radios using the RFC 8175 specification.

DLEP is based on RFC 8175 and uses the well-known IP address 224.0.0.117 on the server to communicate with radios. Additional prerequisites must be enabled for this configuration to work.

Procedure


Step 1

Use the ip multicast-routing distributed command to enable multicast routing on the router.

Example:

Router(config)# ip multicast-routing distributed

Step 2

Use these steps to configure the IPv4 address of the server:

  1. Use the interface type number command to enter interface configuration mode.

    Example:

    Router(config)# interface gi0/0/0
  2. Use the ip address ip-address subnet-mask command to assign an IP address and subnet mask to the interface.

    Example:

    Router(config-if)# ip address 10.1.2.3 255.255.255.0
  3. Use the ipv6 enable command to enable IPv6 support on the interface.

    Example:

    Router(config-if)# ipv6 enable
  4. Use the no shutdown command to bring up the interface.

    Example:

    Router(config-if)# no shutdown

Step 3

Use the ip pim sparse-dense-mode command to enable sparse-dense mode.

Example:

Router(config-if)# ip pim sparse-dense-mode

Step 4

Use these commands to enable the router to forward multicast traffic:

Example:

Router(config-if)# ip mfib cef in
                        Router(config-if)# ip mfib cef out
                        Router(config-if)# ip mfib forwarding in
                        Router(config-if)# ip mfib forwarding out

Step 5

Use the ip dlep vtemplate number well-known ip ip-address command to enable the DLEP virtual template to listen to multicast traffic.

Note

 
In the output of the show running-config command, this configuration is displayed as ip dlep vtemplate 1, which means that well-known ip 224.0.0.117 is hidden.

Example:

Router(config-if)# ip dlep vtemplate 1 well-known ip 224.0.0.117

Step 6

Use the show dlep clients command to validate the configuration.

Example:

Router# show dlep clients
                        
                        DLEP Clients for all interfaces:
                        DLEP Clients for Interface GigabitEthernet0/0/0
                        DLEP Server IP=10.1.2.3:55555 Sock=2
                        
                        DLEP Client IP=10.1.2.4:854 TCP Socket fd=3
                        Peer ID=1, Virtual template=1
                        Description: OONF DLEP Radio
                        Peer Timers (all values in milliseconds):
                        Heartbeat=5000, Dead Interval=10000, Terminate ACK=20000
                        Neighbor Timers (all values in seconds):
                        Activity timeout=0, Neighbor Down ACK=10
                        
                        Supported Metrics:
                        Link RLQ RX Metric : 100
                        Link RLQ TX Metric : 100
                        Link Resources Metric : 100
                        Link Latency Metric : 1000 microseconds
                        Link CDR RX Metric : 104857600 bps
                        Link CDR TX Metric : 104857600 bps
                        Link MDR RX Metric : 104857600 bps
                        Link MDR TX Metric : 104857600 bps

The DLEP template is configured with the well-known IP address, and multicast routing is enabled for communication with radios.

DLEP configuration with GTSM

Generalized TTL Security Mechanism (GTSM) can be used to provide an additional layer of security for the DLEP session.

Table 1. DLEP configuration modes

DLEP Configuration Mode

Command to attach DLEP template under WAN or sub-interface

DLEP template with TCP/UDP port based between server and client.

Router(config)# interface gi0/0/0
Router(config-if)# ip dlep vtemplate 1 port 11113 tcp port 11114 
gtsm client ip 10.0.0.3 port 11115

DLEP configuration with dynamic port on server.

Router(config)# interface gi0/0/0
Router(config-if)# ip dlep vtemplate 1 gtsm client ip 10.0.0.3 port 11115

DLEP template attach in discovery mode.

Router(config)# interface gi0/0/0 
Router(config-if)# ip dlep vtemplate 1 gtsm

DLEP template with well-known ip address.

Router(config)# interface gi0/0/0
Router(config-if)# ip dlep vtemplate 1 gtsm well-known ip 224.0.0.117

Configure DLEP with OSPFv3

Use this task to configure Dynamic Link Exchange Protocol (DLEP) with OSPFv3 to establish DLEP communication between routers and radio devices, enabling adaptive routing based on link characteristics.


Note


DLEP works only with the OSPFv3 or EIGRP routing protocols. This task uses OSPFv3.

Procedure


Step 1

Use the configure terminal command to enter the global configuration mode.

Example:

Router# configure terminal

Step 2

Use the ipv6 unicast-routing command to enable IPv6 unicast routing.

OSPFv3 IPv4 requires IPv6 support to be enabled at the interface level.

Example:

Router(config)# ipv6 unicast-routing

Step 3

Use these steps to configure the virtual multipoint interface (VMI):

  1. Use the interface vmi number command to create the VMI and enter interface configuration mode.

    Example:

    Router(config)# interface vmi 1
    Router(config-if)#
  2. Use the ip unnumbered interface command to configure the VMI to use the IP address of the physical interface.

    Example:

    Router(config-if)# ip unnumbered GigabitEthernet 0/0/0
  3. Use the physical-interface interface command to bind the physical interface to the VMI for packet flow.

    Example:

    Router(config-if)# physical-interface GigabitEthernet 0/0/0
  4. Use the ipv6 enable command to enable IPv6 support on the VMI.

    Example:

    Router(config-if)# ipv6 enable
  5. Use the ospfv3 process-id ipv4 area area-id command to enable the VMI to participate in OSPFv3 routing.

    Example:

    Router(config-if)# ospfv3 1 ipv4 area 0
  6. Use the exit command to return to global configuration mode.

    Example:

    Router(config-if)# exit

Step 4

Use these steps to configure the virtual template:

  1. Use the interface Virtual-Template number command to create the virtual template interface and enter interface configuration mode.

    You must use the same virtual template interface when you attach it to the physical interface.

    Example:

    Router(config)# interface Virtual-Template 1
    Router(config-if)#
  2. Use the ip unnumbered interface command to configure the virtual template interface to use the IP address of the physical interface.

    Example:

    Router(config-if)# ip unnumbered GigabitEthernet 0/0/0
  3. Use the ipv6 enable command to enable IPv6 support on the virtual template interface.

    Example:

    Router(config-if)# ipv6 enable
  4. Use the exit command to return to global configuration mode.

    Example:

    Router(config-if)# exit
    Router(config)#

Step 5

Use these steps to configure the WAN interface and attach the DLEP template:

  1. Use the interface type number command to enter interface configuration mode for the WAN interface.

    Example:

    Router(config)# interface gi0/0/0
    Router(config-if)#
  2. Use the ipv6 enable command to enable IPv6 support on the interface.

    Example:

    Router(config-if)# ipv6 enable
  3. Use the ip address ip-address subnet-mask command to assign an IP address to the WAN interface.

    Example:

    Router(config-if)# ip address 12.0.0.1 255.255.255.0
  4. Use the ip dlep vtemplate number port udp-port tcp port tcp-port client ip ip-address port client-port command to attach the DLEP template to the WAN interface.

    Example:

    Router(config-if)# ip dlep vtemplate 1 port 11117 tcp port 11115 client ip 12.0.0.2 port 859
  5. Use the no shutdown command to bring up the interface.

    Example:

    Router(config-if)# no shutdown
  6. Use the exit command to return to global configuration mode.

    Example:

    Router(config-if)# exit

DLEP is configured with OSPFv3, enabling DLEP communication between the router and radio devices for adaptive routing based on link characteristics.

Configure DLEP with EIGRP

Use this task to configure Dynamic Link Exchange Protocol (DLEP) with EIGRP to enable dynamic link metric updates and improved routing decisions in mobile network environments. This task creates a VMI, binds it to a physical interface, and enables the EIGRP routing protocol.

Perform this configuration when you need to integrate DLEP with EIGRP for dynamic routing metric adjustments based on radio link conditions.

Procedure


Step 1

Use the configure terminal command to enter the global configuration mode.

Example:

Router# configure terminal
                        Router(config)#

Step 2

Use the interface vmi number command to create the VMI and enter interface configuration mode.

Example:

Router(config)# interface vmi 1
                        Router(config-if)#

Step 3

Use the ip unnumbered interface command to configure the VMI to use the IP address of the physical interface.

Example:

Router(config-if)# ip unnumbered GigabitEthernet 0/0/0

Step 4

Use the physical-interface interface command to bind the physical interface to the VMI for packet flow.

Example:

Router(config-if)# physical-interface GigabitEthernet 0/0/0

Step 5

Use the ipv6 enable command to enable IPv6 support on the VMI.

Example:

Router(config-if)# ipv6 enable

Step 6

Use the no ip split-horizon eigrp as-number command to disable split horizon for the EIGRP process.

Example:

Router(config-if)# no ip split-horizon eigrp 1

Step 7

Use the exit command to exit interface configuration mode and return to global configuration mode.

Example:

Router(config-if)# exit
                        Router(config)#

Step 8

Use these steps to enable the global configuration for EIGRP:

  1. Use the router eigrp as-number command to enter router configuration mode.

    Example:

    Router(config)# router eigrp 1
                                    Router(config-router)#
  2. Use the router-id ip-address command to configure the router ID.

    Example:

    Router(config-router)# router-id 1.1.1.1
  3. Use the network ip-address wildcard-mask command to enable all the networks that can be part of EIGRP.

    Example:

    Router(config-router)# network 10.0.0.0 0.0.0.255

DLEP is configured with EIGRP, and the VMI is bound to the physical interface with EIGRP routing enabled for the specified network.

DLEP with quality of service (QoS)

Quality of Service (QoS) for DLEP needs to be configured on the Virtual-Template which is associated with the physical interface. QoS policy can be verified using the command sh policy-map interface Virtual-Access , as the actual data packets for DLEP will flow through the Virtual Access interfaces that will be created when DLEP neighbors come up.

Before proceeding, it is a good idea to familiarize yourself with content in the Quality of Service (QoS) Configuration Guide for IOS-XE.

DLEP QoS example

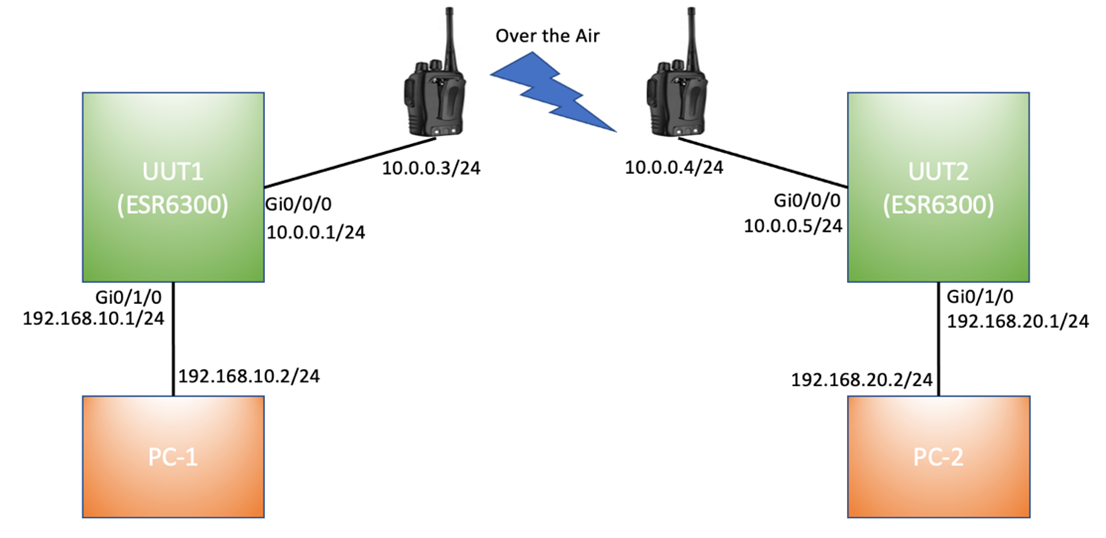
This figure shows an example topology for DLEP with QoS.

The figure illustrates a topology for DLEP with Quality of Service (QoS), highlighting the application of the QoS policy to the egress of the Virtual-Template connected to the WAN interface Gi0/0/0.

Based on above figure, the QoS policy is applied to egress of Virtual-Template attached to WAN interface Gi0/0/0.

UUT1 running configuration

UUT1# show running-config
Building configuration...

Current configuration : 7773 bytes
!
!
version 17.8
service timestamps debug datetime msec
service timestamps log datetime msec
service call-home
platform qfp utilization monitor load 80
platform punt-keepalive disable-kernel-core
!
hostname UUT1
!
boot-start-marker
boot system bootflash:/c6300-universalk9.SSA.bin
!
ipv6 unicast-routing
!
class-map match-any CMAP_VIDEO
 match dscp 33 
 match dscp 35 
 match dscp 37 
 match dscp 39 
 match dscp af41 
class-map match-any CMAP_VOICE
 match dscp 41 
 match dscp 43 
 match dscp 45 
 match dscp 47 
 match dscp 49 
class-map match-any CMAP_DATA
 match dscp 9 
 match dscp 11 
 match dscp 13 
 match dscp 15 
 match dscp af11 
!
policy-map Queue_Map
 class CMAP_VOICE
  bandwidth percent 40 
  set dscp af11
 class CMAP_VIDEO
  bandwidth percent 50 
 class CMAP_DATA
  bandwidth percent 10 
  set dscp af23
!
interface Loopback1
 ip address 1.1.1.1 255.255.255.255
 ipv6 enable
 ospfv3 1 ipv4 area 0
!
interface GigabitEthernet0/0/0
 ip address 10.0.0.1 255.255.255.0
 ip dlep vtemplate 1 port 11113 tcp port 11114 client ip 10.0.0.3 port 11115
 negotiation auto
 ipv6 address 1000::1/64
 ipv6 enable
!
interface GigabitEthernet0/0/1
 no ip address
 shutdown
 negotiation auto
!
interface GigabitEthernet0/1/0
 switchport access vlan 30
!
interface GigabitEthernet0/1/1
!
interface GigabitEthernet0/1/2
!
interface GigabitEthernet0/1/3
!
interface Virtual-Template1
 ip unnumbered GigabitEthernet0/0/0
 ipv6 enable
 service-policy output Queue_Map
!
interface Vlan1
 no ip address
!
interface Vlan30
 ip address 192.168.10.1 255.255.255.0
 ipv6 address 1010::1/64
 ipv6 enable
 ospfv3 1 ipv6 area 0
!
interface Async0/2/0
 no ip address
 encapsulation scada
!
interface vmi1
 ip unnumbered GigabitEthernet0/0/0
 ipv6 address FE80::7E31:EFF:FE85:1E78 link-local
 ipv6 enable
 ospfv3 1 ipv4 area 0
 physical-interface GigabitEthernet0/0/0
!
router ospfv3 1
 !
 router-id 1.1.1.1 
 address-family ipv4 unicast
 exit-address-family
!
end
UUT1#

Validation for DLEP QoS

For the above example, where QoS policy is applied to Virtual-Template1, data packets are flowing through Virtual-Access2 interface which is created when DLEP neighbors came up.


Note


The CLI show policy-map interface Virtual-Template1 will not show the stats.


UUT1#show policy-map interface Virtual-Template 1
 Virtual-Template1 
Service-policy output: Queue_Map

Service policy content is displayed for cloned interfaces only such as virtual access and sessions.

See the output for Virtual-Access 2:

UUT1#show policy-map interface Virtual-Access 2
Virtual-Access2
Service-policy output: Queue_Map

Class-map: CMAP_VOICE (match-any)
0 packets, 0 bytes
5 minute offered rate 0000 bps, drop rate 0000 bps
Match:  dscp 41
Match:  dscp 43
Match:  dscp 45
Match:  dscp 47
Match:  dscp 49
Queueing
queue limit 208 packets
(queue depth/total drops/no-buffer drops) 0/0/0
(pkts output/bytes output) 0/0
bandwidth 40% (400000 kbps)
QoS Set
dscp af11
Marker statistics: Disabled

Class-map: CMAP_VIDEO (match-any)
0 packets, 0 bytes
5 minute offered rate 0000 bps, drop rate 0000 bps
Match:  dscp 33
Match:  dscp 35
Match:  dscp 37
Match:  dscp 39
Match:  dscp af41 (34)
Queueing
queue limit 208 packets
(queue depth/total drops/no-buffer drops) 0/0/0
(pkts output/bytes output) 0/0
bandwidth 50% (500000 kbps)

Class-map: CMAP_DATA (match-any)
0 packets, 0 bytes
5 minute offered rate 0000 bps, drop rate 0000 bps
Match:  dscp 9
Match:  dscp 11
Match:  dscp 13
Match:  dscp 15
Match:  dscp af11 (10)
Queueing
queue limit 208 packets
(queue depth/total drops/no-buffer drops) 0/0/0
(pkts output/bytes output) 1024337/34827458
bandwidth 10% (100000 kbps)
QoS Set
dscp af23
Marker statistics: Disabled

Class-map: class-default (match-any)
0 packets, 0 bytes
5 minute offered rate 0000 bps, drop rate 0000 bps
Match: any

queue limit 208 packets
(queue depth/total drops/no-buffer drops) 0/0/0
(pkts output/bytes output) 0/0

Edit the virtual template

Before you begin

Before you edit the virtual template, remove the ip dlep vtemplate configuration from the WAN interface.

Use this task to modify virtual template interface configurations by creating or editing the interface and applying service policies for traffic management.

Virtual template interfaces are used to create virtual interfaces dynamically. Perform this configuration when you need to manage traffic policies on these interfaces.

Procedure


Step 1

Use the configure terminal command to enter the global configuration mode.

Example:

Router# configure terminal
Router(config)#

Step 2

Use the interface Virtual-Template number command to create the virtual template interface and enter interface configuration mode.

Example:

Router(config)# interface Virtual-Template 1
Router(config-if)#

Step 3

Use the service-policy {input | output} policy-map-name command to apply the policy map to the ingress or egress direction of the virtual template interface.

Example:

Router(config-if)# service-policy output Queue_Map

The virtual template interface is configured with the specified policy map applied for traffic management.

Configure DLEP on a sub-interface

Use this task to configure Dynamic Link Exchange Protocol (DLEP) on a sub-interface to enable dynamic link monitoring and management capabilities on a VLAN-tagged interface.

DLEP can also be configured on a sub-interface. This configuration is useful when you need to implement DLEP functionality on specific VLAN segments rather than on the main physical interface.

Procedure


Step 1

Use these interface commnds:

  1. Use the interface type number command to select the WAN interface, and then use the no shutdown command to bring it to the active state.

    Example:

    Router(config)# interface gi0/0/0
    Router(config-if)# no shutdown
  2. Use the interface type number.subinterface-number command to create the sub-interface.

    Example:

    Router(config-if)# interface gi0/0/0.2

Step 2

Use the encapsulation dot1q vlan-id native command to add 802.1Q encapsulation over the VLAN and configure it as the native VLAN.

Example:

Router(config-subif)# encapsulation dot1q 2 native

Step 3

Use these commands to assign and enable IPv4 and IPv6 addresses:

  1. Use the ip address ip-address subnet-mask command to assign an IPv4 address to the sub-interface.

    Example:

    Router(config-subif)# ip address 10.0.0.1 255.255.255.0
  2. Use the ipv6 enable command to enable IPv6 support on the sub-interface.

    OSPFv3 IPv4 requires IPv6 support to be enabled at the interface level.

    Example:

    Router(config-subif)# ipv6 enable

Step 4

Use the interface vmi number command to create the virtual multipoint interface (VMI) and enter interface configuration mode.

Example:

Router(config-subif)# interface vmi 1
Router(config-if)#

Step 5

Use the ip unnumbered interface command to configure the VMI to use the IP address of the physical interface.

Example:

Router(config-if)# ip unnumbered GigabitEthernet 0/0/0.2

Step 6

Use the physical-interface interface command to bind the physical interface to the VMI for packet flow.

Example:

Router(config-if)# physical-interface GigabitEthernet 0/0/0.2

Step 7

Use the ipv6 enable command to enable IPv6 support on the VMI.

OSPFv3 IPv4 requires IPv6 support to be enabled at the interface level.

Example:

Router(config-if)# ipv6 enable
  1. Use the interface type number.subinterface-number command to return to the sub-interface configuration to add the DLEP template.

    Example:

    Router(config-if)# interface gi0/0/0.2

Step 8

Use the ip dlep vtemplate number gtsm client ip-address command to attach the DLEP template to the sub-interface.

Example:

Router(config-subif)# ip dlep vtemplate 1 gtsm client 10.0.0.2
  1. Use the exit command to exit sub-interface configuration mode and return to global configuration mode.

    Example:

    Router(config-subif)# exit
    Router(config)#

Step 9

Use these steps to enable the global configuration for EIGRP:

  1. Use the router eigrp as-number command to enter router configuration mode.

    Example:

    Router(config)# router eigrp 1
  2. Use the router-id ip-address command to configure the router ID.

    Example:

    Router(config-router)# router-id 1.1.1.1
  3. Use the network ip-address wildcard-mask command to specify the network.

    Example:

    Router(config-router)# network 10.0.0.0 0.0.0.255

DLEP is successfully configured on the sub-interface with the associated VMI and routing protocol configuration. The sub-interface is ready to handle DLEP communications.

The following is an example of the running configuration:

Router# show running-config
        Building configuration...
        Current configuration : 7726 bytes
        !
        !
        version 17.8
        hostname Router
        !
        boot-start-marker
        boot system bootflash:/c6300-universalk9.SSA.bin
        boot-end-marker
        !
        ipv6 unicast-routing
        subscriber templating
        !
        license udi pid ESR-6300-CON-K9 sn FOC234304H3
        license boot level network-advantage
        !
        interface Loopback1
        ip address 1.1.1.1 255.255.255.255
        ipv6 enable
        ospfv3 1 ipv4 area 0
        !
        interface GigabitEthernet0/0/0
        no ip address
        negotiation auto
        !
        interface GigabitEthernet0/0/0.10
        encapsulation dot1Q 10
        ip address 10.0.0.1 255.255.255.0
        ip dlep vtemplate 1 port 11113 tcp port 11114 client ip 10.0.0.2 port 11115
        ipv6 enable
        !
        interface Virtual-Template1
        ip unnumbered GigabitEthernet0/0/0.10
        !
        interface vmi1
        ip unnumbered GigabitEthernet0/0/0.10
        ipv6 address FE80::7E31:EFF:FE85:1E78 link-local
        ipv6 enable
        ospfv3 1 network manet
        ospfv3 1 ipv4 area 0
        physical-interface GigabitEthernet0/0/0.10
        !
        router ospfv3 1
        !
        address-family ipv4 unicast
        exit-address-family
        !
        address-family ipv6 unicast
        exit-address-family
        !
        end

Remove the DLEP configuration

Use this task to remove the DLEP configuration so that you can edit the virtual template or VMI interface configurations without encountering configuration conflicts.

Before you edit or remove any configuration related to the virtual template or the VMI, you must remove the DLEP virtual template configuration attached to the WAN interface or sub-interface. If you attempt to edit the VMI or the virtual template, the following messages are displayed:

Router(config)# interface vmi1
  vmi1 is associated with an instance of DLEP running on GigabitEthernet0/0/0.
Please remove DLEP configuration before making any changes to the VMI configuration.
Router(config)# interface Virtual-Template1
Virtual-Template1 is associated with an instance of DLEP running on GigabitEthernet0/0/0.
Please remove DLEP configuration before making any changes to the virtual-template.

Procedure


Step 1

Use the configure terminal command to enter the global configuration mode.

Example:

Router# configure terminal
Router(config)#

Step 2

Use the interface type number command to enter interface configuration mode for the interface on which DLEP is configured.

Example:

Router(config)# interface gi0/0/0

Step 3

Use the no ip dlep vtemplate number command to detach the DLEP configuration.

Example:

Router(config-if)# no ip dlep vtemplate 1

Step 4

Use the no interface vmi number command to remove the VMI from the router.

Example:

Router(config-if)# no interface vmi 1

Step 5

Use the no interface Virtual-Template number command to remove the virtual template from the router.

Example:

Router(config-if)# no interface Virtual-Template 1

DLEP is removed from the router. However, the virtual access interfaces that were created when the DLEP neighbors came up continue to appear in the output of the show ip interface brief command until the system is rebooted.

Configure DLEP using the WebUI

Use this task to configure Dynamic Link Exchange Protocol (DLEP) on physical interfaces, sub-interfaces, and virtual templates using the web user interface (WebUI), and to monitor DLEP neighbors and clients.

DLEP configuration allows for dynamic management of network links. The WebUI provides a graphical interface for configuring DLEP on different interface types, including physical interfaces, sub-interfaces, and virtual templates.

The following images illustrate how to configure DLEP using the WebUI.

Procedure


Step 1

To configure DLEP on a physical interface, navigate to Configuration > Interface > Ethernet, select the interface to configure, apply the DLEP virtual template, and then click Update & Apply to Device.

Step 2

To configure DLEP on a sub-interface, navigate to Configuration > Interface > Ethernet, select the sub-interface to configure, apply the DLEP virtual template, and then click Update & Apply to Device.

Example:

Step 3

Use these steps to configure the virtual template:

  1. Navigate to Configuration > Interface > Logical and select the Virtual-Template tab.

    From this tab, you can add, edit, or delete interfaces.

    Example:

  2. Click Add to add a virtual template, or select an existing virtual template and click Edit.

    Example:

    The Add Virtual Interface window appears.

  3. Click Apply to Device.

Step 4

Use these steps to configure the virtual multipoint interface (VMI):

  1. Navigate to Configuration > Interface > Logical and select the VMI tab.

    From this tab, you can add, edit, or delete interfaces.

    Example:

  2. Click Add to add a VMI, or select an existing VMI and click Edit.

    Example:

    The Add VMI window appears.

  3. Click Apply to Device.

Step 5

To monitor DLEP, navigate to Monitoring > General > DLEP.

Two tabs are available for monitoring neighbors or clients. The Neighbors tab displays information equivalent to the show dlep neighbors command. The Clients tab displays information equivalent to the show dlep clients command.

Step 6

Use these steps to monitor DLEP neighbors:

  1. On the Neighbors tab, select the interface.

    Example:

  2. Open the interface to view the details.

    Example:

Step 7

To monitor DLEP clients, select the interface on the Clients tab and open it to view the details.

The Clients tab works in the same manner as the Neighbors tab.

Example:


DLEP is successfully configured on the selected interfaces, and monitoring capabilities are available through the WebUI. You can now monitor DLEP neighbors and clients through the monitoring interface.

DLEP validation commands

This section contains examples of how to verify the DLEP configuration on the router.

DLEP configuration

Command

Information

Router# show dlep config ?
  GigabitEthernet  GigabitEthernet IEEE 802.3z
  |                Output modifiers
  <cr>             <cr>

DLEP configuration is supported only on WAN or sub-interface.

Router# show dlep config g0/0/1
DLEP Configuration for GigabitEthernet0/0/1

DLEP Peer Description - 
DLEP Version = RFC 8175
DLEP Server IP=10.0.0.1:11117
DLEPv27 TCP Port = 11118
Virtual template=2
Timers (all values are in seconds):
Missed heartbeat threshold=2, Peer Terminate ACK timeout=10
Dlepv27 Applicable configs(in seconds):
Heartbeat interval=5, Discovery interval =5, Session Ack timeout=10
Neighbor activity timeout=0, Neighbor Down ACK timeout=10

DLEP clients

Command

Information

Router# show dlep clients ?
  GigabitEthernet  GigabitEthernet IEEE 802.3z
  |                Output modifiers
  <cr>             <cr>

DLEP clients is supported only on WAN or sub-interface.

Router# show dlep clients
DLEP Clients for all interfaces:


DLEP Clients for Interface GigabitEthernet0/0/1
DLEP Server IP=10.0.0.1:11117 Sock=0 --> Local Router IP address


DLEP Client IP=10.0.0.2:859 TCP Socket fd=1 --> Directly connected Radio to the router
Peer ID=2, Virtual template=2
Description: DLEP_RadioSIM2
Peer Timers (all values in milliseconds):
  Heartbeat=5000, Dead Interval=10000, Terminate ACK=20000
Neighbor Timers (all values in seconds):
  Activity timeout=0, Neighbor Down ACK=10

Supported Metrics:
  Link RLQ RX Metric : 100
  Link RLQ TX Metric : 100
  Link Resources Metric : 100
  Link MTU Metric : 100
  Link Latency Metric : 250 microseconds
  Link CDR RX Metric : 100000000 bps
  Link CDR TX Metric : 100000000 bps
  Link MDR RX Metric : 100000000 bps
  Link MDR TX Metric : 100000000 bps
Router#

DLEP neighbor

Command

Information

Router# show dlep neighbor ?
  GigabitEthernet  GigabitEthernet IEEE 802.3z
  |                Output modifiers
  <cr>             <cr>

DLEP neighbors is supported only on WAN or sub-interface.

Router# show dlep neighbor
DLEP Neighbors for all interfaces:

DLEP Neighbors for Interface GigabitEthernet0/0/1
DLEP Server IP=10.0.0.1:11117 Sock=0   ---> Local Router IP address

SID=2151  MAC_Address=a453.0e94.f861 
  Addresses:
  IPv4 : 16.0.0.1           ---> Mac-Address and IPv4 address of neighbor's end-point device
Supported Metrics:
  RLQ RX Metric : 100
  RLQ TX Metric : 100
  Resources Metric : 100
  MTU Metric : 1500
  Latency Metric : 250 microseconds
  CDR RX Metric : 100000000 bps
  CDR TX Metric : 100000000 bps
  MDR RX Metric : 100000000 bps
  MDR TX Metric : 100000000 bps

DLEP counters

Command

Information

Router# show dlep counters ?
  GigabitEthernet  GigabitEthernet IEEE 802.3z
  |                Output modifiers
  <cr>             <cr>

DLEP Counters is supported only on WAN or sub-interface, which will summarize port information, counters for peer, and neighbors.

UUT1# show dlep counters
DLEP Counters for GigabitEthernet0/0/1

Last Clear Time = 

DLEP Version = RFC 8175
DLEP Server IP=10.0.0.1:11117
DLEPv5 TCP Port = 11118

Peer Counters:
RX Peer Discovery     0      TX Peer Offer             0     
 RX Peer Offer         0      TX Peer Discovery         0     
 RX Peer Init          0      TX Peer Init Ack          0     
 RX Peer Init Ack      1      TX Peer Init              1     
 RX Heartbeat          41     TX Heartbeat              41    
 RX Peer Terminate     0      TX Peer Terminate Ack     0     
 RX Peer Terminate Ack 0      TX Peer Terminate         0     

Neighbor Counters:
RX Neighbor Up        1      TX Neighbor Up Ack        1     
 RX Metric             0     
 RX Neighbor Down      0      TX Neighbor Down Ack      0     
 RX Neighbor Down Ack  0      TX Neighbor Down          1     

Exception Counters:
RX Invalid Message    0      RX Unknown Message        0     
 Pre-Existing Neighbor 0      Neighbor Resource Error   1     
 Neighbor Not Found    0      Neighbor Msg Peer Not Up  0     

Timer Counters:
Peer Heartbeat Timer         41    
 Peer Terminate Ack Timer     0     
 Neighbor Terminate Ack Timer 0     
 Neighbor Activity Timer      0     
 Radio Connect Timer          5     

Single Timer Wheel "Manet Infra Wheel"
  Granularity      = 250 msec
  Wheel size       = 4096
  Spoke index      = 3730
  Tick count       = 3423890
  Flags            = 0x00
  Active timers    = 1
  High water mark  = 1
  Started timers   = 171177
  Restarted timers = 2
  Cancelled timers = 5
  Expired timers   = 171169
  Long timers      = 0
  Long timer revs  = 0
  Timer suspends   = 0

Optional configurations for DLEP

There are set of optional commands that are available to configure for the ip DLEP CLI under the WAN or sub-interface. Based on those commands, you can define the set of timeout intervals between peers, neighbors, and how long to send heart-beat intervals to radio's.

Command

Purpose

ip dlep set heartbeat-threshold ?
  <2-8>  Threshold of missed heartbeat messages

Set the heartbeat-threshold, between Server and Client.

ip dlep set nbr-activity-timeout ?
  <0-240>  Neighbor Activity timer duration in seconds

Set the neighbor activity timeout.

ip dlep set nbr-down-ack-timeout ?
  <1-50>  Neighbor Down ACK timer duration in seconds

Set the neighbor acknowledgment timeout.

ip dlep set peer-description ? 
  LINE  Peer Description Name

Defines the description with Peer.

ip dlep set peer-heartbeat-interval ? 
  <1-60>  Peer Heartbeat Interval timer duration in seconds

Set the heartbeat interval between Server and client.

ip dlep set peer-discovery-interval ? 
  <1-60>  Peer Discovery Interval timer duration in seconds

Set the peer discovery interval timer.

ip dlep set peer-init-ack-timeout ? 
  <1-60>  Peer Init ACK timer duration in seconds

Set the peer with init acknowledge messages from client.

ip dlep set peer-terminate-ack-timeout ? 
  <1-50>  Peer Terminate ACK timer duration in seconds

Set the peer terminate acknowledge timer between client and server.

Restrictions for DLEP IPv6 unicast

DLEP deployment restrictions

Previous releases of IOS XE offered support for IPv4 unicast traffic over an IPv4 DLEP session. IOS XE 17.12.1a provides support for IPv6 unicast over an IPv4 DLEP session.

  • Multicast traffic is not supported with DLEP, but is supported with PPPOE.

  • DLEP cannot be deployed with High Availability (HA) configuration.

  • You must configure the VMI and Virtual-Template before attaching the Virtual-Template to a physical interface.

  • The ESR6300 is connected over DLEP radio links and only 1 radio per interface (WAN port only) is supported.

  • All configurations for the virtual-template need to be removed individually using the no form of the respective configuration commands, before removing the virtual-template using the no interface virtual-template command.

  • Changing of configurations on the virtual-template and VMI interfaces is not supported while DLEP is enabled on the physical interface. In order to make such changes, disable DLEP by removing the DLEP configuration from the physical interface, make the changes, and re-configure DLEP on the physical interface.

  • DLEP interface does not support Jumbo frames (frames > 1500 bytes in size).

  • Routing of internally generated application traffic (e.g. pingv6) with source as DLEP VMI / physical interface is not supported.

  • Viewing information about DLEP neighbors using the show ipv6 neighbor command is not supported.

This section provides a subset of the overall DLEP information that is found in the IP Routing Configuration Guide, Cisco IOS XE 17.x.

IPv4 and IPv6 multicast over DLEP

DLEP Multicast is now supported with IOS XE 17.13.1. See the configuration examples for IPv4 and IPv6 multicast implementation.

IPv4 multicast

Global Command Examples:

ip multicast-routing distributed
ip pim rp-address <rp ip addr>  [access-list for group]

Physical Interface Command Examples:

interface GigabitEthernet0/0/1
  ip address 28.28.28.1 255.255.255.0
  ip pim sparse-mode
  ip igmp version 3
  negotiation auto
  ipv6 address 1111::3/120
ipv6 enable

VMI Command Examples:

interface vmi 5
ip pim sparse-mode

Loopback Command Examples:

interface Loopback0
ip address 7.7.7.7 255.255.255.255
ip pim sparse-mode
ipv6 address 2000::2/128
ipv6 enable

IPv6 multicast

Global Command Examples:

ipv6 pim 
ipv6 multicast-routing
ipv6 pim rp-address <rp ipv6 addr> [access-list for group]

Physical Interface Command Examples:

interface GigabitEthernet0/0/2
ip address 38.38.38.1 255.255.255.0
ip igmp version 3
ipv6 mld version 2
negotiation auto
ipv6 address 1111::3/120
ipv6 enable
ipv6 pim register-source loopback0

VMI Command Examples:

interface vmi 5
ip pim sparse-mode

Loopback Command Examples:

interface Loopback0
ip address 7.7.7.7 255.255.255.255
ip pim sparse-mode
ipv6 address 2000::2/128
ipv6 enable

Remove commands

Remove Command Examples:

Router(config-if)# no ip dlep vtemplate 1
Router(config-if)# no int vmi 1
Router(config-if)# no int Virtual-Template 1

Show commands

Show Command Examples:

show ip interface brief
show dlep config
show dlep clients
show dlep neighbors

IPv6 control plane for DLEP

IPv6 control plane for DLEP is a network capability that

  • enables DLEP control plane session support on IPv6 networks

  • allows routers to initiate DLEP session setup over IPv6 when both router and radio run IPv6 stack, and

  • supports both manual mode and auto discovery mode for session establishment.

Configuration modes

Manual mode session setup occurs when the router is configured with an IPv6 address and transport layer port details of listening radio, enabling the router to initiate DLEP session setup.

DLEP client and neighbor clearing

DLEP client and neighbor clearing is a network management process that

  • terminates active DLEP peer sessions between routers and radios using specific CLI commands

  • handles session teardown through message exchanges or automatic timeout mechanisms, and

  • provides granular control over individual client connections and neighbor relationships.

Command operation details

When the clear DLEP client command is issued on a router, the router sends a "Session Termination" message to the radio. The radio responds to this message by sending a "Session Termination Response" message. When the router receives the "Session Termination Response" message, it tears down the peer session.

When the radio is stopped gracefully, and after the clear DLEP client command is issued on the router, the router will still send "Session Termination" message to the radio, but it won't be received by the radio, since it is already turned off. The router will automatically tear down the peer session after the timeout (heartbeat timer expiry) is reached.

There is another clear DLEP command that can be used. The clear DLEP neighbor <interface> <session ID> CLI will clear DLEP neighbors. The session ID can be obtained from show DLEP neighbor command.

DLEP client clearing example


Note


First obtain the Peer ID from the output of the show DLEP client CLI. Then, use that as the input to the clear DLEP client CLI.
Router#show dlep client gi0/0/1

DLEP Clients for Interface GigabitEthernet0/0/1
DLEP Local IP=15.0.0.10:55555 Sock=0


DLEP Local Radio IP=15.0.0.2:856 TCP Socket fd=1
Peer ID=20, Virtual template=2
Description: DLEP_Radio_2042
Peer Timers (all values in milliseconds):
Heartbeat=60000, Dead Interval=120000, Terminate ACK=240000
Neighbor Timers (all values in seconds):
Activity timeout=0, Neighbor Down ACK=10

Supported Metrics:
Link RLQ RX Metric : 100
Link RLQ TX Metric : 100
Link Resources Metric : 100
Link MTU Metric : 100
Link Latency Metric : 250 microseconds
Link CDR RX Metric : 100000000 bps
Link CDR TX Metric : 100000000 bps
Link MDR RX Metric : 100000000 bps
Link MDR TX Metric : 100000000 bps
Router#

Router#clear dlep client gi0/0/1 20
DLEP: Clear Client (peer) peer_id=20 from 15.0.0.10
Router#clear dlep neighbor gi0/0/1 2215
DLEP: Clear neighbor sid=2215 from 195.0.0.2 

Troubleshoot with show commands

This series of figures illustrates what the output of various show commands mean in a sample installation.

Figure 4. Sample installation
The figure illustrates the output of various show commands in a sample DLEP installation, providing context for troubleshooting and configuration verification.
Figure 5. Show DLEP configuration
The DLEP configuration output displays the current settings and parameters for the DLEP protocol in a sample installation, aiding in troubleshooting efforts.
Figure 6. Show DLEP clients
The output of the show command displays a list of DLEP clients connected to the network, including their status and associated details.
Figure 7. Show DLEP neighbors
The Show DLEP neighbors command output displays a list of neighboring devices, including their IP addresses and connection statuses, to assist in troubleshooting DLEP configurations.
Figure 8. Show DLEP counters
The image displays the DLEP counters, illustrating the current statistics and metrics related to DLEP operations, which are essential for troubleshooting and monitoring network performance.

Troubleshoot with debug commands

This section provides procedures to resolve DLEP client reachability issues and session timeout problems using diagnostic commands.

Scenario 1: DLEP client is not reachable

In this scenario, the router is not running in discovery mode, and the client/radio attributes have been explicitly configured.

Router# show dlep clients
                DLEP Clients for all interfaces:
                DLEP Clients for Interface GigabitEthernet0/0/1
                DLEP Server IP=14.0.0.3:11117 Sock=-1
Router# show dlep config
                DLEP Configuration for GigabitEthernet0/0/1
                DLEP Peer Description - 
                DLEP Version = RFC 8175
                DLEP Server IP=14.0.0.3:11117
                DLEPv27 TCP Port = 11118
                Virtual template=2
                Timers (all values are in seconds):
                Missed heartbeat threshold=2, Peer Terminate ACK timeout=10
                Dlepv27 Applicable configs(in seconds):
                Heartbeat interval=60, Discovery interval =5, Session Ack timeout=10
                Neighbor activity timeout=0, Neighbor Down ACK timeout=10
                Router# show run int g0/0/1
                Building configuration...
                Current configuration : 245 bytes
                !
                interface GigabitEthernet0/0/1
                ip address 14.0.0.3 255.255.255.0
                ip dlep set peer-heartbeat-interval 60
                ip dlep vtemplate 2 port 11117 tcp port 11118 client ip 14.0.0.6 port 859
                negotiation auto
                ipv6 address 1111::1/120
                ipv6 enable
                end

Verify that the configuration on the radio (client) matches the configuration on the router (server) and that the router can reach the radio.

Router# show ip arp
                Protocol  Address          Age (min)  Hardware Addr   Type   Interface
                Internet  10.199.184.2            9   0013.5f22.0b4a  ARPA   GigabitEthernet0/0/0
                Internet  10.199.184.3            8   0018.7414.4e80  ARPA   GigabitEthernet0/0/0
                Internet  10.199.184.19           -   a453.0e94.f638  ARPA   GigabitEthernet0/0/0
                Internet  14.0.0.2                4   000c.297a.6b3d  ARPA   GigabitEthernet0/0/1
                Internet  14.0.0.3                -   a453.0e94.f639  ARPA   GigabitEthernet0/0/1
                Internet  14.0.0.6                0   Incomplete      ARPA   
                Router# ping 14.0.0.6
                Type escape sequence to abort.
                Sending 5, 100-byte ICMP Echos to 14.0.0.6, timeout is 2 seconds:
                ...
                Success rate is 0 percent (0/3)

The ping to client 14.0.0.6 failed. A check of the radio configuration revealed that the client IP address was 14.0.0.2. Correct the client IP address and verify the fix.

Router# conf t
                Router(config)# int g0/0/1
                Router(config-if)# no ip dlep vtemplate 2 port 11117 tcp port 11118 client ip 14.0.0.6 port 859
                Router(config-if)# ip dlep set peer-heartbeat-interval 60
                Router(config-if)# ip dlep vtemplate 2 port 11117 tcp port 11118 client ip 14.0.0.6 port 859
                Router(config-if)# ^Z

Scenario 2: DLEP session keeps timing out

In this scenario, the router is running in discovery mode and the DLEP session flaps.

Router# show dlep clients
                DLEP Clients for all interfaces:
                DLEP Clients for Interface GigabitEthernet0/0/1
                DLEP Server IP=14.0.0.3:55555 Sock=0
                DLEP Client IP=14.0.0.2:859 TCP Socket fd=1
                Peer ID=13, Virtual template=2
                Description: DLEP_RadioSIM2

Turn on the following debug commands to troubleshoot:

debug dlep server
                debug dlep timer detail
                debug dlep client error
                debug dlep client infra
                debug dlep client packet detail
                debug dlep client state

The debug logs indicate a connection error. An examination of the DLEP config reveals that the heartbeat on the router is set to 5 seconds, while the radio is set to 60 seconds. Change the heartbeat to 60 seconds to resolve the timeout.

Router# conf t
                Router(config)# int g0/0/1
                Router(config-if)# no ip dlep
                Router(config-if)# no ip dlep vtemplate
                Router(config-if)# ip dlep set peer-heartbeat-interval 60
                Router(config-if)# ip dlep vtemplate 2
                Router(config-if)# ^Z

Additional debug commands

These commands are available for troubleshooting purposes.


Note


We recommend using debug commands only when under the guidance of Cisco TAC.


DLEP

debug dlep server detail
debug dlep timer detail
debug dlep neighbor error
debug dlep neighbor infrastructure detail
debug dlep neighbor infrastructure error
debug dlep neighbor metrics
debug dlep neighbor state
debug dlep neighbor all
debug dlep client error
debug dlep client infrastructure
debug dlep client packet dump
debug dlep client packet detail
debug dlep client state

VMI

debug vmi bma
debug vmi packet
debug vmi error
debug vmi multicast 
debug vmi neighbor
debug vmi registries

Virtual template

debug vtemplate cloning
debug vtemplate error
debug vtemplate  event
debug vtemplate subinterface

PPPOE

debug pppoe errors
debug pppoe events
debug pppoe packets
debug pppoe data

SSS

debug sss error
debug sss event

Related documentation

This reference identifies external documentation and technical standards relevant to the implementation and understanding of radio aware routing.

Additional information can be found in the following resources:

Radio Aware Routing is discussed in this Cisco white paper .

Internet Engineering Task Force (IETF) RFC 8175